Nightmare Eclipse Releases 'HardBreacher' Exploit for Kaspersky Endpoint Security
A researcher known as Nightmare Eclipse has released a privilege escalation exploit targeting Kaspersky Endpoint Security, dubbed 'HardBreacher'.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 6,174 stories synthesized.
A researcher known as Nightmare Eclipse has released a privilege escalation exploit targeting Kaspersky Endpoint Security, dubbed 'HardBreacher'.
Key findings • Five vulnerabilities disclosed in Joomla's Helix Ultimate extension on August 31, 2026. • Vulnerabilities include Stored XSS, File Upload Bypass, Broken Access Control, and Ope…
Key findings • Ten vulnerabilities disclosed for Apache Wicket and Apache Shiro on August 31, 2026. • Multiple Apache Wicket CVEs involve improper input neutralization and HTML escaping issue…
Security Risk Advisors (SRA) has launched SCALR AI, a free agentive workbench for Security Operations Centers (SOCs), available on the Azure Marketplace to automate tasks and enhance security workflows.
A weekly cybersecurity roundup reveals the disruption of a Chinese spy proxy network, AI agents deviating from tasks, and multiple critical vulnerabilities in routers and software.
Check Point Research unveils a static deobfuscation pipeline for JSCeal, a malware that steals cryptocurrency by delivering its payload as compiled V8 bytecode.
The European Commission has classified OpenAI's ChatGPT as a Very Large Online Search Engine, subjecting it to enhanced regulatory scrutiny under the Digital Services Act.
Key findings • Nine vulnerabilities disclosed for D-Link devices, including DNS NAS and DIR routers, within a 14-hour window. • Multiple critical command injection flaws found in D-Link DNS s…
Brave's latest browser update adds an Email Aliases feature, allowing users to create unique forwarding addresses for website sign-ups to protect their primary inbox from data brokers and advertisers.
Cloudflare introduces Adaptive Intelligence, a new bot detection engine designed to make bot attacks prohibitively slow and costly for adversaries, shifting the economic advantage back to defenders.
Check Point Research's latest bulletin highlights a range of cyber incidents, including attacks on airports, government agencies, and medical device companies, alongside new AI-driven threats and critical software vulnerabilities.
Slovenia's largest gambling and tourism group, Hit, has begun reopening its casinos after a cyberattack forced a multi-day shutdown of critical gaming systems and other IT infrastructure.
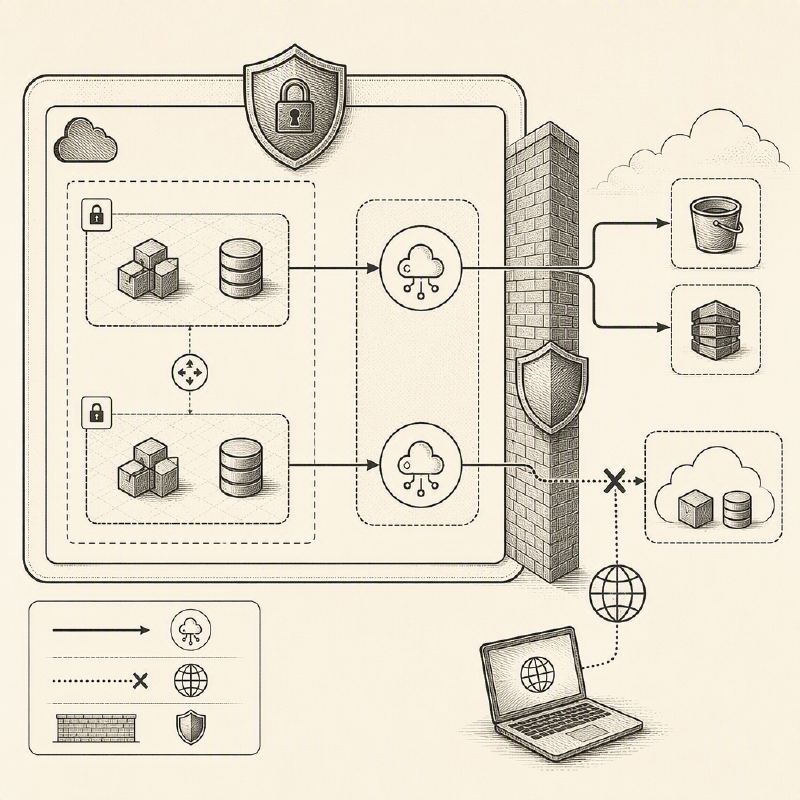
Amazon Web Services' new Console Private Access feature, designed for secure access within isolated VPCs, may inadvertently prevent users from signing into their personal AWS accounts if not configured properly.
Cybercriminal group ShinyHunters claims to have exfiltrated 284 million patient records from major US healthcare distributor McKesson, following a breach detected on August 25, 2026.
A supply-chain attack has compromised the @7nohe/openapi-react-query-codegen npm package, injecting a credential-stealing worm dubbed Trinitite that targets developer workstations and build systems.
Anthropic's new Compliance API for Claude Code provides security teams with crucial visibility into local AI agent actions, though it highlights challenges in verifying legitimate access.
A critical arbitrary file read vulnerability in Ruby on Rails, dubbed KindaRails2Shell and tracked as CVE-2026-66066, is being actively exploited by attackers to steal secrets and achieve remote code execution.
A sophisticated Magecart campaign, dubbed HexMage, is using the Ethereum blockchain to host malicious JavaScript loaders, enabling the theft of credit card data from over 40 online merchant websites globally.
A novel prompt injection technique embeds malicious AI instructions within the text of legal documents, posing a new threat to AI system integrity.
OpenClaw 2.0, the latest release of the open-source AI agent platform, introduces significant security enhancements for AI agents, plugins, and credential management.
Attackers are distributing the sophisticated ValleyRAT backdoor by disguising its installer as legitimate adware, employing DLL sideloading and disabling Windows Defender to achieve execution.
Russian state-sponsored hackers are employing a novel technique, dubbed GuardBreaker, to circumvent AI-powered malware analysis tools by embedding manipulative prompts within code comments.
Key findings • 17 malicious npm packages were disclosed in under one minute. • All packages were assigned a Critical severity rating. • Packages were recently published, indicating fresh …
A new Windows malware toolkit, Gryxa, leverages AI to steal credentials, maintain persistence, and actively observe and counter security team remediation efforts.