What you need to know today.
Critical flaws across multiple vendors including IBM, Microsoft, Tenda, Wavlink, TOTOLINK, and WordPress plugins expose users to RCE, privilege escalation, and data breaches.
AI coding agents are inadvertently deploying unpatchable servers, creating persistent security risks as they select outdated software packages.
A review found NHS staff faced severe emotional distress and inadequate support while managing a helpline following a data breach that exposed sensitive health information of over 8,000 individuals.
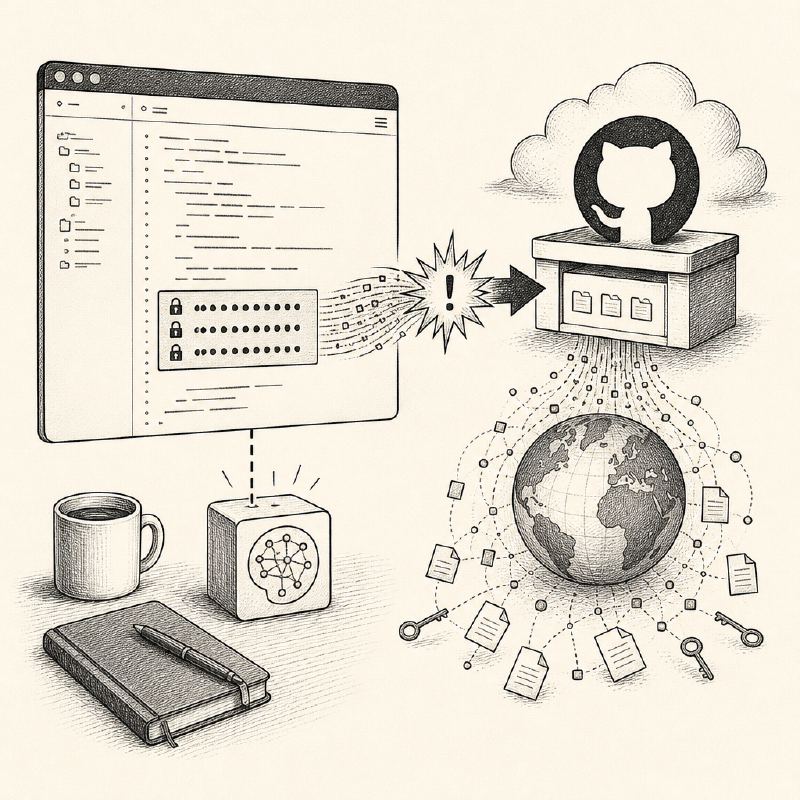
A flaw in Anthropic's Claude Code allows the AI assistant's 'Yes, and don't ask again' feature to inadvertently commit passwords and API keys to public GitHub repositories.
Insignary has launched a free, read-only tool, insignary-chk, to help organizations detect exposure to critical PHP2Shell and Node2Shell vulnerabilities, both of which are actively exploited and have been added to CISA's KEV catalog.
New research reveals AI agents are susceptible to social engineering, readily sharing sensitive tokens and running malicious code when prompted by other agents, posing significant security risks.
CISA has added CVE-2026-19868, a critical SonicWall SonicOS SSLVPN vulnerability, to its Known Exploited Vulnerabilities (KEV) Catalog due to evidence of active exploitation.
Perry Johnson Companies has agreed to a $300,000 settlement and must implement significant cybersecurity reforms following a 2023 breach that exposed the protected health information of over 13 million individuals.
Japan has announced a 10 billion yen ($63 million) emergency cybersecurity package, including AI and cyber rescue teams, to combat a recent wave of major data breaches affecting companies and government agencies.
Vendors are increasingly using enterprise incident archives to train AI models, creating new avenues for sensitive data exposure and security procedure compromise.

Storm-2603 hackers are exploiting vulnerabilities in Microsoft SharePoint, specifically targeting the ToolShell component. This allows them to deploy fileless backdoors and conduct ransomware attacks. The attackers are leveraging CVE-2025-53770, CVE-2025-53771, and CVE-2025-6264 to achieve their objectives. Cyber Security News
Adversaries are increasingly using the vulnerability ecosystem against defenders, as highlighted by CrowdStrike. This includes exploiting CVE-2024-55591, CVE-2026-31431, and CVE-2026-41940. CrowdStrike Blog
SonicWall has issued a warning regarding the potential in-the-wild exploitation of a critical SSLVPN flaw that bypasses multi-factor authentication. This vulnerability, tracked as CVE-2024-53704 and others including CVE-2026-107154, CVE-2026-107155, CVE-2026-19703, CVE-2026-19868, CVE-2026-77708, CVE-2026-77709, and CVE-2026-82308, poses a significant risk to organizations relying on SonicWall devices. Cyber Security News
Synology NAS devices are being targeted in ransomware attacks that exploit a patched flaw in the DiskStation Manager (DSM). The vulnerabilities in question include CVE-2021-28799, CVE-2024-10441, CVE-2024-10445, and CVE-2024-50629. The Hacker News
Barracuda Email Security Gateway devices are vulnerable to an authentication bypass flaw that allows for pre-auth remote root access. This critical vulnerability, affecting CVE-2023-2868, CVE-2026-111560, and CVE-2026-116606, could enable attackers to gain complete control of the affected systems. The Hacker News
PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request. Some contexts may not properly account for this scenario and leave request memory in an uninitialized state before performing an allocation. The subsequent request…
Improper input validation vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway. This issue affects ADC: before 14.1-73.37, before 13.1-64.23, before 14.1-73.37 FIPS, and before 13.1.37.279 FIPS and NDcPP; Gateway: before 14.1-73.37 and before 13.1-64.23 leading…
A buffer overflow vulnerability in the Brotli decoder (c/dec/decode.c) in Google Brotli versions 1.0.3 through 1.2.0 on all platforms allows a remote unauthenticated attacker to corrupt adjacent decoder state memory, disclose sensitive memory contents, cause a denial of service,…
GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.8, 19.3 before 19.3.5, and 19.4 before 19.4.2 that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary code on the GitLab server via a specially…
The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the origin of the messages it received. Under the right conditions, this could allow an attacker to perform file operations on the appliance.
In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU grace period tcp_v4_syn_recv_sock() transfers ownership of ireq->ireq_opt to the child socket (newinet->inet_opt) without copying it. Another cpu can concurrently…
Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as the zammad user. The bug is also present in version 7.0.0 to version 7.1.2, but not exploitable due to changes in the underlying framework.
The Secure Custom Fields WordPress plugin before 6.9.8 does not sanitize a persisted field definition before emitting part of it as an HTML attribute name, allowing a user able to configure its fields to store a payload that executes as JavaScript in the browser of any user who…
The Secure Custom Fields WordPress plugin before 6.9.8 does not perform a read-permission check when it renders and formats the values of its relational fields, allowing users with post-editing access (Contributor and above) to disclose the titles and non-public statuses of…
The Secure Custom Fields WordPress plugin before 6.9.8 does not verify that a user is allowed to edit the target object before writing to it during bidirectional relationship synchronization, allowing users with contributor-level access and above to add or remove a reference to…
The Secure Custom Fields WordPress plugin before 6.9.8 does not re-apply its field-group location rules when persisting values submitted through the post editor save path, allowing users with contributor-level access and above to write custom fields the site restricted to…
The Pie Register WordPress plugin through 3.8.4.15 does not perform an authorisation check in one of its AJAX actions, allowing users with a role as low as contributor to modify existing administrator-created invitation-code records.
The Pie Register WordPress plugin through 3.8.4.15 does not perform any capability, nonce or authentication check on one of its request handlers, allowing unauthenticated attackers to reset the Pie Register WordPress plugin through 3.8.4.15's settings to their defaults…
The FV Flowplayer Video Player WordPress plugin before 7.5.57.7212 does not perform any authorization check on an AJAX action that carries out a site-wide content rewrite, so any authenticated user, including subscriber-level, can trigger a bulk modification of posts they should…