Siemens Desigo Controllers Vulnerable to Denial-of-Service Attacks
Siemens Desigo DXR and PXC controllers are susceptible to denial-of-service vulnerabilities, potentially disrupting critical building automation systems.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,304 stories synthesized.
Siemens Desigo DXR and PXC controllers are susceptible to denial-of-service vulnerabilities, potentially disrupting critical building automation systems.
Multiple vulnerabilities in Siemens License Server versions prior to V5.1 and V5.3 could allow attackers to escalate privileges and access sensitive files.
Siemens Parasolid software contains a critical out-of-bounds read vulnerability that could allow attackers to crash the application or execute arbitrary code.
Flock Safety is implementing stricter privacy measures, including mandatory audit features and a seven-day data retention limit, following reports of law enforcement misuse of its surveillance technology.
GitHub Security Lab's Secure Open Source Fund invested over $500,000 in 50 projects to address AI-driven security challenges, pairing maintainers with experts and tools to accelerate vulnerability triage and response.
A new variant of the notorious Mirai botnet has emerged, featuring encrypted command-and-control communications and a sniffer to detect devices with default credentials, increasing its stealth and effectiveness.
Key findings • 25 vulnerabilities disclosed for Rsync versions prior to 3.5.0 on August 13, 2026. • Multiple vulnerabilities include heap corruption, path traversal, and DoS conditions. •…
The White House has launched a new initiative to leverage private cybersecurity expertise for offensive cyber operations against foreign criminal organizations.
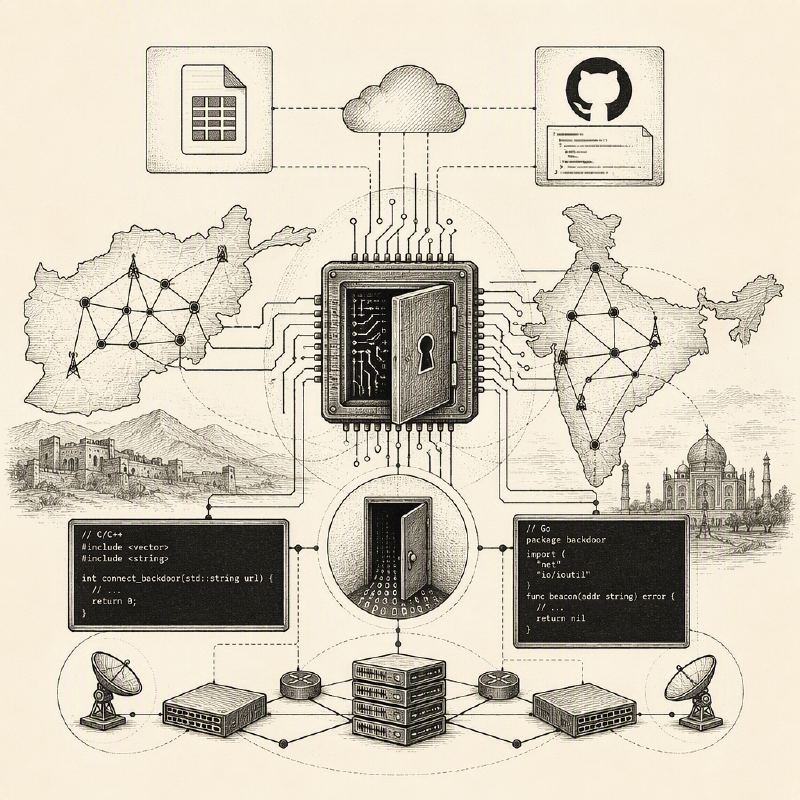
A sophisticated campaign is deploying a new C/C++ backdoor named PATCHCORD against Afghan telecom providers and South Asian critical infrastructure, with a related Go-based backdoor, SHEETCORD, targeting Indian government networks.
Organizations are increasingly misunderstanding Microsoft's role in data recovery, leaving them vulnerable to ransomware and data loss due to the shared responsibility model.
Google Cloud has unveiled its strategy for transitioning to quantum-resistant cryptography, setting a 2027 target for its initial major milestone to counter future threats.
A critical vulnerability in VMware vCenter Server, allowing for remote code execution, is being actively exploited by attackers just five days after Broadcom released security advisories.
A data breach at Trezor's third-party logistics provider, ShipMonk, has exposed the personal information of over 13,000 hardware wallet customers, increasing their risk of phishing and social engineering attacks.
A new macOS infostealer, AmnesiaStealer, is spreading via a convincing fake GitHub download page, using social engineering to hijack browser sessions and gain live control.
Key findings • 25 CVEs disclosed for PostgreSQL on August 13, 2026, with multiple High-severity flaws. • Arbitrary code execution is possible via authorization bypass, type confusion, and buf…
Cloudflare's Certificate Transparency Monitoring service is now generally available, enhancing its ability to detect mis-issued TLS certificates by filtering out routine renewals.
Check Point Research's latest report indicates a significant increase in active ransomware groups, while the 'The Gentlemen' operation demonstrates AI's role in rapid development of malicious tools.
Key findings • Ten vulnerabilities disclosed for Flowise on August 13, 2026, impacting versions prior to 3.1.3 and 3.1.4. • Multiple critical vulnerabilities allow for remote code execution a…
Researchers have identified over 6,300 internet-exposed building automation controllers near U.S. data centers, posing a significant risk to critical cooling and power systems.
North Korean IT workers are increasingly infiltrating government and corporate systems by posing as legitimate remote employees, a tactic that the FBI is actively investigating.
Cisco Talos has identified the JWR phishing framework, a sophisticated platform that uses encrypted WebSockets for real-time operator control over victim sessions, targeting extensive personal and financial data.
A sophisticated APT group, dubbed 'Jewelbug,' is conducting both state-sponsored espionage and cryptocurrency theft operations using a unified web panel, researchers have discovered.
Over 3,000 lawsuits alleging intentional design of addictive and harmful features for minors are proceeding against major tech companies after a key appeals court ruling.
SpecterOps has released Blacklight, an open-source toolkit designed to identify sensitive data left behind by AI coding agents on developer workstations.