research2 sources
Attackers Use Personal Phones for Microsoft 365 Account Takeovers via Vishing
Cybercriminals are impersonating IT staff to trick employees into revealing Microsoft 365 credentials by calling their personal phones.
Sep 10, 2026

Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 6,130 stories synthesized.
Cybercriminals are impersonating IT staff to trick employees into revealing Microsoft 365 credentials by calling their personal phones.
The MantaxOtax Android malware has emerged as a sophisticated dual-threat, combining file encryption for ransom with extensive data exfiltration capabilities, targeting Indonesian users.
Cloudflare's 1.1.1.1 DNS resolver now validates DNSSEC signatures using ML-DSA-44, a post-quantum algorithm, preparing the internet's infrastructure for future quantum threats.
Tenable has unveiled its 'agentic harness,' a control layer designed to safely integrate AI agents into security operations by treating them as untrusted insiders.
Researchers have analyzed a sophisticated RedTail Linux payload found on a DShield honeypot, revealing its ability to masquerade as legitimate processes and support multiple hardware architectures.
A new vulnerability, 'Workflow Identity Hijacking,' allows attackers to exfiltrate sensitive enterprise data by exploiting authorization gaps in AI workflows, bypassing traditional security measures.
Multiple critical vulnerabilities in the open-source AI gateway LiteLLM could allow attackers to execute code as root and steal sensitive cloud credentials.
Check Point has released patches for two critical vulnerabilities, CVE-2026-85102 and CVE-2026-85103, both rated CVSS 9.8 and capable of unauthenticated remote code execution.
Threat actors are leveraging DCSync attacks to impersonate Active Directory domain controllers and steal password hashes, bypassing traditional security measures.
Two critical vulnerabilities in Cisco Secure Firewall Management Center (FMC) software are being actively exploited by nation-state actors, including Sandworm, and ransomware groups like Qilin.
Healthcare provider AdaptHealth has disclosed a data breach impacting approximately 4.1 million individuals, with sensitive personal, health, and insurance data compromised.

Key findings • Six vulnerabilities disclosed on September 10, 2026, affect Joomla extensions SP Property and T4 Page Builder. • Critical SQL injection (CVE-2026-78082) and XSS (CVE-2026-78082…
A critical buffer overflow vulnerability in Palo Alto Networks' PAN-OS, CVE-2026-0310, enables unauthenticated attackers to achieve root-level code execution on PA-Series firewalls.

Key findings • 40 malicious npm packages were disclosed in a coordinated attack. • All advisories were published within a tight four-minute window on September 10, 2026. • Packages exhibi…

New AI capabilities allow exploit discovery from mere rumors, challenging traditional security embargo practices and necessitating faster response protocols.
CISA has added three critical vulnerabilities affecting Cisco, Citrix, and Fortinet products to its Known Exploited Vulnerabilities catalog, demanding federal agencies apply patches by September 12, 2026.

OpenAI has developed an automated cybersecurity system, dubbed the 'Defense Factory,' that uses AI agents to continuously find, validate, and fix software vulnerabilities.

WordPress.org has implemented an automated security review system using AI to scan all new plugin releases, automatically blocking those identified as potential risks before they reach users.

Researchers have detailed a post-exploitation technique allowing attackers with root access on a Kubernetes node to misuse SPIFFE/SPIRE metadata and impersonate co-located workloads.

Scammers are exploiting Instagram's copyright reporting system to temporarily suspend user accounts and demand cryptocurrency for their reinstatement.

Cybercriminals are exploiting the immense anticipation for Grand Theft Auto VI by distributing malware-laden ISO files disguised as leaked game downloads.
Key findings • 23 CVEs disclosed on 2026-09-10 for Geovision GV-LPC2211, impacting V1.13 and V1.14. • Multiple vulnerabilities allow for remote code execution as root via various input manipu…
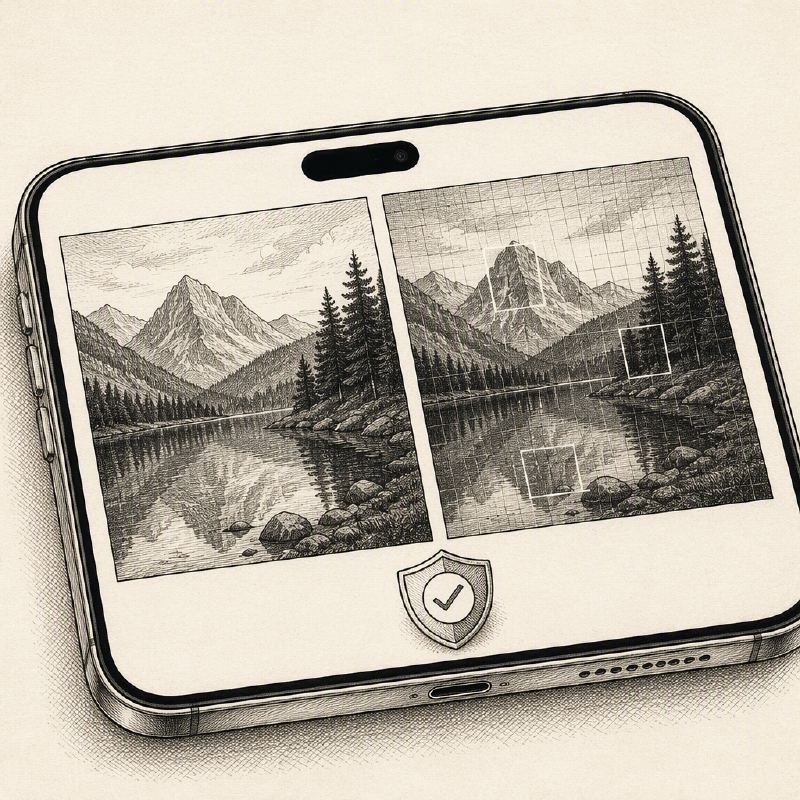
Apple's new opt-in 'Reference Image' feature for iPhone 18 Pro aims to combat image manipulation by creating an unalterable digital negative of photos at the sensor level.
The cybersecurity landscape in 2026 sees endpoint encryption management, not the encryption engines themselves, as the primary focus for businesses seeking robust data protection and compliance.