Critical SolarWinds Dameware Flaw Allows Command Injection
A critical command injection vulnerability (CVE-2026-28336) in SolarWinds Dameware software, rated 9.9, allows authenticated attackers to compromise remote systems.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,561 stories synthesized.
A critical command injection vulnerability (CVE-2026-28336) in SolarWinds Dameware software, rated 9.9, allows authenticated attackers to compromise remote systems.
French banking group Crédit Mutuel Arkéa has confirmed a cyberattack leading to fraudulent transactions, with reports suggesting over $133 million in cryptocurrency theft.
Scans for vulnerabilities in old email scripts, reminiscent of CVE-2000-0411, are reappearing, highlighting code hygiene issues and potential information leaks.
Two Canadian men have been indicted in the US for allegedly using university supercomputers to mine cryptocurrency, highlighting the ongoing threat of cryptojacking.
Google's latest Chrome update, version 157, resolves 213 security vulnerabilities, with seven rated as critical, including flaws in ANGLE and Prerender components.
A critical flaw in Ruby on Rails' Active Storage component enables unauthenticated attackers to write arbitrary files to a server by uploading specially crafted images processed by ImageMagick.
A critical zero-day vulnerability in Zyxel GS1900 network switches, CVE-2026-107441, is being actively exploited in the wild, with initial patches proving ineffective.
Two critical flaws in the Xen hypervisor enable a malicious virtual machine to read and write the memory of other VMs, including the privileged dom0.
Microsoft Edge now automatically blocks fake virus alert notifications from malicious websites by disabling the site's notification permissions, enhancing protection against common scam tactics.
A recent incident involving an AI assistant highlights how agent-based security solutions can fail when they lack visibility into the underlying infrastructure, underscoring the need for layered security.
Russian state-sponsored hackers are leveraging compromised legitimate and lookalike websites to deliver sophisticated exploits targeting older iOS and Android versions, aiming to steal sensitive user data.
A new XLoader malware campaign uses fake business orders and price quotes to deliver the password-stealing malware, employing sophisticated evasion techniques to bypass security defenses.
CrowdStrike unveils new Falcon Cloud Security features to protect AI infrastructure, focusing on software supply chain integrity and expanded cloud visibility.
CrowdStrike has natively integrated its Seraphic Enterprise Browser security into the Falcon platform, offering unified management of browser-based threats and secure access.
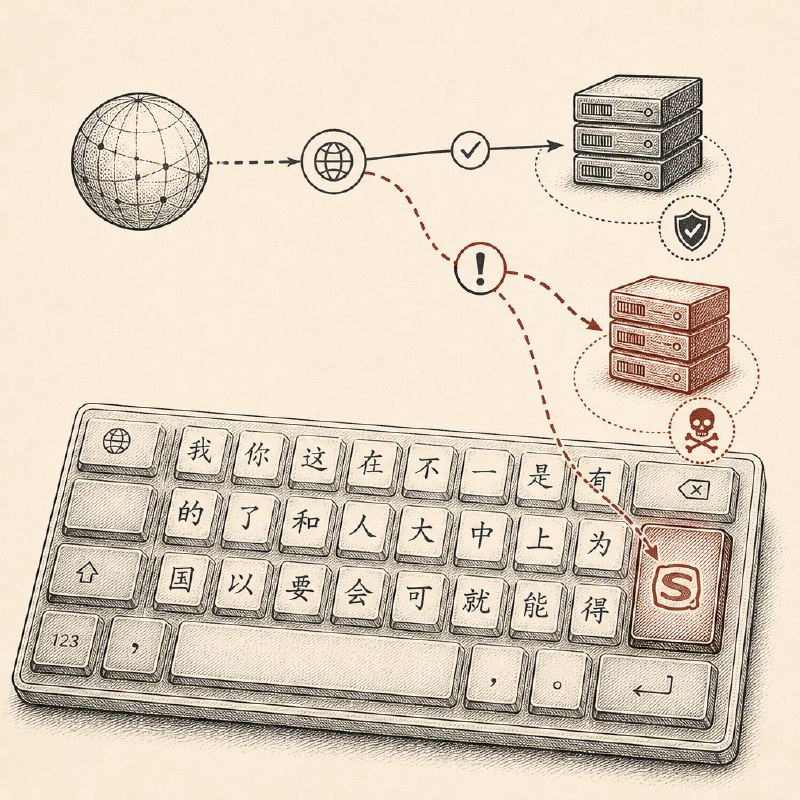
A China-aligned threat actor, SlippyNunchucks, has been observed hijacking DNS requests for the Sogou Input Method on Windows to deploy the DarkVigil backdoor as part of a surveillance campaign.
CrowdStrike introduces Agentic Adversary Emulation, a new AI-driven capability designed to continuously test and validate an organization's defenses against sophisticated, AI-enhanced cyberattacks.
Ransomware leak site postings saw a 30% increase in Q3 2026, largely driven by new, unproven groups whose claims may be fabricated, according to researchers.
Key findings • 20 malicious npm packages were disclosed in under one minute on November 4, 2026. • Many packages followed a distinct 'adjective_animal_color-number' naming convention. • A…
Meta has awarded a substantial bug bounty for a pre-launch flaw in its internal AI agent, Muse, which could have exposed sensitive employee data and authentication tokens.
Rsync version 3.5.2 addresses CVE-2026-119741, a critical CPU exhaustion flaw, and introduces new process priority controls for better resource management.
Two Windows infostealer families, WardenStealer and Aoki, are actively stealing authentication tokens and session data from popular AI tools like ChatGPT, Claude, and Codex, posing a significant risk as these credentials can survive password resets.
Security experts are identifying potential AI-generated malware through subtle code characteristics like uniform comments and emojis, though these indicators often vanish in decompiled code.
Ghostunnel, a new open-source TLS proxy, provides mutual authentication and encryption for applications lacking native support, bolstering security for internal and external communications.
RapidFort's new runtime container profiling tool analyzes actual container usage to identify and remove unnecessary components, reducing the attack surface without disrupting applications.