Malware Infection Exposes Attackers' Toolkit, Infrastructure
A security investigation uncovered the tools and infrastructure of a Blind Eagle-linked campaign after an operator's workstation was compromised by a separate information-stealer.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,564 stories synthesized.
A security investigation uncovered the tools and infrastructure of a Blind Eagle-linked campaign after an operator's workstation was compromised by a separate information-stealer.
Key findings • Six high-severity SQL injection vulnerabilities disclosed for Itsourcecode Online Medicine Delivery System 1.0 on August 31, 2026. • Seven medium-severity SQL injection vulnera…
A new report indicates that AI-powered application security tools agree on only 5% of identified security findings, while adversaries probe average applications every four minutes.
A critical out-of-bounds write vulnerability in pdfforge PDF Architect's file parsing component enables remote code execution, requiring only user interaction with a malicious file or webpage.
Key findings • 25 vulnerabilities disclosed across Ash Project components (ash_phoenix, ash_admin, ash_ai, ash_graphql, ash_cloak). • Critical code injection vulnerability (CVE-2026-77956) in…
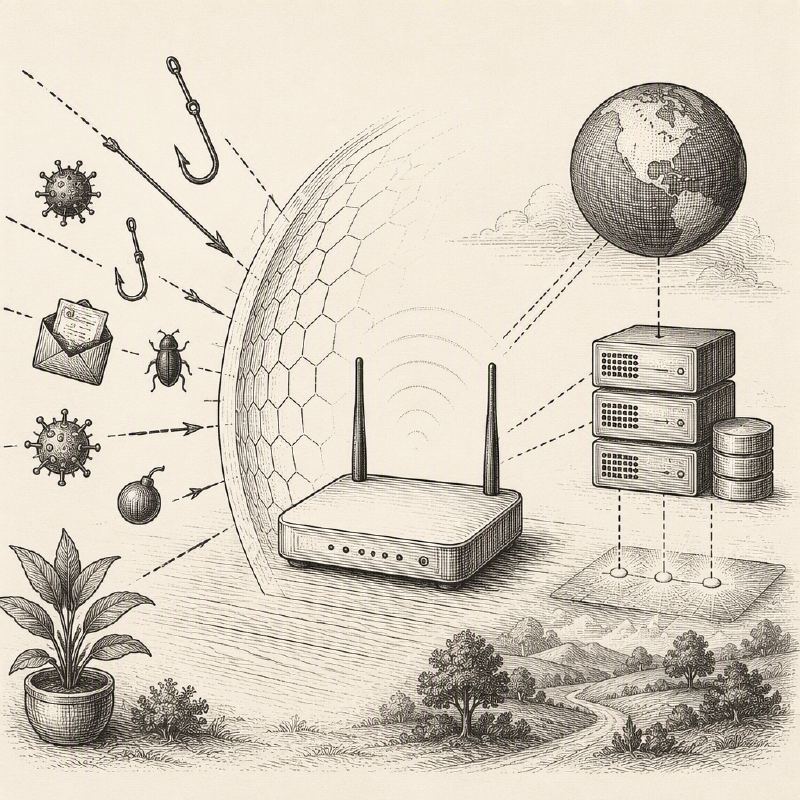
A simple change to a home router's DNS settings can provide a free, network-wide layer of defense against malware and phishing attacks.
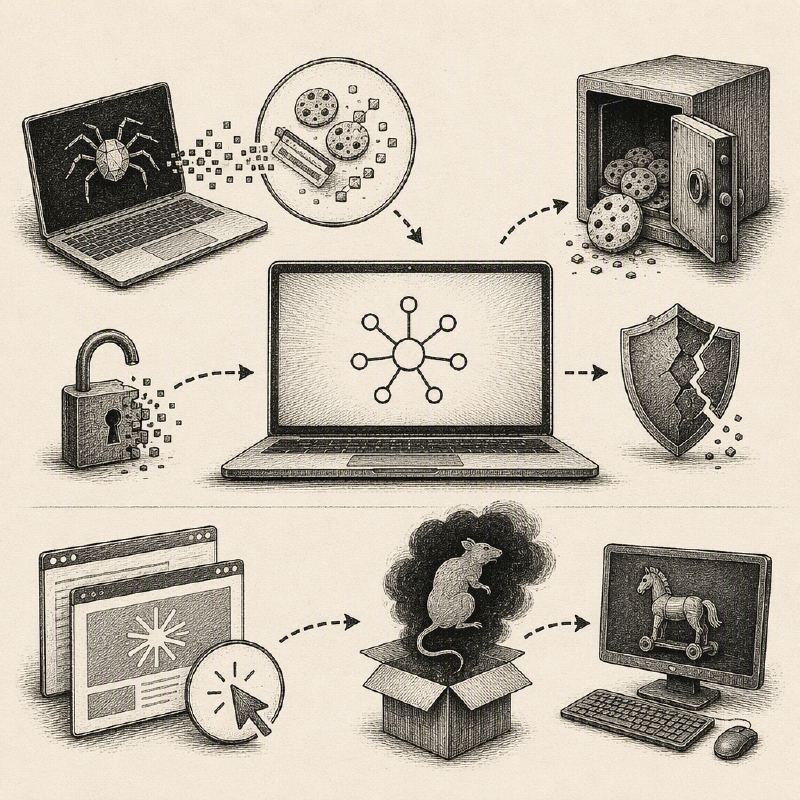
Infostealer malware is targeting Anthropic's Claude AI platform, stealing session cookies to bypass MFA and hijack user accounts, while a separate attack uses malicious Claude ads to deploy RATs.
Key findings • Four SQL injection vulnerabilities disclosed together for Itsourcecode Sales and Inventory System 1.0. • All vulnerabilities affect version 1.0 and are triggered by manipulatin…
Key findings • 25 WordPress plugins disclosed with vulnerabilities between August 29-30, 2026. • Multiple critical vulnerabilities include authentication bypass, RCE, and privilege escalation…
The YARA-X project has released version 1.20.0, introducing a new option to ignore invalid rules, while the core YARA tool has seen multiple patch releases addressing numerous bugs.
Key findings • 40 malicious npm packages were disclosed. • All advisories were published within a one-minute window on August 29, 2026. • All 40 packages were assigned a Critical severity…
OpenAI is terminating its AI model supply to the coding assistant Cursor, citing concerns that Elon Musk's companies, including SpaceX and xAI, have violated its terms of service by using its technology to train competing systems.
Multiple popular WordPress plugins and themes harbor critical vulnerabilities, including authentication bypass, privilege escalation, and remote code execution flaws, potentially impacting hundreds of thousands of sites.
Toy and game giant Hasbro has disclosed a data breach impacting employee personal information, following earlier disruptions caused by a cyberattack.
Malvertising campaigns are increasingly sophisticated, shifting from deceptive ad content to complex, multi-stage redirect chains and cloaking techniques that hide malicious activity.
Microsoft details the TerminalFix campaign, a sophisticated multi-stage attack using compromised websites, steganography, and reverse tunnels to gain persistent network-level proxy access.
Key findings • 19 malicious npm packages were disclosed simultaneously at 03:31 UTC on August 29, 2026. • All packages were assigned a Critical severity rating. • The burst included both …
Key findings • 40 malicious npm packages were disclosed on August 29, 2026. • All advisories were published within a single minute at 00:31 UTC. • 10 of the packages shared the grafeno- p…
Key findings • 40 malicious npm packages disclosed within an 18-minute window on August 28, 2026 • High-profile package @7nohe/openapi-react-query-codegen (151k weekly downloads) was compromi…
Key findings • 20 vulnerabilities disclosed across MongoDB Connector for BI, multiple drivers, and core services. • High-severity flaws include memory-safety issues, authentication bypass, an…
Key findings • Ten vulnerabilities disclosed in TP-Link devices between August 24-28, 2026, including high-severity command injection and DoS flaws. • Multiple Archer routers vulnerable to co…
Key findings • 25 incorrect access control vulnerabilities disclosed for Totolink T6 router on August 28, 2026. • All flaws affect firmware version 4.1.5cu.748_B20211015, allowing unauthentic…
Key findings • 16 vulnerabilities disclosed across multiple IBM products on August 28, 2026. • IBM Langflow OSS is heavily impacted with eight vulnerabilities, including critical code executi…
Key findings • Eight vulnerabilities disclosed simultaneously for IBM Langflow OSS, impacting versions 1.0.0 through 1.11.1. • Critical flaws include arbitrary code execution and OS command i…