Microsoft Azure Entra ID OAuth Vulnerability Exposes Sensitive Information
A critical vulnerability in Microsoft Azure Entra ID's OAuth Device Code Grant allows unauthenticated remote attackers to disclose sensitive organizational information.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 6,135 stories synthesized.
A critical vulnerability in Microsoft Azure Entra ID's OAuth Device Code Grant allows unauthenticated remote attackers to disclose sensitive organizational information.
A denial-of-service vulnerability in Backblaze Personal Computer Backup allows local attackers with low-privileged code execution to overwrite arbitrary files and crash the service.
Google Chrome 153 addresses 230 vulnerabilities, including CVE-2026-87491, a medium-severity out-of-bounds write in the V8 engine exploited in the wild.
Key findings • Eleven Huawei vulnerabilities disclosed on September 9, 2026, span graphics, input, and permission control modules. • High severity flaws include DoS in input device module (CV…
BleachBit 6.0.4 resolves a significant bug in its secure file deletion feature on Windows, ensuring that fragmented files are now completely overwritten.
Key findings • 16 vulnerabilities disclosed simultaneously in Tanium Comply on September 9, 2026. • Flaws include improper access controls, SQL injection, path traversal, and unauthorized cod…
Key findings • Google Chrome 153.0.8010.36 patches 25 vulnerabilities disclosed on September 9, 2026. • Batch includes critical flaws like buffer overflows, use-after-free, and out-of-bounds …
Key findings • 25 vulnerabilities in Chromium disclosed on September 9, 2026, patched in Chrome 153.0.8010.36. • Batch includes critical flaws like use-after-free, out-of-bounds writes, and t…
Key findings • CVE-2026-19490, a Netscaler vulnerability, has been added to CISA KEV due to active exploitation. • The flaw poses an immediate and significant risk to organizations using affe…
Key findings • CVE-2026-20079, a Cisco vulnerability, added to CISA KEV on September 9, 2026. • The vulnerability is confirmed to be under active exploitation by threat actors. • Immediat…
Key findings • Google vulnerability CVE-2026-87491 added to CISA KEV catalog. • The flaw is confirmed to be under active exploitation in the wild. • No ransomware association has been rep…
Key findings • Fortinet vulnerability CVE-2025-25249 confirmed actively exploited. • Added to CISA's Known Exploited Vulnerabilities (KEV) catalog on September 9, 2026. • Organizations mu…
Key findings • 17 CVEs disclosed together for N8n on September 8, 2026, spanning multiple components. • High severity vulnerabilities include expression engine flaws, sanitizer bypass, and in…
Microsoft's September 2026 Patch Tuesday addresses a record 974 vulnerabilities, including two zero-days under active exploitation, highlighting the growing challenge of patch management.
Key findings • Adobe Acrobat Reader patched 18 CVEs on September 8, 2026, including multiple high-severity flaws. • Flaws include Use After Free, Heap Overflow, and Type Confusion, potentiall…
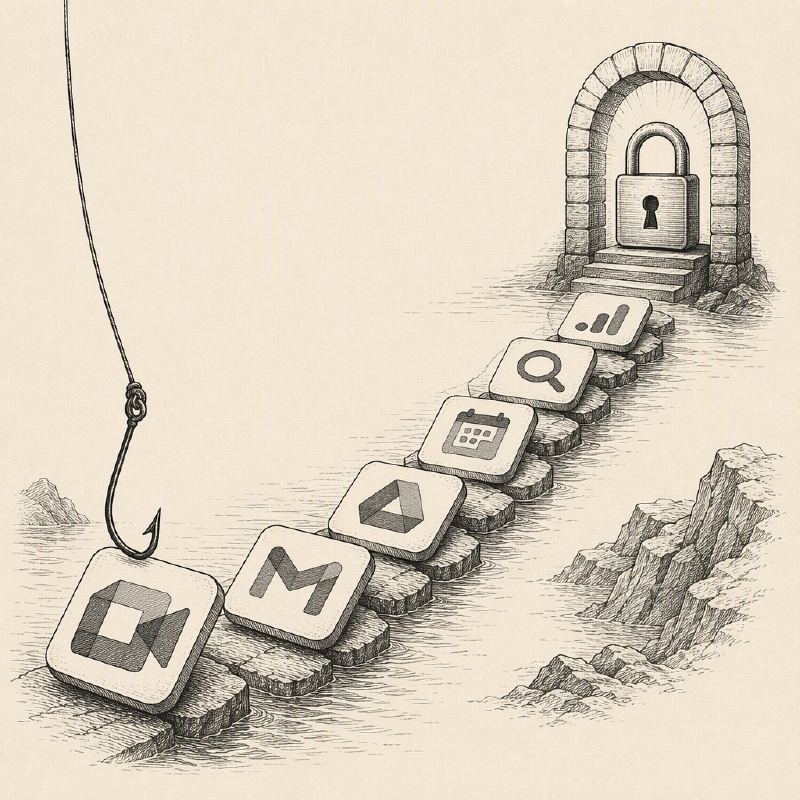
Cybercriminals are chaining Google services to bypass security filters in phishing campaigns that deliver credential harvesting or remote access trojans.
Key findings • Adobe Experience Manager: 25 CVEs disclosed on Sept 8, 2026, primarily XSS vulnerabilities. • Batch includes stored XSS, DOM-based XSS, and an improper input validation flaw. …
CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, citing evidence of active exploitation and urging prioritized patching.
A Russian national extradited from Georgia faces 11 federal charges in Atlanta for his alleged role in a large-scale bank account takeover conspiracy that defrauded U.S. banks of millions.
US agencies warn that China-based AI companies are systematically extracting proprietary functionalities from US AI models through large-scale knowledge distillation campaigns, posing a threat to US technological leadership.
Key findings • 25 vulnerabilities disclosed simultaneously for Android-x86 on September 8, 2026. • Critical flaws (CVSS 9.8) like CVE-2026-58822 and CVE-2026-49921 allow for remote code execu…
Enterprise AI agents are susceptible to manipulation via hidden instructions and poisoned data, bypassing traditional security controls and enabling undetected alterations to AI decisions.
Federal agencies are urged to adopt an offense-driven cybersecurity approach, shifting from reactive patching to real-time prioritization based on exploitability and active threats.
Key findings • Microsoft patched 25 Windows vulnerabilities on September 8, 2026, including one Critical and multiple High severity flaws. • CVE-2026-69768, a Critical heap-based buffer overf…