ShinyHunters Claims Florida DMV Hack, N-able Patches Critical RCE Flaw
The ShinyHunters threat group claims a breach of Florida's DMV, while N-able rushes a patch for a critical zero-day in its N-central platform.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,191 stories synthesized.
The ShinyHunters threat group claims a breach of Florida's DMV, while N-able rushes a patch for a critical zero-day in its N-central platform.
A Ukrainian national involved in the prolific Conti ransomware group has been sentenced to four years in prison for his role in developing malware and extorting victims.
Apple's new 'Live Rewind' feature on the Apple Watch Series 12 can record 15-second audio snippets of conversations without explicit consent from all parties, raising privacy and legal issues.
A new report from Anthropic indicates that artificial intelligence is enabling smaller threat actors to conduct sophisticated, state-level cyber operations, blurring the lines between amateur and nation-state capabilities.
Wordfence Intelligence's latest weekly report, covering August 31 to September 6, 2026, identifies 269 vulnerabilities across 182 WordPress plugins and 7 themes, with a significant portion rated as Medium or High severity.
A comprehensive ThreatsDay report details a wide array of cyber threats, including numerous Android vulnerabilities, sophisticated AI-powered intrusions, and a massive network of fake e-commerce shops.
Threat actors are leveraging generative AI to launch sophisticated financial fraud campaigns, impersonating executives and fabricating invoices to trick organizations into sending illicit payments.
Key findings • Nine Rclone vulnerabilities disclosed on September 10, 2026, ranging from Low to Critical severity. • Critical vulnerabilities (CVE-2026-88018, CVE-2026-88044) impact serve S3,…
Key findings • Three High (8.8) and one Medium (6.5) severity CVEs disclosed for Craft CMS between Sep 8-10, 2026. • Authenticated users can achieve RCE via element-index or OS command execut…
Google has introduced a new Android feature enabling direct, secure transfer of passkeys and passwords between password managers, eliminating insecure file exports.
Cybercriminals are increasingly impersonating popular AI platforms like ChatGPT and Copilot to conduct phishing, malvertising, and malware distribution campaigns.
Three high-severity flaws in NextGen Connect could expose administrator credentials, leading to unauthorized access to sensitive hospital systems and patient data.
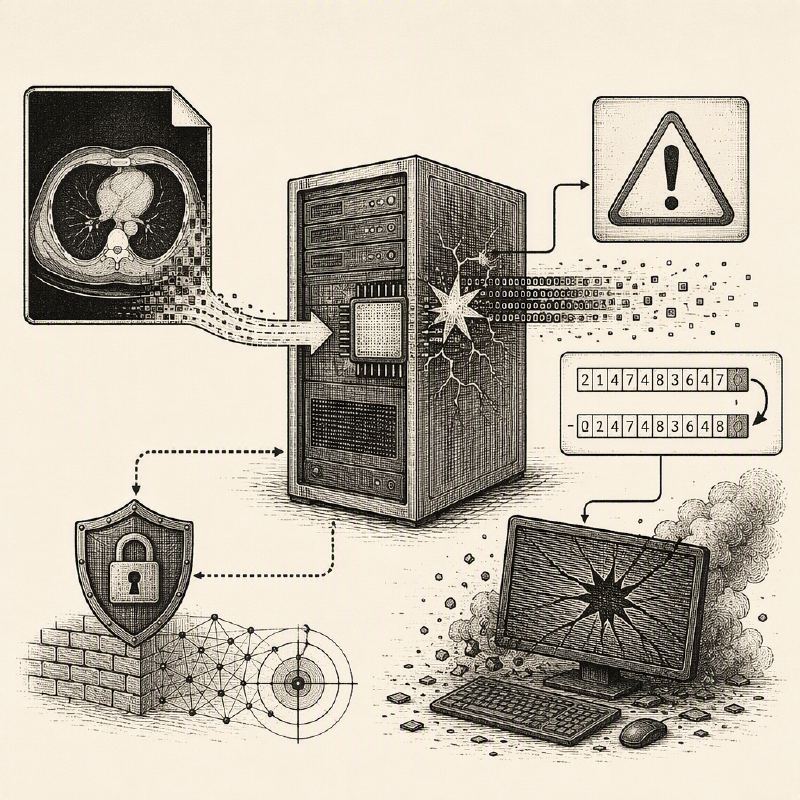
CISA has issued an advisory for Orthanc DICOM Server versions prior to 1.13.0, detailing CVE-2026-87020, an integer overflow vulnerability that can lead to a denial-of-service condition.
CISA has issued an advisory detailing four critical vulnerabilities in AVEVA Pipeline Integrity Monitor, potentially allowing attackers to disclose sensitive information, brute-force passwords, or execute arbitrary code.
Key findings • High severity CVE-2026-88924 in gvfs allows local privilege escalation via TOCTOU race condition. • CVE-2026-74859 in gnome-tweaks permits arbitrary file writes through crafted…
Key findings • 18 vulnerabilities disclosed for Open WebUI between September 9-10, 2026, patched in version 0.11.1. • High-severity flaws include SQL injection (CVE-2026-87016), XSS risks (CV…
Researchers have developed PuzzleMask, a method to hide malicious instructions within benign text, tricking AI gatekeepers and enabling attacks on target models.
Key findings • 16 authorization and access control vulnerabilities disclosed for Snipe-IT in a single batch. • High-severity flaws allow unauthorized data access, asset reassignment, and file…
Key findings • Ten vulnerabilities disclosed for Renovate on September 10, 2026, with most rated High severity. • Multiple command injection flaws found in Maven Wrapper, Mix, Gradle Wrapper,…
Dishonest developers are exploiting Google Play's Early Access program to bypass security reviews and distribute deceptive Android applications to unsuspecting users.
A distributed denial-of-service attack on Wildberries, a major Russian e-commerce platform, led to delayed payments for sellers due to implemented security measures.
Cybercriminals are impersonating IT staff to trick employees into revealing Microsoft 365 credentials by calling their personal phones.
The MantaxOtax Android malware has emerged as a sophisticated dual-threat, combining file encryption for ransom with extensive data exfiltration capabilities, targeting Indonesian users.
Tenable has unveiled its 'agentic harness,' a control layer designed to safely integrate AI agents into security operations by treating them as untrusted insiders.