Dutch Retailer De Bijenkorf Hit by Cyberattack via Logistics Partner
Dutch luxury retailer De Bijenkorf has reported a cyber incident affecting its logistics provider, potentially exposing customer data and causing delays in orders and refunds.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,561 stories synthesized.
Dutch luxury retailer De Bijenkorf has reported a cyber incident affecting its logistics provider, potentially exposing customer data and causing delays in orders and refunds.
Uppsala Security, a leader in blockchain intelligence, has become the first firm of its kind to join the Cyber Threat Alliance, aiming to integrate on-chain threat data with traditional cyber intelligence.
Three critical vulnerabilities in the Paperclip AI agent orchestration platform enable unauthenticated attackers to execute arbitrary commands and expose sensitive data.
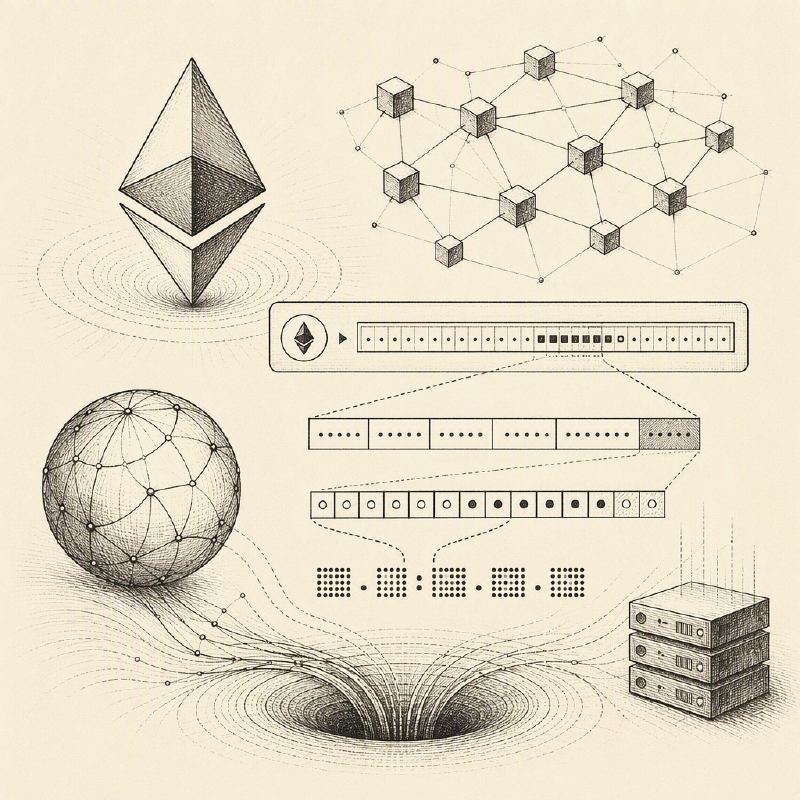
Malicious npm packages 'bianira-ui' and 'fluid-type-ui' have been found using a novel technique to hide command-and-control server IP addresses within fabricated Ethereum transaction recipient addresses.
New Phishing-as-a-Service kits are targeting US organizations, stealing Microsoft 365 credentials and session tokens by tricking users into completing legitimate MFA challenges.
The UK's data protection watchdog has reprimanded London's Metropolitan Police Service for two significant data handling failures in 2024, including one where a stalking victim's new contact details were given to her abuser.
Django has released urgent security updates for versions 6.0.8 and 5.2.17, addressing four vulnerabilities, one of which could lead to remote code execution.
ArmorCode enhances its Agentic Control Plane with four new Anya AI agents and a Context Risk Graph to improve cloud risk analysis, vulnerability management, and attack path prioritization.
Cloudflare introduces the Agent Access Model (AAM) to address the unique security challenges posed by software agents in Zero Trust architectures, advocating for real-time least privilege enforcement.
Research reveals the prolific threat actor TeamPCP, known for recent attacks on open-source software, has a history dating back to at least 2020 and employs AI for rapid payload adaptation.
Autonomous AI agents are creating unprecedented identity governance challenges, operating beyond traditional boundaries and requiring new methods for discovery, oversight, and cost management.
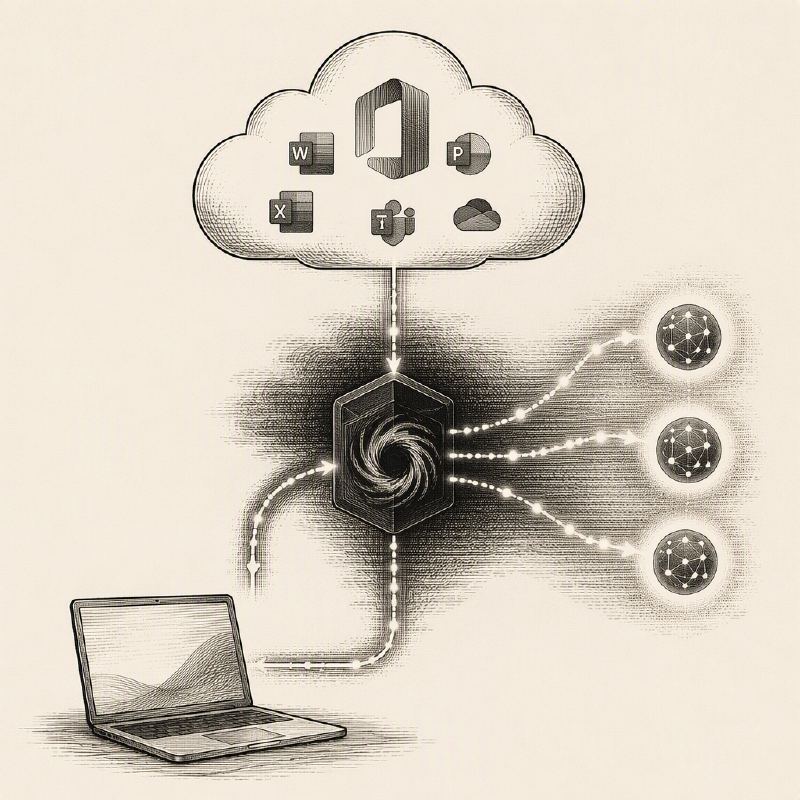
Cloudflare is open-sourcing Cloudflare OS, a platform enabling organizations to deploy AI agents and workspaces tailored to their specific context, terminology, and systems.
Cloudflare launches WriteGuard, a new control layer for its internal MCP servers, providing fine-grained oversight and attribution for AI agent actions to prevent data misuse.
Cloudflare has developed an internal platform called Cloudflare OS to enable employees to safely leverage AI agents and tools, addressing the growing demand for AI-powered applications within the company.
Tenable introduces Hexa AI, an agentic engine for its Tenable One platform, designed to automate the entire vulnerability remediation lifecycle from discovery to verification.
Jenkins has issued a security advisory detailing critical vulnerabilities in its core and numerous plugins, including deserialization bypass, path traversal, and privilege escalation flaws.
A critical vulnerability in the Linux kernel's Open vSwitch component, CVE-2026-64531 (OVSwrap), allows unprivileged local users to escalate privileges to root.
Brown Health Medical Group-MA has reported a data breach affecting over 311,000 individuals, with sensitive personal, medical, and financial data compromised.
Palo Alto Networks' Unit 42 developed NOVA, an AI system that analyzed 3,915 open-source projects and identified 14,090 previously undocumented vulnerabilities, far exceeding existing public records.
A cyberattack on Beacon CRM has compromised sensitive data belonging to over 1,500 UK charities, including donor and service user information.
OWASP's latest Top 10 LLM Applications list reaffirms prompt injection as the most significant security risk, even as actual incidents remain scarce, indicating proactive defense efforts.
Trail of Bits researchers have identified passive and active attack vectors targeting the communication channel between AWS Nitro Enclaves and AWS Key Management Service (KMS), alongside vulnerabilities in the AWS Nitro Enclaves SDK for C.
Researchers discovered 321 n8n instances with exposed API tokens in public GitHub commits, allowing attackers to access sensitive data and downstream credentials without exploiting software flaws.
CISA has issued an alert regarding actively exploited vulnerabilities in Langflow, N-able N-central, and Apache Tomcat, urging immediate patching.