Microsoft Teams Enhances Security by Allowing Admins to Block Meeting Bots
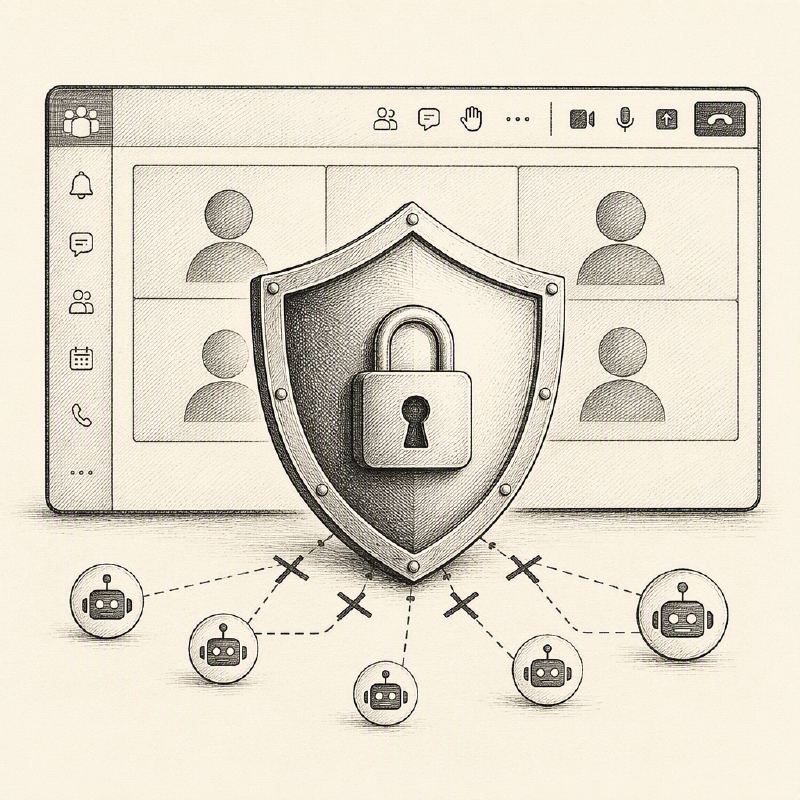
Microsoft Teams administrators can now automatically block identified external meeting bots from joining meetings, bolstering security against unauthorized data capture.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,561 stories synthesized.
Microsoft Teams administrators can now automatically block identified external meeting bots from joining meetings, bolstering security against unauthorized data capture.
Cybercriminals are capitalizing on the immense hype surrounding Grand Theft Auto VI by creating fake demo websites that lure unsuspecting users into downloading the Vidar infostealer.
The Trusted Computing Group (TCG) has issued new guidance to help businesses validate claims of quantum-resistant hardware, focusing on Trusted Platform Modules (TPMs).
Malicious websites impersonating Microsoft are tricking users into uninstalling their legitimate antivirus software by claiming it's unsupported, paving the way for further scams.
ManageWP's integration with Patchstack's vulnerability protection has successfully blocked over 11.9 million threats in a six-month period, significantly enhancing security for agencies managing multiple WordPress sites.
This week's cybersecurity landscape is marked by AI-driven attacks on industrial control systems, a significant leak of Stripe API keys, and a resurgence of interest in older vulnerabilities, alongside the weaponization of trusted tools.
Check Point Research's latest bulletin highlights a range of cyber incidents, including attacks on ports, data breaches, and vulnerabilities in AI tools and network devices.
Attackers are manipulating Google and Bing search results to direct users to fake banking login pages using a technique called Chameleon SEO Poisoning.
An anonymous AI model named Ox Alpha has emerged, offering an unprecedented 100 trillion free tokens daily for coding and agentic tasks, but its undisclosed developer and prompt retention policy pose significant operational security risks.
ReliaQuest has successfully defended against a sophisticated vishing attack where threat actors impersonated its own security team to steal employee credentials and MFA access.
A recent investigation found 768 corporate AWS keys publicly exposed and still active, providing full administrator access and posing significant security risks.
The Kimsuky threat group is employing an AI-assisted Chrome extension to steal sensitive Gmail data, including messages and attachments, as part of a sophisticated espionage campaign.
A critical vulnerability (CVE-2026-19598) in the Everest Forms WordPress plugin, affecting versions prior to 3.0.9.5, enables unauthenticated attackers to achieve complete site takeover through remote code execution and arbitrary file upload.
A sophisticated malware campaign known as Doubloon Dredger is exploiting Notion's integration features and malicious PDFs to harvest user authentication tokens for Microsoft accounts.
Uber has been fined 825 million euros ($964 million) by Dutch regulators for violating GDPR through its automated suspension of driver accounts without human review.
Cybersecurity researchers have identified two new malware families, WordlistLoader and SynkLoader, which are being used to deliver sophisticated payloads like Amatera Stealer and phish for Windows credentials, likely paving the way for ransomware operations.
A new SynkLoader malware campaign uses Microsoft Teams phishing to deliver a toolkit that steals Windows passwords, posing a significant threat to corporate networks.
Developer Matt Callaghan claims AliExpress uses obfuscated JavaScript to perform audio fingerprinting via the WebAudio API, impacting Bluetooth connections and creating comprehensive device fingerprints.
A new malware campaign is compromising Android-based automotive infotainment systems, repurposing them to form a proxy botnet for malicious traffic routing.
Spring Framework has patched a significant number of vulnerabilities this year, with over 200 addressed compared to previous years, indicating a heightened focus on security.
A critical vulnerability in Keycloak, an open-source identity and access management server, allows unauthenticated remote attackers to reset any user's password and take over their account.
Malwarebytes Labs is tracking PavinLoader, a sophisticated .NET loader used in multiple malicious campaigns, including fake software downloads and ClickFix attacks, often delivering information-stealing malware.
Microsoft is investigating an issue where its August 2026 Windows 11 updates are causing games to crash or PCs to restart, specifically on systems utilizing RGB lighting hardware.
A Venezuelan national has received an 8-year federal prison sentence for his role in a sophisticated ATM jackpotting operation that defrauded financial institutions of millions of dollars.