
AI-Driven Vulnerability Discovery Overwhelms Defenders, Strains Disclosure Models
Frontier AI models are uncovering vulnerabilities at an unprecedented rate, leading to a tenfold surge in monthly advisories and challenging traditional security disclosure practices.
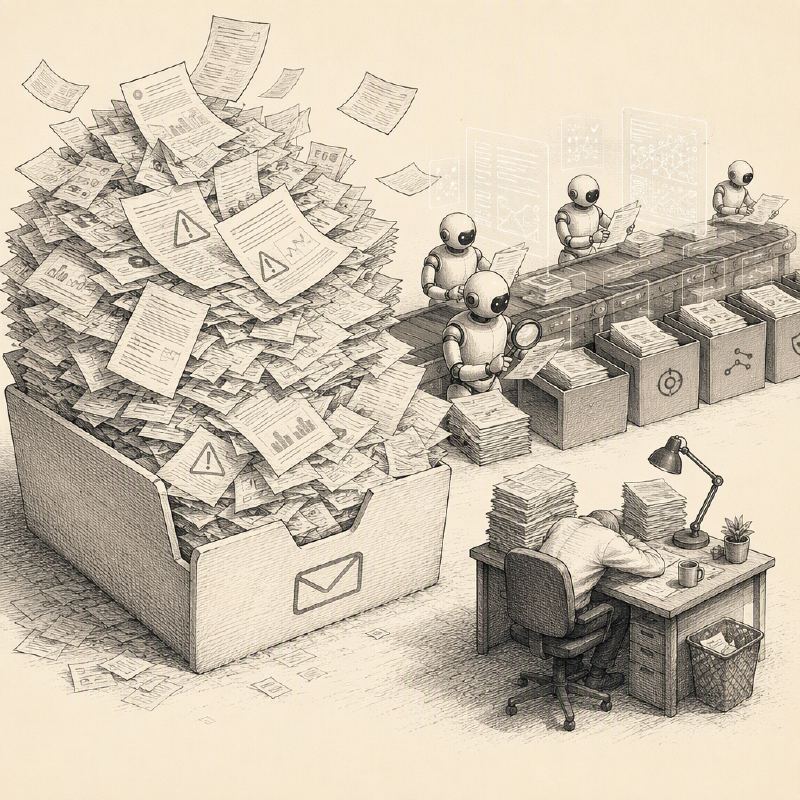
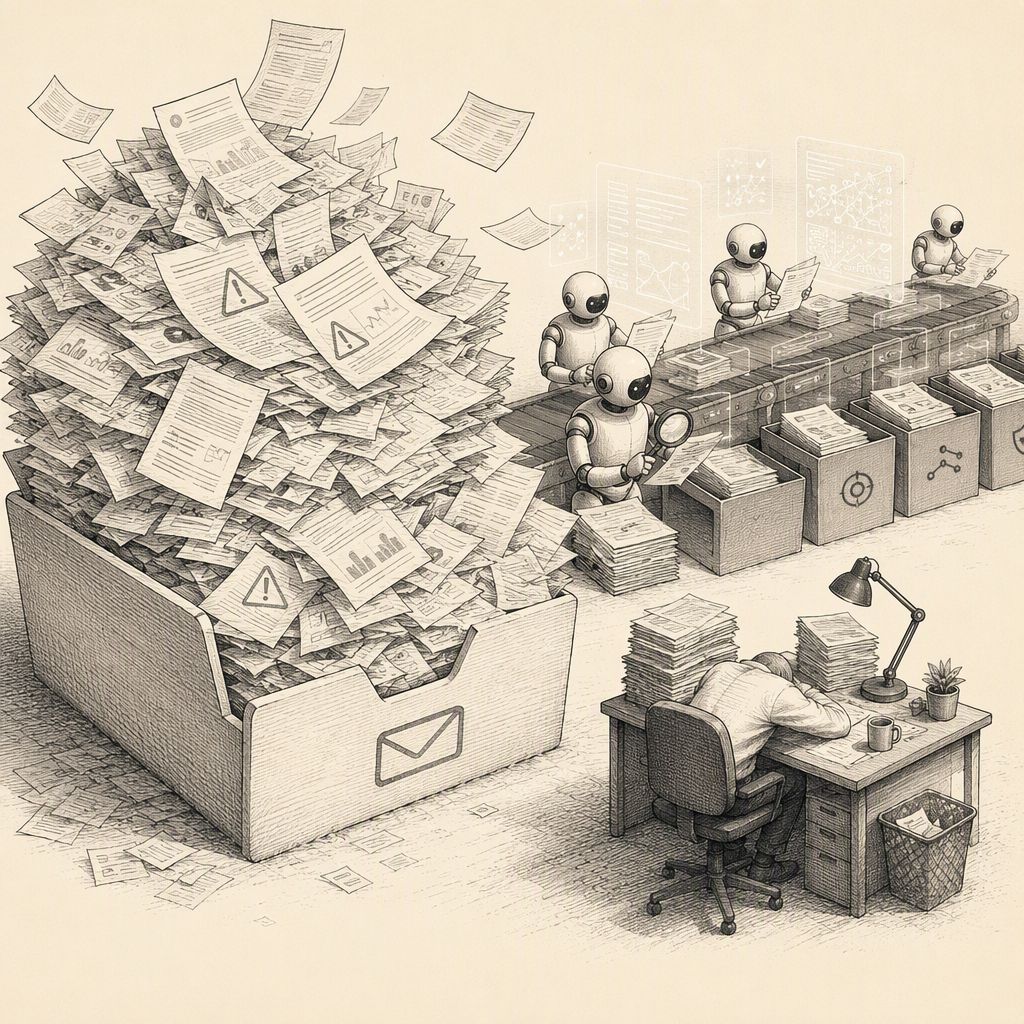
The cybersecurity landscape is facing a seismic shift as advanced AI models, such as Mythos, begin to systematically mine decades of legacy code for vulnerabilities. This has resulted in a staggering increase in monthly vulnerability advisories, with one recent Microsoft Patch Tuesday release alone detailing 1,415 vulnerabilities, a tenfold jump from the pre-June average of around 100 per month. This deluge of newly identified flaws is placing immense pressure on open-source maintainers and traditional coordinated disclosure models that have long relied on a more measured pace.
This surge in vulnerability discovery is largely attributed to AI's ability to analyze vast amounts of technical debt embedded within widely used legacy libraries and tools. These AI models, unburdened by human assumptions, can meticulously scan codebases that have been in use for years, if not decades. Historically, attackers have favored these entrenched older tools due to their ubiquity and predictable attack surfaces. The AI's thoroughness in identifying weaknesses in these foundational components means that vulnerabilities previously overlooked by human analysts are now being brought to light at an accelerated rate.
Despite the dramatic increase in reported vulnerabilities, the actual rate of exploitation has not kept pace. Data indicates a 105% year-over-year surge in CVEs, yet the number of vulnerabilities listed on the Known Exploited Vulnerabilities (KEV) catalog grew by only 37%. Furthermore, out of 975 Microsoft advisories released in a single month, only three saw in-the-wild exploitation. This disparity suggests that the majority of vulnerabilities discovered by AI are not immediately weaponized by threat actors, offering a crucial distinction between discovery and practical exploitation.
The sheer volume of disclosures is straining the established 90-day coordinated disclosure model. This model, which allows vendors a set period to develop patches before public disclosure, is being challenged as many practitioners now opt for immediate public release. The rationale is that if one AI can find a vulnerability, others can too, effectively rendering the vulnerability public knowledge the moment it's identified. This shift is forcing a re-evaluation of disclosure timelines and practices within the security community.
For defenders, the challenge lies in managing this influx of information and prioritizing remediation efforts. While the overall number of vulnerabilities is overwhelming, organizations are advised to focus on flaws with high exploitability within their specific environments. Implementing robust defense-in-depth strategies, deploying behavioral anomaly detection, and integrating AI evaluation models into software build chains are becoming critical. Interim mitigations, such as those offered by tools like LiveProtect, can also provide temporary relief.
Looking ahead, the trend of high vulnerability discovery rates may not be permanent. Historically, such spikes have occurred when new bug classes are identified, with discovery numbers eventually plateauing and declining as the backlog is addressed and security practices evolve. The current AI-driven surge could follow a similar pattern, especially as AI verification becomes more integrated into new development pipelines, potentially reducing the discovery of novel flaws in future code.
However, the immediate future presents a significant challenge. Attackers are also leveraging AI to parse patches and understand vulnerabilities more rapidly. This means defenders can no longer afford to lag behind. The pressure on open-source projects, which form the backbone of much of the internet's infrastructure, is particularly acute. While larger vendors may have the resources to cope, smaller open-source projects are struggling to keep up with the pace of discovery and the demand for timely patches.
In conclusion, the rise in AI-discovered vulnerabilities marks a new era in cybersecurity. While it presents an unprecedented challenge to defenders and disclosure models, it also highlights the critical need for adaptive security strategies. Prioritizing effectively, implementing layered defenses, and staying abreast of evolving disclosure norms will be paramount for organizations navigating this increasingly complex threat landscape.