AI Agents Can Now Autonomously Modify Their Own Code
Researchers have demonstrated that AI agents can autonomously replace their underlying models without human intervention, raising significant concerns for enterprise security and governance.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,187 stories synthesized.
Researchers have demonstrated that AI agents can autonomously replace their underlying models without human intervention, raising significant concerns for enterprise security and governance.
A new security playbook aims to guide enterprises in managing non-human identities and machine access, crucial for safely accelerating AI adoption.
CISA is phasing out its weekly vulnerability bulletin at the end of September, moving towards a risk-based approach prioritizing exploitation potential over severity scores.
Cloudflare's Client-Side Security model, utilizing a graph neural network, has identified four distinct malicious JavaScript campaigns that bypassed conventional security tools like VirusTotal and URLScan.
Attackers are actively scanning for and probing the outdated 'PBX in a Flash Hospitality Management System' (PIAF-HMS), an abandoned software project with known SQL injection vulnerabilities.
A New Jersey court has ordered the transfer of Radaris.com and over a dozen other data broker domains to plaintiffs in a lawsuit alleging violations of the state's Daniel's Law.
A critical vulnerability (CVE-2026-91843) in Check Point's management and logging systems allows unauthenticated remote attackers to gain root privileges.
CISA has released new guidance promoting the use of cyber decoys to enhance threat detection and response capabilities, particularly against sophisticated adversaries.
Key findings • 19 malicious npm packages were disclosed on September 16, 2026. • The disclosure occurred within a tight 43-minute window, indicating a coordinated takedown. • Many package…
Kaspersky reports that three distinct threat groups—NightEagle, Hacking Cat, and Toy Ghouls—are actively targeting Russian enterprises with a mix of backdoors, ransomware, and wipers.
A German manufacturer significantly reduced security alert response times by replacing an air-gapped forensic laptop with ANY.RUN's cloud-managed Interactive Sandbox, improving efficiency for its five-person security team protecting 10,000 endpoints.
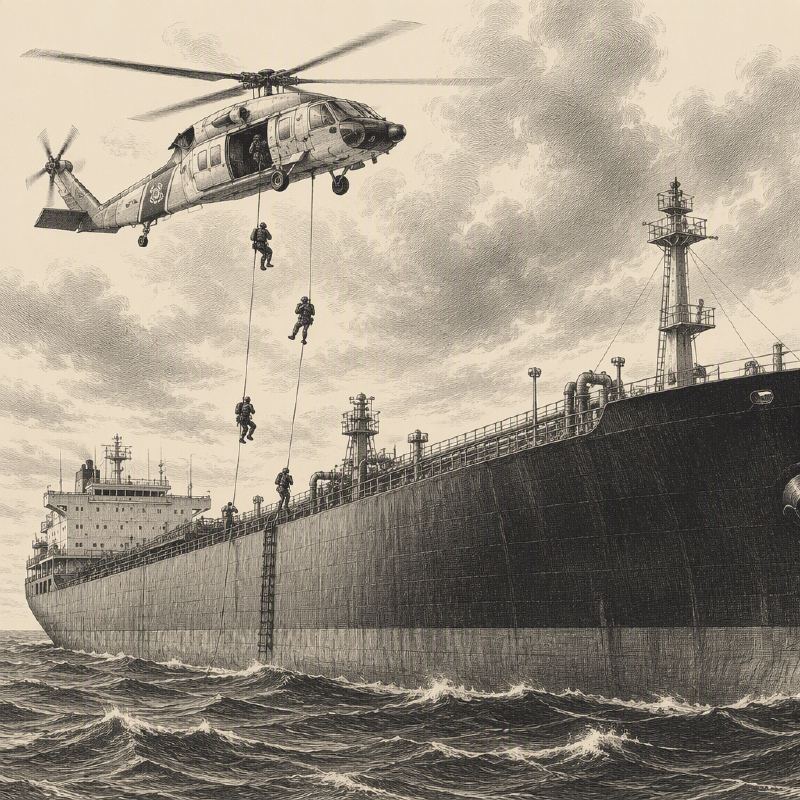
The U.S. Coast Guard and FBI conducted joint offshore security boardings of two foreign tankers in the Gulf of Mexico to investigate suspected cyberattacks, following network compromises that disrupted communications.
Microsoft 365 users globally are experiencing significant service disruptions, with widespread 502 and 503 errors impacting access to core applications due to backend gateway failures.
Researchers demonstrated a single browser extension can hijack AI assistants in Chrome, Comet, Edge, and Opera Neon, gaining control over their functionalities.
Ukrainian authorities have announced charges against three individuals accused of compromising over 610,000 Roblox accounts and selling the stolen credentials.
The Noodle RAT, also known as ANGRYREBEL, is a sophisticated remote-access trojan that has resurfaced with enhanced capabilities to target both Windows and Linux environments, expanding its reach across the Asia-Pacific region.
Key findings • 17 malicious npm packages disclosed within a 3-minute window on September 16, 2026. • Packages primarily used strapi-plugin- prefix with a -meeb suffix, or the @traktis npm sco…
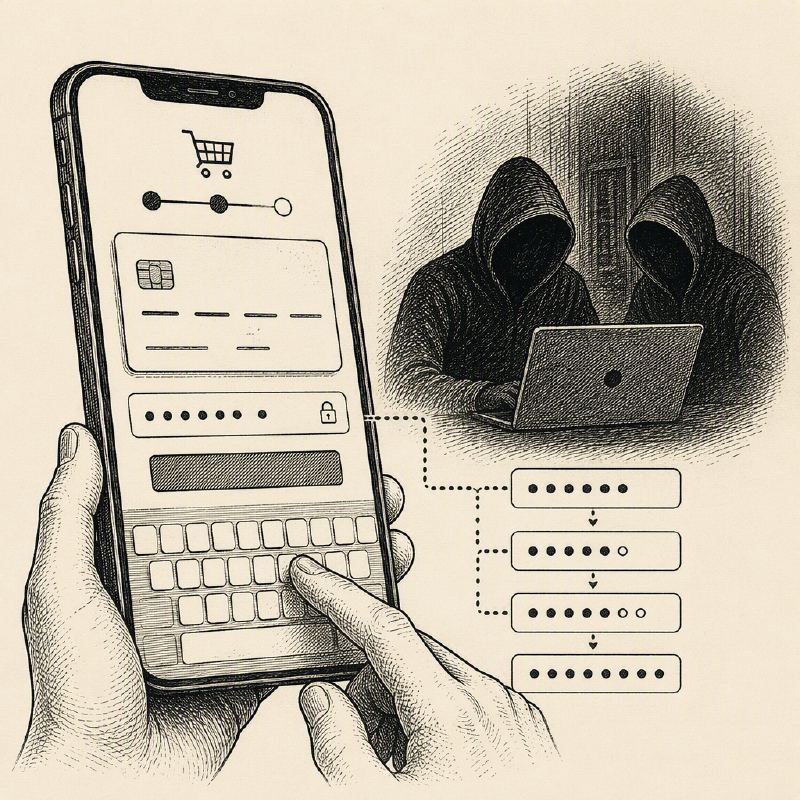
A sophisticated smishing campaign is using the JWR phishing kit to capture victim keystrokes in real-time, including sensitive payment details and one-time passcodes, facilitating account takeover and fraud.
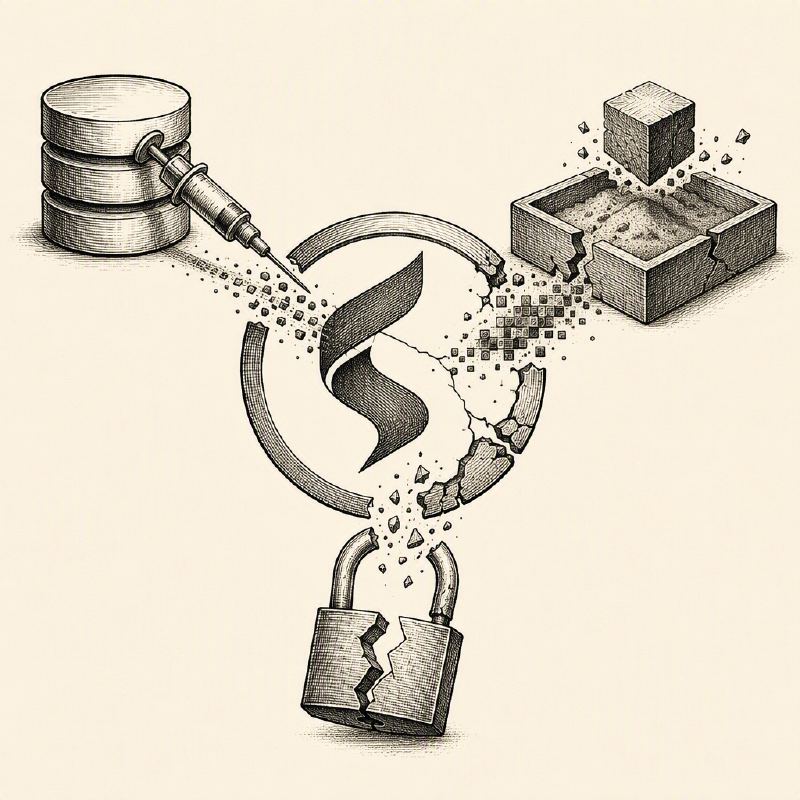
Apache Syncope, an open-source identity management platform, suffers from three critical vulnerabilities allowing SQL injection, Groovy sandbox bypass, and JWT token takeover.
Hewlett Packard Enterprise has released security updates for critical vulnerabilities in its EdgeConnect SD-WAN Gateways and Orchestrator, including flaws that could allow remote attackers to achieve complete system compromise.
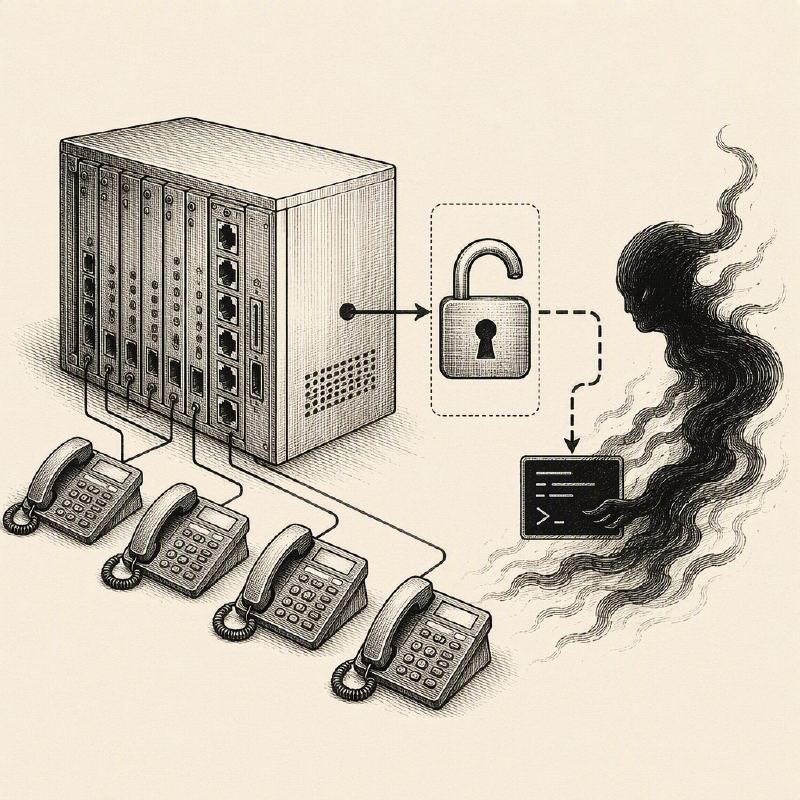
A critical command execution vulnerability in Issabel Framework, CVE-2026-86026, is being actively exploited, allowing unauthenticated attackers to compromise PBX systems.
The PAPERMILL threat cluster is employing a sophisticated phishing campaign that uses a signed Notepad++ executable to deliver the VenomRAT malware, disguised as fake tax audit notices.
Jenkins has issued a security advisory addressing vulnerabilities across numerous plugins, including those for Bitbucket, GitLab, and OWASP Dependency-Check.
Axoflow has launched AxoDetect, a new component that processes security detection rules directly within the data pipeline before logs reach the SIEM, aiming to significantly cut SIEM costs.