advisory1 source
Fortinet FortiManager Vulnerability Allows Workflow Approval Bypass
A critical access control flaw in Fortinet's FortiManager allows administrators to bypass workflow session approvals through crafted HTTP requests.
Sep 8, 2026

Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 6,158 stories synthesized.
A critical access control flaw in Fortinet's FortiManager allows administrators to bypass workflow session approvals through crafted HTTP requests.
Fortinet has disclosed a broken access control vulnerability in its FortiSOAR platform that could allow authenticated attackers with no permissions to access sensitive data and inject messages.
Fortinet has issued an advisory for an open redirect vulnerability in its FortiSIEM product, allowing authenticated attackers to redirect users to arbitrary websites.
A critical command injection vulnerability in FortiSandbox allows privileged attackers to execute arbitrary code through malicious HTTP requests.
Fortinet has issued a security advisory for an improper authentication vulnerability in the FortiPAM Server's Chrome Extension, potentially allowing attackers to proxy user traffic.
A critical vulnerability in Fortinet's FortiAnalyzer SNMP daemon could allow authenticated attackers to cause a denial of service by sending specific SNMP requests.
A critical improper access control vulnerability in Fortinet's FortiSandbox products allows unauthenticated attackers to access sensitive information by manipulating NAT rules.
Ransomware groups are professionalizing their negotiation tactics, treating them as a structured business process to maximize profits and efficiency.
Key findings • 19 vulnerabilities disclosed in Code Projects applications between September 3-8, 2026. • Batch includes SQL injection, information disclosure, and XSS flaws across multiple pr…
A critical integer underflow vulnerability in Microsoft Windows' IKEv2 component, tracked as CVE-2026-50696, permits unauthenticated remote code execution on systems with specific IPsec configurations.
A local privilege escalation vulnerability in Microsoft Windows, tracked as CVE-2026-62712, allows attackers with initial low-privileged access to gain elevated system privileges.
A critical vulnerability in the Koha library management system allows authenticated remote attackers to execute arbitrary code, posing a significant risk to institutions relying on the software.
A local privilege escalation vulnerability in Microsoft Windows' MIDI service, ZDI-26-617 (CVE-2026-66804), allows attackers with low-privileged code execution to gain higher privileges.
Key findings • 17 SQL injection vulnerabilities disclosed for Itsourcecode products between September 6-8, 2026. • All vulnerabilities have publicly available exploits, increasing immediate r…
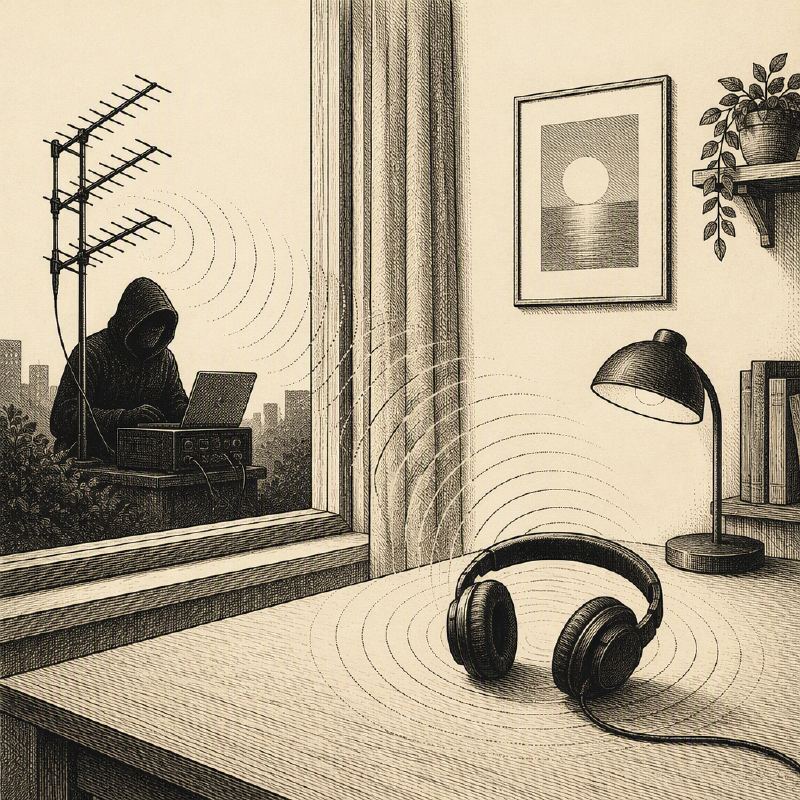
Researchers have developed a novel electromagnetic attack, dubbed InjectEave, capable of eavesdropping on audio played through wired and wireless headphones from up to 30 meters away, even through walls.
Key findings • Ten vulnerabilities disclosed for Ash Project components between 2026-09-07 and 2026-09-08. • Two high-severity flaws include resource exhaustion in the OAuth2 server and arbit…
Key findings • CVE-2026-75650, an Adobe vulnerability, is now on CISA's KEV catalog. • The flaw is confirmed to be actively exploited in real-world attacks. • All organizations should pri…
Mandiant's latest AI Threat Tracker reveals threat actors are rapidly evolving their use of AI, moving from basic prompting to autonomous agentic workflows and sophisticated supply chain attacks.

Key findings • Two Microsoft vulnerabilities, CVE-2026-81963 and CVE-2026-85880, are now in CISA's KEV catalog. • Both flaws are confirmed to be under active exploitation in real-world attack…
Cybercriminals are increasingly targeting loyalty points programs, turning accumulated rewards into cash for flights, hotel stays, and other illicit gains.
A new post-exploitation toolkit named PEEP leverages Chrome and Edge browser extensions to establish a backdoor for executing commands on compromised hosts, bypassing standard security checks.
Key findings • 22 vulnerabilities disclosed simultaneously for JetBrains YouTrack on September 7, 2026. • Vulnerabilities range from Medium to Critical severity, impacting multiple versions. …
Key findings • Dell Secure Connect Gateway 5.0 impacted by 25 vulnerabilities disclosed on September 7, 2026. • High-severity flaws include OS command injection, missing authentication, and i…
A sophisticated threat cluster is targeting executives with Microsoft 365 data theft and extortion, using vishing, AitM token theft, and residential proxies.