Password-Spraying Campaign Targets Over 150 Organizations' AWS Root Accounts
A password-spraying campaign between July and August 2026 targeted AWS root accounts at more than 150 organizations, though no successful compromises were confirmed.
Stories cluster related articles into a single narrative, linked to the underlying CVEs and affected products. 8,239 stories synthesized.
A password-spraying campaign between July and August 2026 targeted AWS root accounts at more than 150 organizations, though no successful compromises were confirmed.
Key findings • 25 vulnerabilities disclosed across Ash Project components, ranging from Low to High severity. • Critical code injection (CVE-2026-77956) in ash_ai allows arbitrary code execut…
CrowdSec's latest release, version 1.8.0, introduces integrated bot detection capabilities for its Web Application Firewall and addresses two critical Denial-of-Service vulnerabilities in its log intake components.
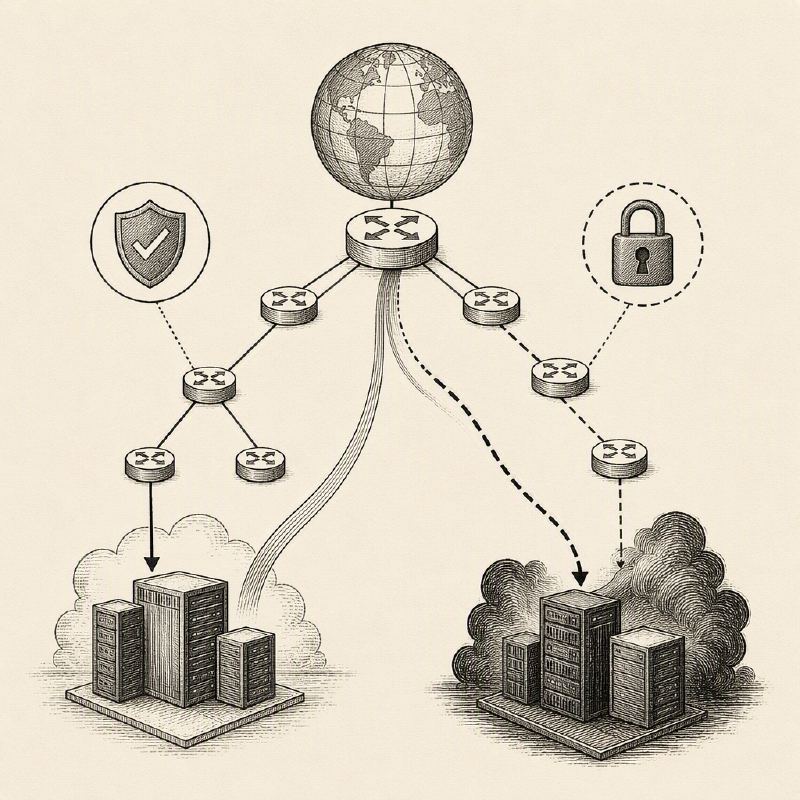
Attackers hijacked BGP routes for Softaculous, diverting traffic to deliver a malicious Virtualizor update with a valid TLS certificate, potentially enabling root-level code execution on hypervisor servers.
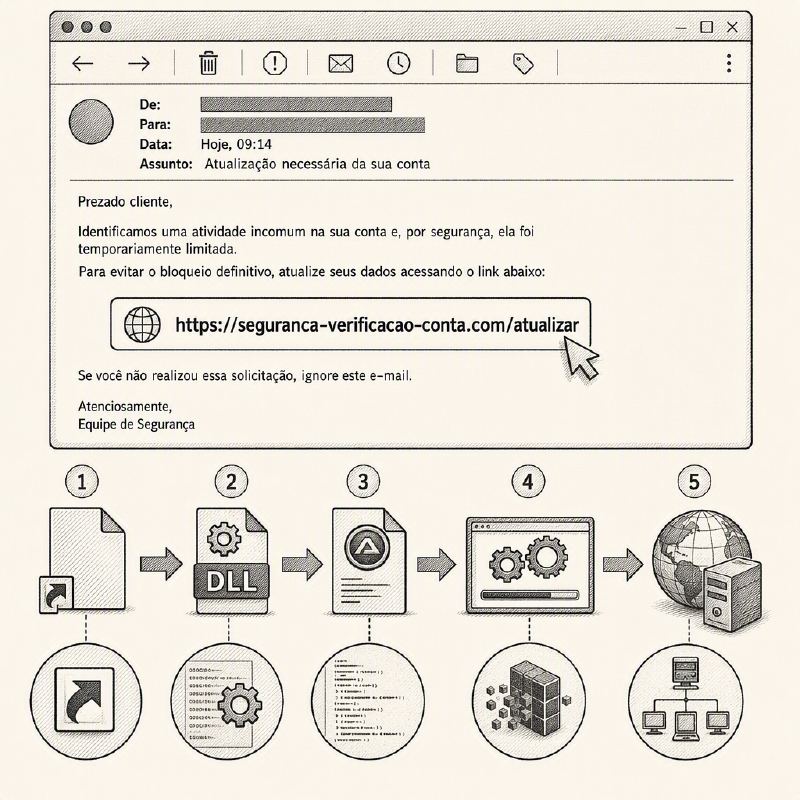
A new Guildma (Astaroth) malware campaign is using geofenced emails in Brazilian Portuguese to infect targeted Windows users, employing a multi-stage infection chain that includes shortcut files and AutoIt scripts.
Mandiant has identified BREEZE COMET, a financially motivated threat actor targeting Brazil's financial sector with custom malware and AI-assisted development to manipulate payment systems for fraudulent transfers.
Key findings • 40 malicious npm packages disclosed within a 2-minute window on August 31, 2026. • Packages share 'allied' and 'alleged' prefixes, often with animal names and suffixes like _z3…
Healthcare giant McKesson disclosed a cyberattack resulting in data theft and temporary service interruptions, with the threat group ShinyHunters claiming responsibility and demanding over $55 million.
Key findings • Five critical vulnerabilities disclosed in Tenda routers between August 30-31, 2026. • Flaws include missing authentication, buffer overflows, and hardcoded credentials. • …
Following U.S. strikes on Iranian rocket launchers, federal warnings highlight increased cyber risk to American critical infrastructure, with Iranian-linked actors historically probing energy and water systems after kinetic escalations.
Key findings • 25 vulnerabilities in Totolink T6 firmware (4.1.5cu.748_B20211015) disclosed on August 31, 2026. • All flaws stem from incorrect access control in the /cgi-bin/cstecgi.cgi endp…
Key findings • Four vulnerabilities disclosed in Zephyr RTOS on August 31, 2026, affecting networking and subsystems. • CVE-2026-14697: Potential improper handling of network traffic due to p…
Attackers are repurposing internet-scanned honeypots and other exposed servers as rogue Large Language Model (LLM) endpoints, tricking tool-enabled AI agents into connecting and potentially executing malicious commands.
An attacker exploited the Tectonic crypto lending platform by artificially inflating the price of its native token, leading to the theft of at least $6 million.
Texas has initiated 'Project Watershed 250,' a six-month pilot program enlisting over a dozen private sector companies to leverage AI and cybersecurity expertise to protect the state's water systems from escalating threats.
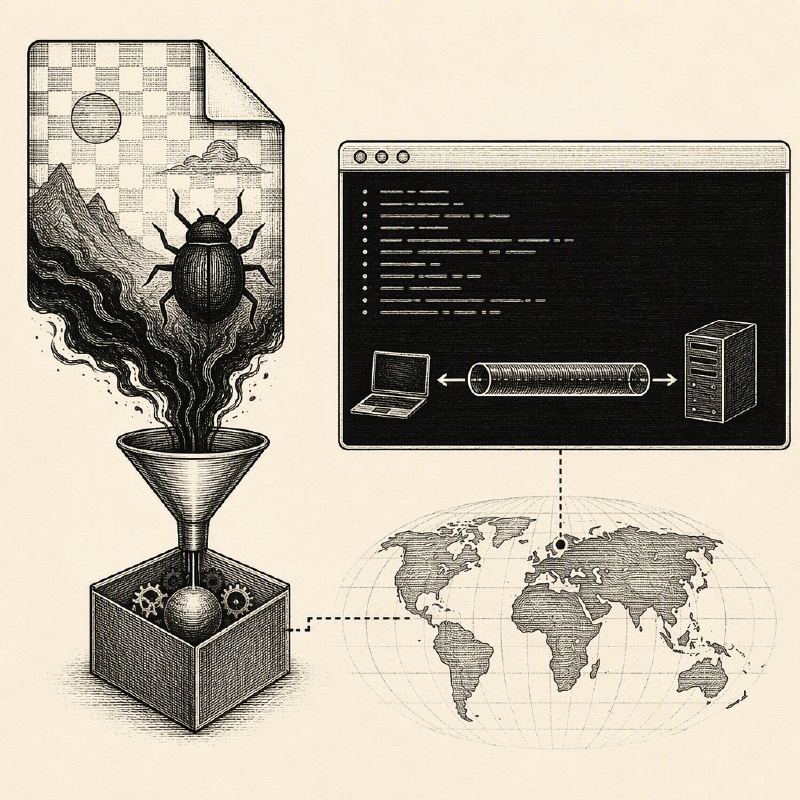
A new attack campaign dubbed 'TerminalFix' uses social engineering and steganography to deliver a custom reverse tunnel, granting attackers network-level access.
Multiple US Department of Defense commissaries are experiencing significant refrigeration outages, sparking concerns of a coordinated cyberattack targeting critical infrastructure.
Key findings • 24 vulnerabilities in TOTOLINK T6 firmware (4.1.5cu.748_B20211015) disclosed on August 31, 2026. • All flaws stem from incorrect access control in the /cgi-bin/cstecgi.cgi endp…
Broadcom's VMware AI Factory aims to simplify enterprise AI agent deployment and governance with automated infrastructure, centralized security controls, and secure sandboxes.
Microsoft is actively investigating a new disruption impacting Exchange Online, identified as EX1464935, affecting mail flow and user access.
Key findings • Six vulnerabilities disclosed on August 31, 2026, affect multiple Code Projects software including Typora. • Vulnerabilities include SQL injection, XSS, and information disclos…
Key findings • Five vulnerabilities disclosed for NASA software including earthdata-search, cFS, and Trick between Aug 30-31, 2026. • High severity flaws include SSRF in earthdata-search and …
Key findings • Three vulnerabilities in Ebyte NA111-M disclosed on August 31, 2026, with severity ranging from Medium to Critical. • CVE-2026-76133 (Critical) involves a deprecated hashing al…
Critical vulnerabilities in D-Link's DIR-X1860Z router enable unauthenticated local attackers to alter administrator passwords and extract Wi-Fi credentials.