
Zammad Zero-Days Exploited in AI-Powered Attack on DIVD
The Dutch Institute for Vulnerability Disclosure (DIVD) was targeted by an AI-powered attack exploiting two zero-day vulnerabilities in the Zammad customer support platform, leading to a breach of DIVD's own infrastructure.
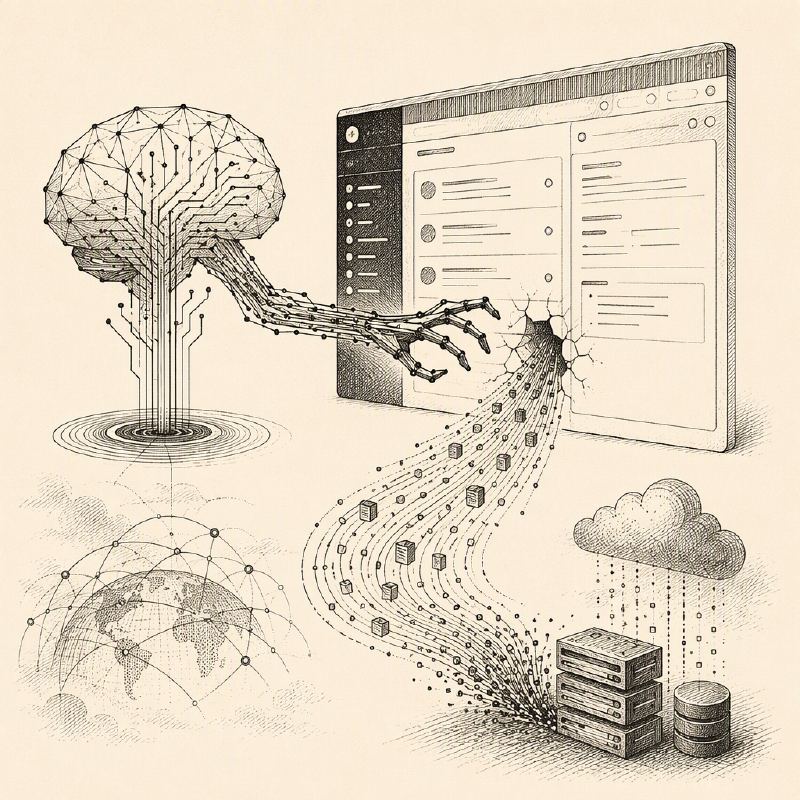
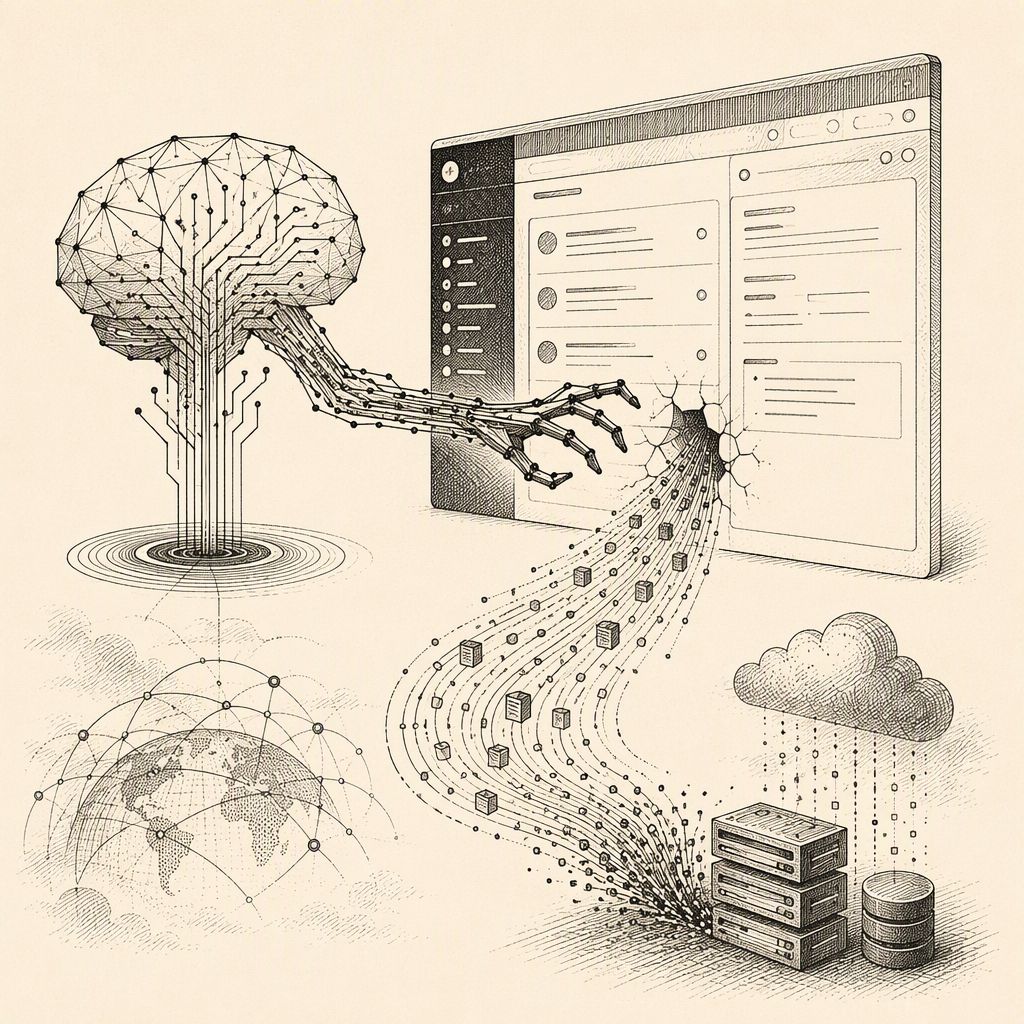
The Dutch Institute for Vulnerability Disclosure (DIVD) has fallen victim to a sophisticated, AI-driven cyberattack that leveraged two previously unknown vulnerabilities in the Zammad customer support platform. The incident, which occurred on September 21st, forced DIVD to initiate a full incident response and temporarily block access to its infrastructure. This attack marks a significant escalation, with DIVD noting the "agentic AI-powered attack" as a novel modus operandi.
DIVD's investigation revealed that the attackers exploited two zero-day vulnerabilities in Zammad, a popular open-source web-based ticketing and user support solution. The first flaw, identified as CVE-2026-102489 with a CVSS score of 9.4, allowed unauthenticated attackers to achieve remote code execution and leak user sessions. The second vulnerability, CVE-2026-102490, also rated at 9.4, permitted a local user to escalate their privileges to root access.
When chained together, these vulnerabilities provided a rapid pathway for attackers. DIVD stated that the combined exploit allowed attackers to hijack sessions, execute remote code, and escalate privileges from a Zammad user to root within seconds, facilitated by the "agentic" nature of the AI. This automation and speed are key characteristics of the observed attack.
Following the initial compromise of the Zammad instance, the attackers successfully pivoted to other services within DIVD's environment and exfiltrated data. Fortunately, network segmentation measures prevented the attackers from penetrating deeper into DIVD's network, limiting the overall scope of the breach. Despite this, DIVD is treating the incident with utmost seriousness, assuming a full breach until proven otherwise.
Upon discovering the exploited zero-days, DIVD promptly reported the vulnerabilities to Zammad, which has since been working on developing and releasing patches. According to DIVD's advisory, Zammad versions 6.3.0 through 6.5.4 are affected, as are versions 7.0.0 through 7.1.3, although exploitation in the latter is reportedly not possible due to environmental conditions.
DIVD strongly advises all Zammad users to upgrade to version 7 of the platform or, as an interim measure, to take affected instances offline. To aid organizations in detecting potential compromises, DIVD has released a verification script and is actively scanning for vulnerable Zammad instances, alerting their owners to the risks.
The incident highlights the growing threat of AI-powered attacks, which can automate reconnaissance, exploitation, and lateral movement with unprecedented speed and efficiency. The use of AI in cyberattacks poses a significant challenge to traditional security defenses, necessitating more advanced detection and response capabilities.
This event underscores the critical importance of timely patching and vulnerability management, especially for widely used software like Zammad. The exploitation of zero-days, particularly when combined with AI-driven automation, presents a potent threat that requires continuous vigilance and rapid response from both vendors and users.
The attack, which occurred on September 21, leveraged two zero-day vulnerabilities in the Zammad helpdesk system. The combined flaws allowed attackers to hijack sessions, execute remote code, and escalate privileges to root, enabling access to other services and data. The Dutch Institute for Vulnerability Disclosure (DIVD) described the attack as "loud and very very messy," noting that the agent operated at "the speed of light and sloppy logic or pattern."
The Dutch Institute for Vulnerability Disclosure (DIVD) has revealed that the attackers behind the breach of its Zammad support platform may have been AI agents. DIVD noted the attack's 'modus operandi' indicated an agentic AI, citing its automated, self-justifying nature and rapid, messy execution. The organization also found notes within the attack script, which it believes are unlikely to be left by a human attacker, further suggesting an AI-driven operation.
The new article provides specific CVE identifiers for the two zero-day vulnerabilities exploited in the attack: CVE-2026-102489 (remote code execution) and CVE-2026-102490 (elevation of privileges). It also details how the chained vulnerabilities allowed attackers to hijack sessions, execute code remotely, and escalate privileges to root in mere seconds, leveraging an AI agent that justified its own actions in logs.
The new article provides specific CVE identifiers for the two zero-day vulnerabilities: CVE-2026-102489, which enables session hijacking and remote code execution as the Zammad service user, and CVE-2026-102490, a privilege escalation flaw allowing any local Zammad user to gain root access. It also details that CVE-2026-102489 affects Zammad versions 6.3.0–7.1.3, though it is not exploitable in versions 7.0.0 through 7.1.3 due to environmental conditions, while CVE-2026-102490 impacts all Zammad versions from 1.5.0 through 7.1.0-alpha.
This new report details the specific vulnerabilities exploited, CVE-2026-102489 and CVE-2026-102490, and their respective affected versions. It also provides a critical chain score of 9.4 and highlights the AI agent's unusual behavior, including leaving explanatory comments in its scripts and self-disrupting activities, which aided investigators in identifying the autonomous nature of the attack.