
Web Servers Mishandle GET Requests with Bodies, Deviating from HTTP Standards
Common web servers like Apache, NGINX, and Python's http.server exhibit non-standard behavior when processing GET requests that include a body, potentially leading to unexpected outcomes.
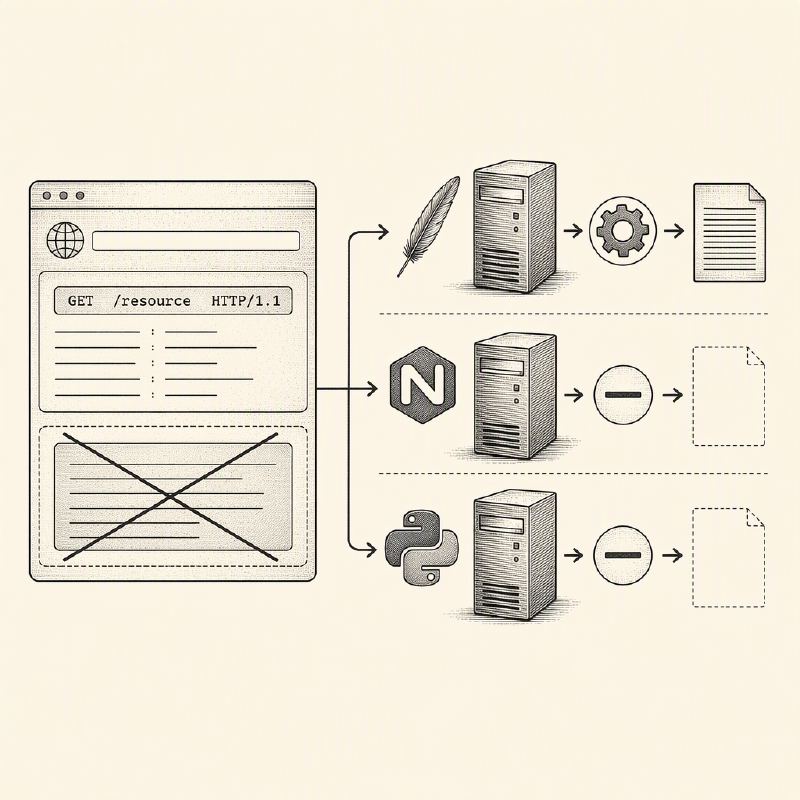
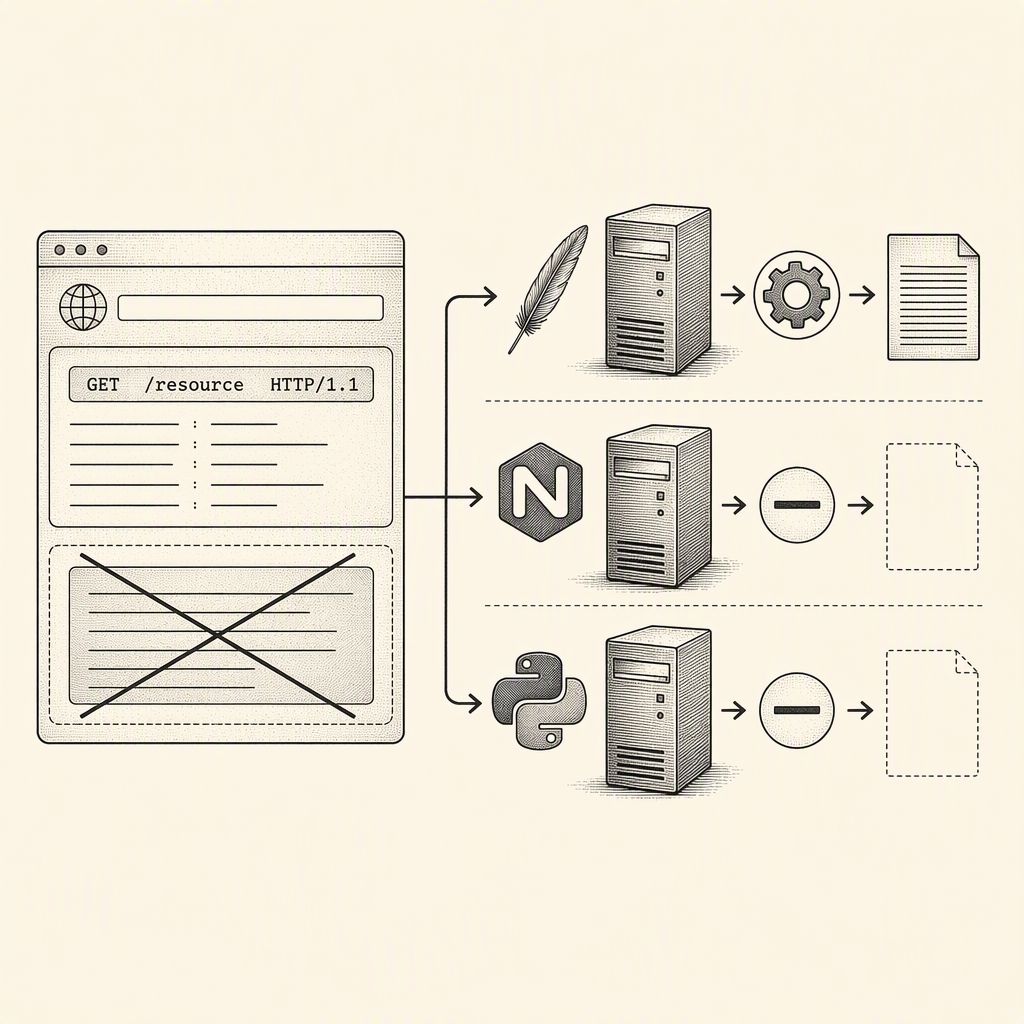
The standard HTTP protocol dictates that GET requests should not contain a message body. However, recent observations have revealed that several widely-used web servers do not strictly adhere to this convention, processing or ignoring these bodies in ways that deviate from expected behavior.
Testing conducted on Apache version 2.4.68 demonstrated a surprising level of compliance with non-standard requests. When presented with a GET request that included a body, Apache successfully processed the data and returned a standard 200 OK status code. This indicates that the server not only accepted the body but also made it available for processing, a behavior that could be exploited or lead to unintended consequences if applications rely on strict adherence to GET request semantics.
In contrast, NGINX and Python's built-in http.server module exhibited a different, yet still non-standard, response. While these servers also returned a 200 OK status without errors, they effectively ignored the provided body. The servers began sending their responses as soon as the headers were received, indicating that the content of the GET request's body was not utilized or even fully read. This behavior, while not directly causing an error, still represents a departure from the intended design of the HTTP GET method.
The implications of this behavior are multifaceted. For developers, it means that relying on the absence of a body in GET requests for security or logic might be flawed. Applications that expect GET requests to be idempotent and free of side effects could encounter issues if a server, like Apache, actually processes the body. Conversely, if an attacker attempts to use a GET request with a body to probe for vulnerabilities or inject data, the varied responses from different servers could complicate exploitation efforts.
This divergence in handling GET requests with bodies highlights a potential area of ambiguity in web server implementations. While the HTTP specification clearly advises against including bodies in GET requests, the practical reality is that servers may interpret and handle them differently. This can lead to inconsistencies across different platforms and potentially create security blind spots.
The SANS Internet Storm Center, which reported these findings, has encouraged further testing across a wider range of web servers and configurations. Understanding how various server software and versions react to non-standard requests is crucial for maintaining robust security postures and ensuring predictable application behavior.
While the immediate impact might seem minor, this exploration into non-standard HTTP request handling serves as a reminder of the complexities inherent in web protocols. As the web evolves, so too do the ways in which servers and applications interpret and respond to requests, underscoring the need for continuous vigilance and testing in the cybersecurity landscape.
This behavior deviates from standard HTTP practices where GET requests are not expected to have bodies. The tests, performed using netcat (nc) against Apache 2.4.68, NGINX, and Python's http.server, revealed that Apache processed the body, while NGINX and Python ignored it but still returned a 200 OK status.