
VirusTotal Enhances Ransomware Detection with Behavior-Based Encryption Verification
VirusTotal's updated ransomware detection now verifies actual document encryption during execution, catching previously undetected threats.
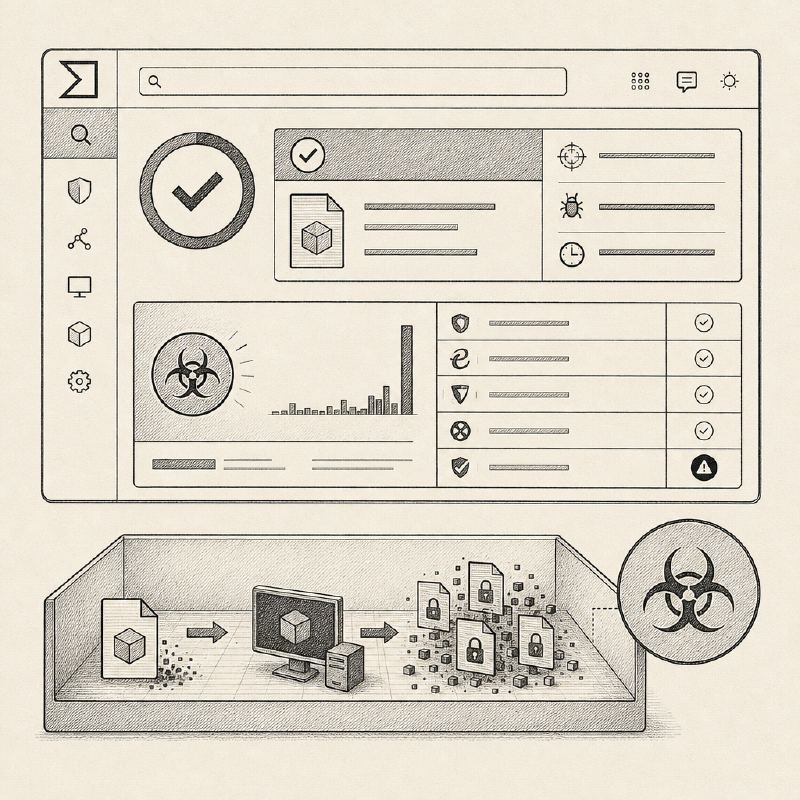
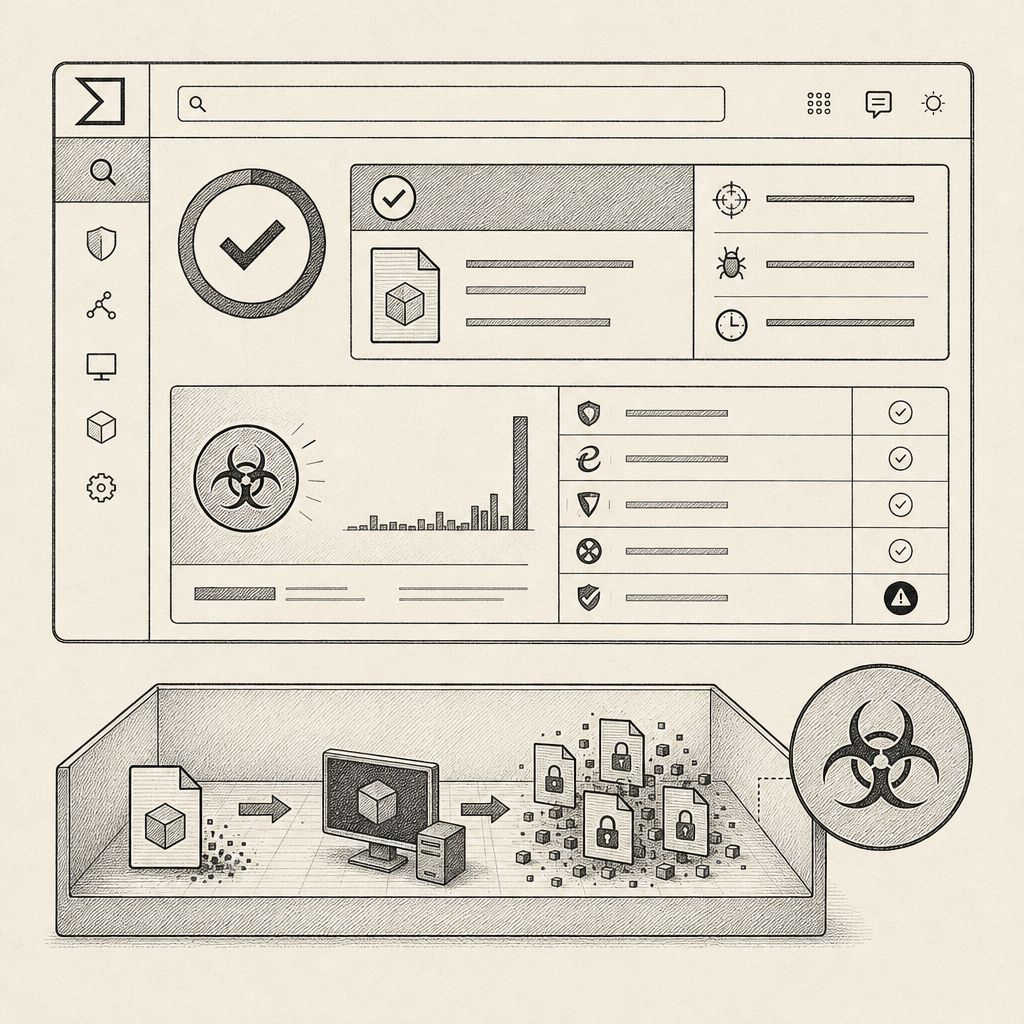
VirusTotal has significantly bolstered its ransomware detection capabilities by implementing a new verification process that confirms whether suspicious files actively encrypt user documents during execution. This behavioral analysis approach aims to identify threats that evade traditional static scanning methods, which often miss sophisticated malware.
The updated system, integrated across VirusTotal and Google Threat Intelligence, now employs behavior checks within sandboxed environments like Zenbox, CAPE Sandbox, and the macOS Mirage environment. These sandboxes meticulously analyze file activity, focusing on whether user documents are demonstrably altered or encrypted. Instead of relying solely on the presence of encryption code or heavy file operations, the system now requires concrete evidence of document damage before tagging a file as ransomware.
This enhancement is particularly crucial for detecting malware that employs diverse encryption techniques, including custom routines or partial encryption. By examining the actual state of files on disk after execution, the sandboxes can identify threats that might otherwise go unnoticed. The system tracks file reads, writes, renames, and deletions, while excluding routine installer activities to maintain accuracy.
A prime example of this new detection capability in action was the identification of a Python ransomware sample, system_update.pyw, linked to the .k404 extortion campaign. This sample initially showed zero detections across 75 antivirus engines. However, the Zenbox sandbox observed it executing, deleting itself, and successfully encrypting desktop documents with the .k404 extension, thereby triggering the new detection tag.
Further analysis revealed that related Windows executables also exhibited ransomware behavior, though with varying levels of initial detection by traditional engines. The system also successfully identified the INC Ransom, which encrypts documents with the .INC extension and drops corresponding ransom notes, a variant previously linked to attacks in the healthcare sector.
VirusTotal reports that since November 17, the new encrypts-files tag has matched 55 files among over 328,000 newly submitted unique files, with manual reviews indicating no benign software among these matches. This update also led to a significant reduction in false positives for the MITRE ATT&CK T1486 (Data Encrypted for Impact) mapping, decreasing its volume by 97.6% by requiring verified document encryption.
Security analysts can now leverage new search tags like tag:encrypts-files and the YARA-X trait vt.BehaviourTrait.ENCRYPTS_FILES for real-time alerts and threat hunting. While this enhancement significantly improves the detection of active encryption, VirusTotal cautions that a missing tag does not definitively prove the absence of ransomware, as some malware may require additional conditions before initiating encryption.
This behavioral analysis upgrade represents a critical step forward in combating evasive ransomware threats, providing a more robust defense against malware that bypasses signature-based detection. By focusing on the actual impact of malicious code on user data, VirusTotal is enhancing its ability to identify and flag sophisticated threats that were previously falling through the cracks.