
Vercel Sandbox Challenge Uncovers Critical Linux Kernel Flaws
A $1 million bug bounty program at Vercel has yielded significant findings, including critical vulnerabilities in the Linux kernel's networking stack.
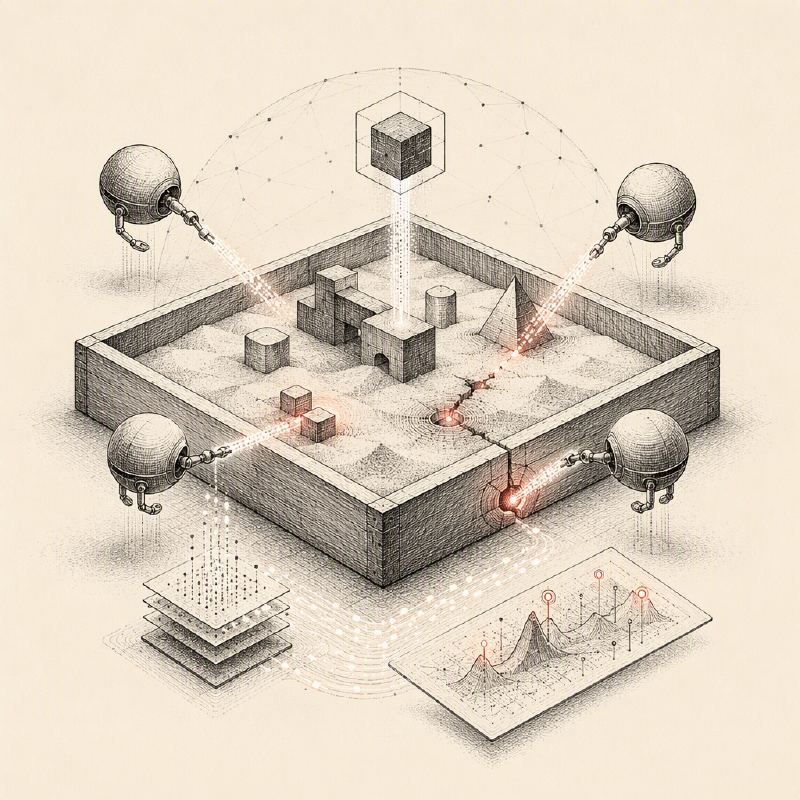
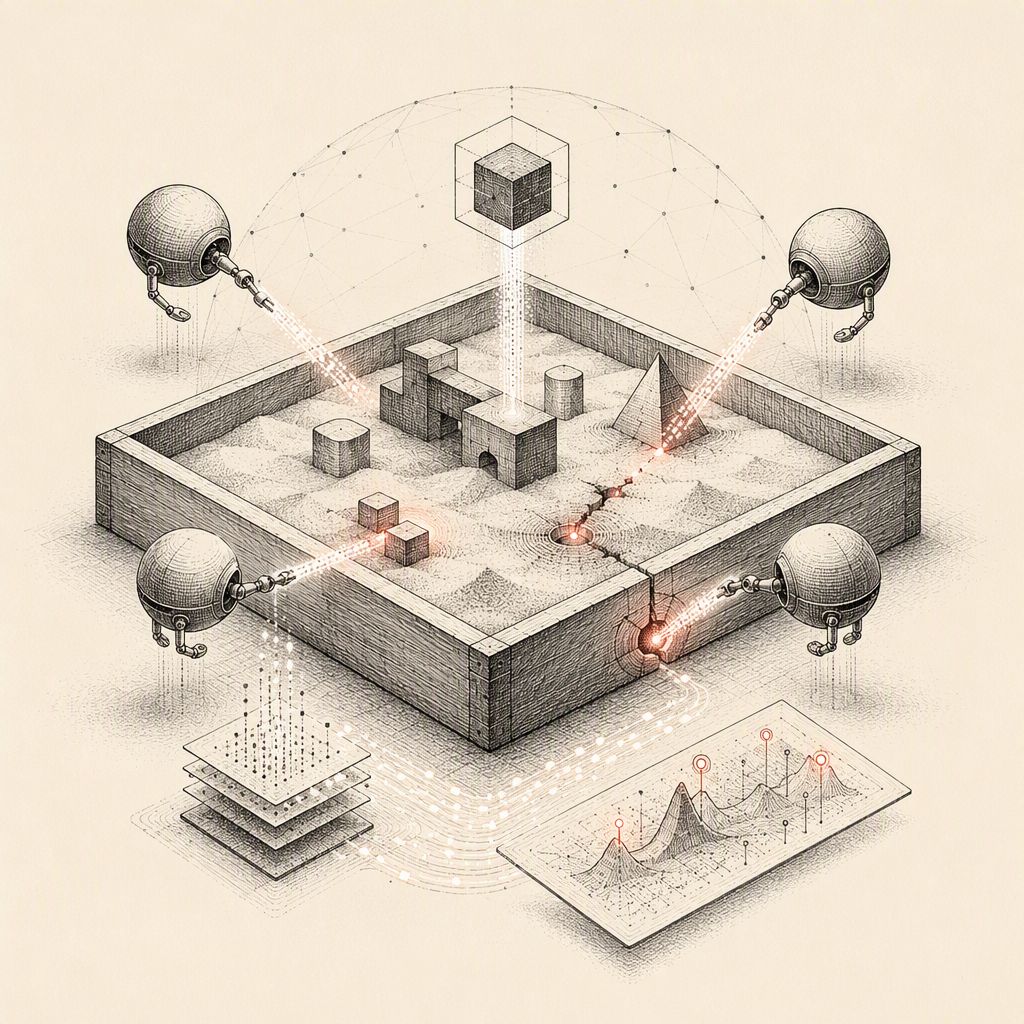
Vercel, a cloud platform for frontend developers, recently concluded a high-stakes bug bounty challenge that offered a $1 million reward for researchers who could escape its sandbox environment. The two-week program, running from August 18 to September 1, saw an impressive 1,285 submissions, highlighting the effectiveness of AI-assisted security research. While none of the submissions successfully accessed customer data, the challenge provided Vercel with valuable insights and led to the discovery of several critical vulnerabilities, prompting the company to enhance its automated triage processes.
The core of the challenge involved testing the security of Vercel's sandbox, which is built upon Firecracker microVMs and designed to isolate untrusted AI agent code. Researchers, both through black-box targeting via HackerOne and white-box analysis by Trail of Bits engineers, were tasked with finding ways to break out of this isolated environment. The sheer volume of reports necessitated the development of an advanced AI-powered triaging solution by Vercel, which could process, deduplicate, and even run proof-of-concept exploits within a real sandbox environment.
Among the most significant findings were two independent defects discovered in the Linux kernel's networking stack. One vulnerability leads to memory leaks from the host kernel, while the other can deterministically crash the host. These flaws carry substantial implications, as many major cloud providers rely on the same Linux kernel components for isolating customer workloads. The bug bounty program allowed Vercel to identify these issues two weeks before they were disclosed to kernel maintainers, underscoring the value of such focused security initiatives.
Details regarding the specific vulnerabilities and their pending CVE assignments are being kept confidential until they are publicly disclosed by the kernel maintainers. Vercel stated that fixes are currently under private review. This proactive discovery and reporting mechanism, facilitated by the bug bounty, allows for a more controlled and timely patching process, minimizing the window of exposure for affected systems.
The white-box testing conducted by Trail of Bits yielded 20 findings and provided architectural advice, including a crucial recommendation to "stop trusting the guest." This emphasizes the principle that any data crossing the boundary from a microVM should be treated as untrusted input and validated server-side, or signed with keys inaccessible to the guest environment. This architectural guidance is as valuable as the vulnerability discoveries themselves in hardening the platform.
The Vercel challenge also served as a proving ground for AI in security operations. The company's development of an agentic triaging solution, built on the Vercel Eve agent framework and running on Kimi K3, demonstrates a potential future for handling the escalating volume of security alerts. Vercel plans to open-source this triaging agent, offering a valuable tool for other organizations facing similar challenges.
Notably, Vercel's experience highlights a growing debate in the security community: the role of human oversight versus automated decision-making. In this instance, Vercel demonstrated confidence in its AI agent by removing human review from the loop to accelerate the triaging process. While customers often prefer human decision-making for assurance, the increasing speed of cyber threats may necessitate such automated responses, even if it introduces a degree of risk.
Ultimately, Vercel's sandbox challenge is deemed a success. The program not only validated the robustness of Vercel's sandbox, preventing any access to customer data, but also contributed to the broader security ecosystem through the discovery of critical Linux kernel flaws and the development of advanced AI-driven security tools. The lessons learned, particularly regarding AI-assisted research and automated triage, are likely to influence future security practices across the industry.