
Tuskira Vector Automates Red Teaming for Attack Surface Validation
Tuskira has launched Vector, an autonomous red teaming capability designed to identify and validate an organization's exploitable external attack surface by simulating attacker actions.
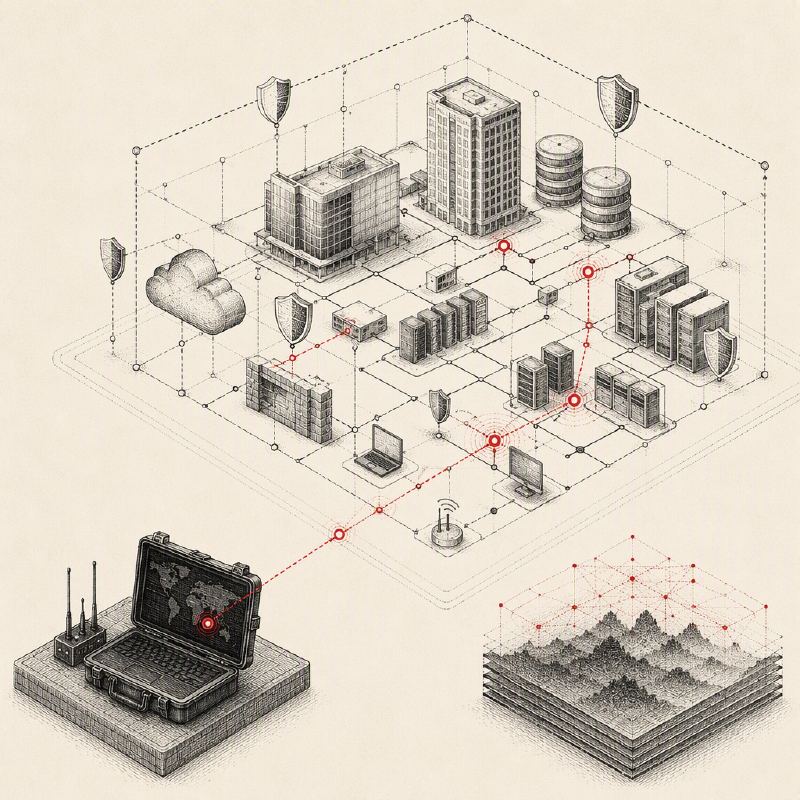
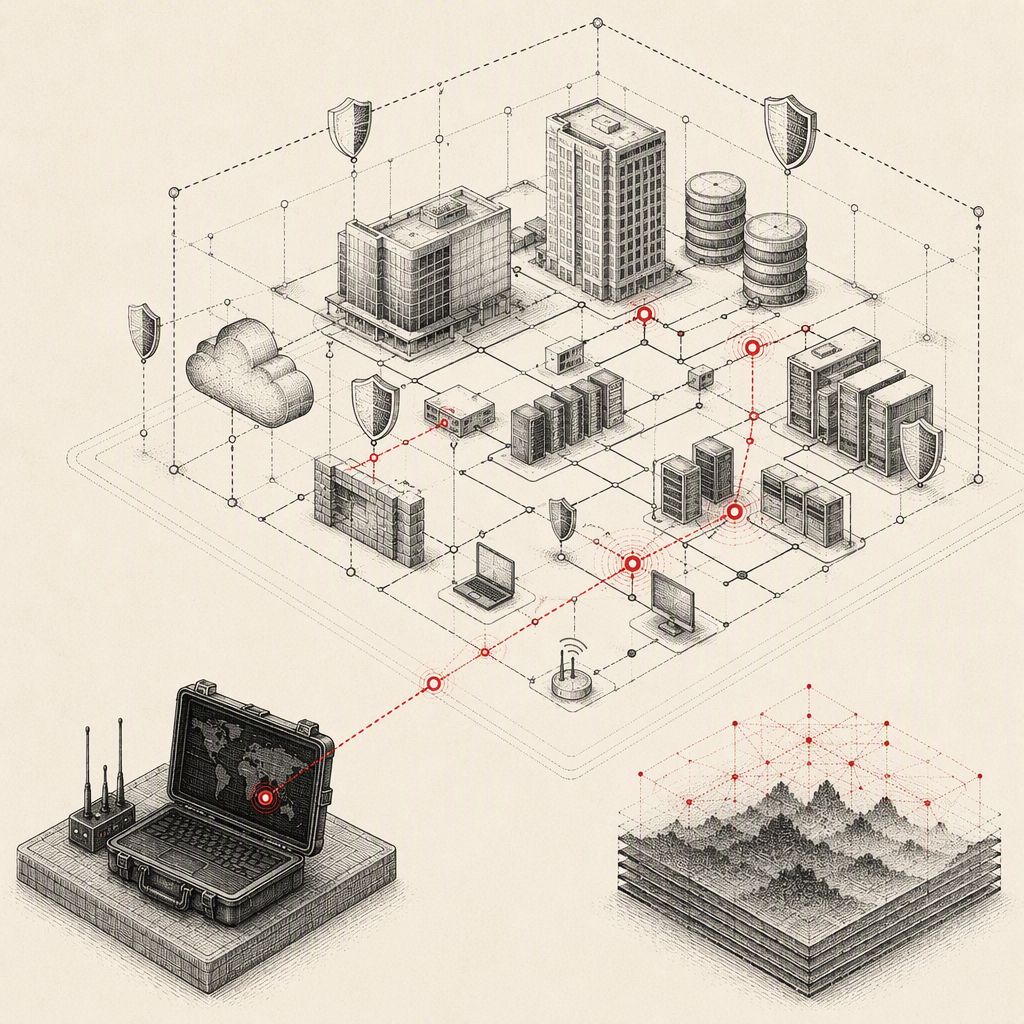
Tuskira has announced Vector, its autonomous red teaming agentic capability, which identifies an organization’s exploitable attack surface by simulating what an attacker can do from outside it.
Tuskira validates every external finding against the organization’s deployed compensating controls, the internal risks already reported by its security tools, and the architecture of its application and infrastructure topologies. The result is autonomous adversarial exposure validation across vulnerabilities, identities, and control configurations, so security teams act only on the exposures an attacker could actually use.
Tuskira’s Red Team Agent probes customer-approved external scope using emerging tactics, techniques, and procedures (TTPs), newly disclosed vulnerabilities, and AI-driven attack techniques. Rather than stopping at “exposed,” it uses Tuskira’s Security Data Fabric as context.
The fabric normalizes signals from third-party security tools into a live digital twin of the enterprise, covering security architecture, application and infrastructure topologies, deployed controls, and the risks those controls already report. Grounding adversarial testing in the enterprise’s own architecture lets Tuskira validate exposure at machine speed without blind exploitation against production systems.
With this release, security teams can see what attackers see by discovering internet-facing assets, services, identities, and misconfigurations across cloud, identity, endpoint, network, and on-prem environments. It also eliminates false positives by confirming exploitability against deployed compensating controls and internal risk context, and validates exposure autonomously through continuous adversarial testing.
Furthermore, Vector accelerates investigation and containment by reducing validation time and providing validated attack paths with context. It also reduces dependence on patching by recommending or staging high-leverage changes to existing controls, then re-testing to confirm the path is closed.
“Every organization has a list of what’s exposed. What they don’t have is a trustworthy answer to whether an attacker can actually get in, and what already stands in the way,” said Piyush Sharrma, CEO of Tuskira. “Our Red Team Agent tests from the outside the way an attacker would, then checks that answer against everything the enterprise knows about itself: its architecture, its controls, and the risks its tools are already reporting.”
This release extends Tuskira's previous Kairo offering, which was introduced in May 2026 to uncover deep, cross-domain breach paths. Vector adds red team sensors for current threat pictures and an agentic defense loop for prioritization, investigation, and response, verifying results. Tuskira's agents, including Kairo, Lattice, Quell, and Iris, work together on a shared model to map attack paths, validate exposures, assess CVE impact, and investigate alerts.