
ThreatBook Launches RedAgents AI Platform for Unified Penetration Testing
ThreatBook introduces RedAgents, a cloud platform that aggregates multiple AI-powered penetration-testing agents to identify system weaknesses through parallel testing.
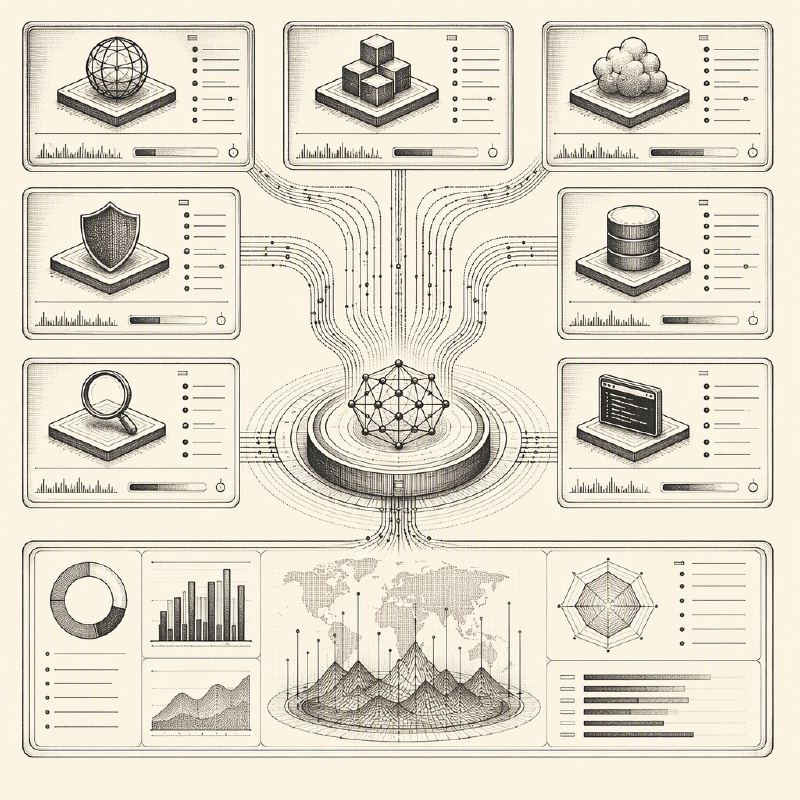
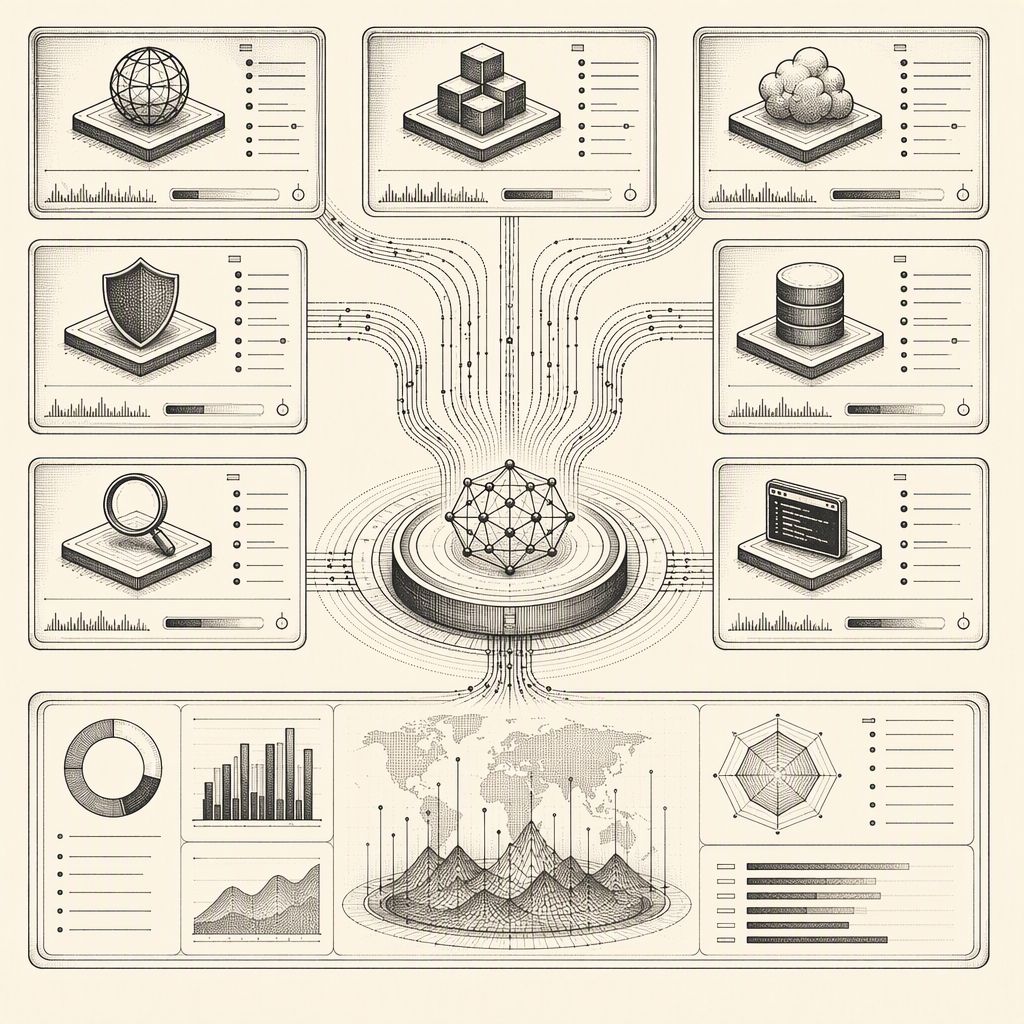
ThreatBook has launched RedAgents, a cloud platform that brings several AI-powered penetration-testing agents together to assess an organization’s systems. Announced on October 16, 2026, the service is designed to help security teams find weaknesses in their own networks by running multiple automated tests within a defined, authorized scope. ThreatBook states that the agents can work in parallel and present their findings and test logs in a unified view, offering a broader assessment than single-tool approaches.
The platform takes a different approach from relying on a single testing tool or provider. Each agent may look for different issues, so combining their results could give defenders a more comprehensive view of their exposure. The launch announcement describes RedAgents as a software-as-a-service platform for security operations teams, rather than a new malware family or a report on a specific intrusion. ThreatBook’s announcement also notes that the service brings together agents with different origins and capabilities. Those named at launch include Artex Pro, Cyber(YanJi), Yanxun, and CyberStrikeAI Enterprise Edition.
RedAgents acts as an aggregator, connecting multiple AI penetration-testing agents through one platform and enabling them to run in parallel. A penetration test is an authorized review in which testers look for weaknesses in systems before malicious actors can exploit them. Running agents side by side may help uncover issues that a single tool misses, though the value of the results depends on how accurately the agents test and report. ThreatBook says the platform consolidates findings, test data, and logs in a unified view, potentially reducing the need for teams to move information between separate tools. The approach is similar to using multiple scanners or testing teams, but RedAgents is designed to coordinate AI agents as part of a single assessment.
The four named agents have distinct backgrounds. ThreatBook describes Artex Pro as the enterprise version of Artex, an autonomous penetration-testing agent. Cyber(YanJi) is a Python-based agent that searches for a route from a starting point to a defined goal. Yanxun is described as a system that coordinates specialist agents, while CyberStrikeAI Enterprise Edition is based on an AI-native testing tool that ThreatBook acquired in September 2026. These descriptions are based on the company’s announcement and should be viewed as vendor claims.
Automated testing tools can cause disruption if they probe systems without permission or exceed an agreed scope. ThreatBook emphasizes that RedAgents allows customers to define an allowlist of approved targets and that agents must operate within those authorized limits. Organizations should still confirm the scope, timing, rate limits, and test conditions before running any penetration test, especially on systems that support business operations. The company also states that customer test data stays within the ThreatBook environment and is not sent to third-party agents, supporting Zero Data Retention (ZDR) for complete deletion of test data.
The launch comes as more security products leverage AI agents to automate parts of testing. Products like PentestCode’s AI testing agent and Xalgorix’s verification-focused platform differ in deployment and findings handling. Teams should compare scope controls, evidence quality, and data handling rather than treating "AI pentesting" as a uniform category.
The main promise of RedAgents is breadth: multiple agents may explore a target in different ways, providing teams with a combined view of possible weaknesses. However, this does not guarantee that every result is valid or that every vulnerability will be found. Security staff still need to review evidence, reproduce important findings safely, and prioritize fixes based on business impact and exposure. ThreatBook claims the platform can reduce false positives by combining agent results, but the announcement does not provide independent accuracy figures or a false-positive rate.
ThreatBook plans to add more open-source agents over time, alongside the enterprise tools available at launch. RedAgents is available through the company’s website, where organizations can request a trial. The platform's distinction lies not in a single testing method but in its central coordination of several agents for comprehensive security assessments.