
Tenable Integrates with OpenAI Daybreak Defense Factory for Streamlined Code Remediation
Tenable One now integrates with OpenAI's Daybreak Defense Factory, allowing developers to import code security findings directly into their local development environment for faster remediation.
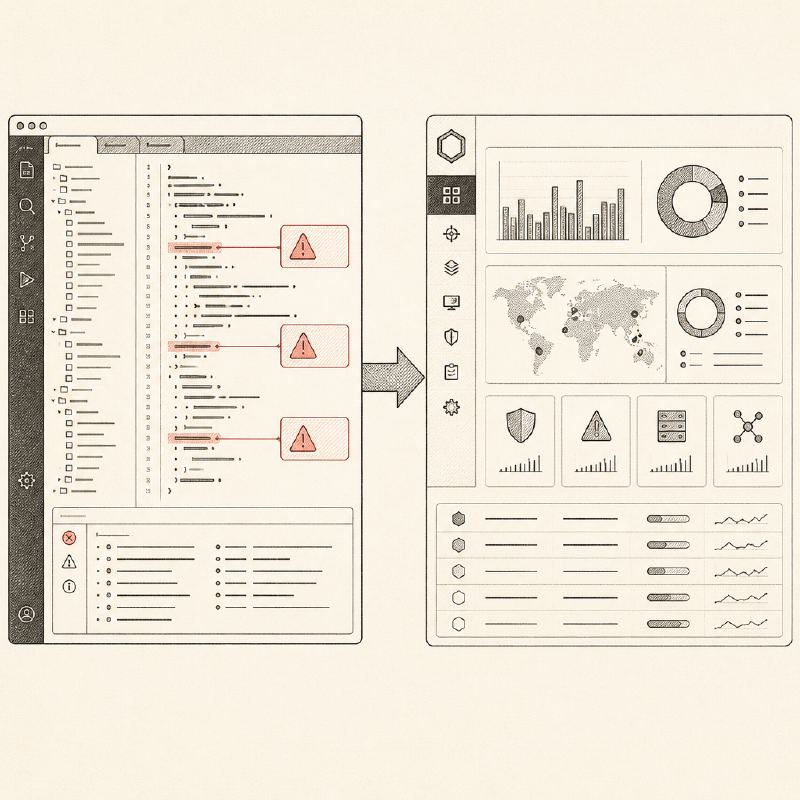
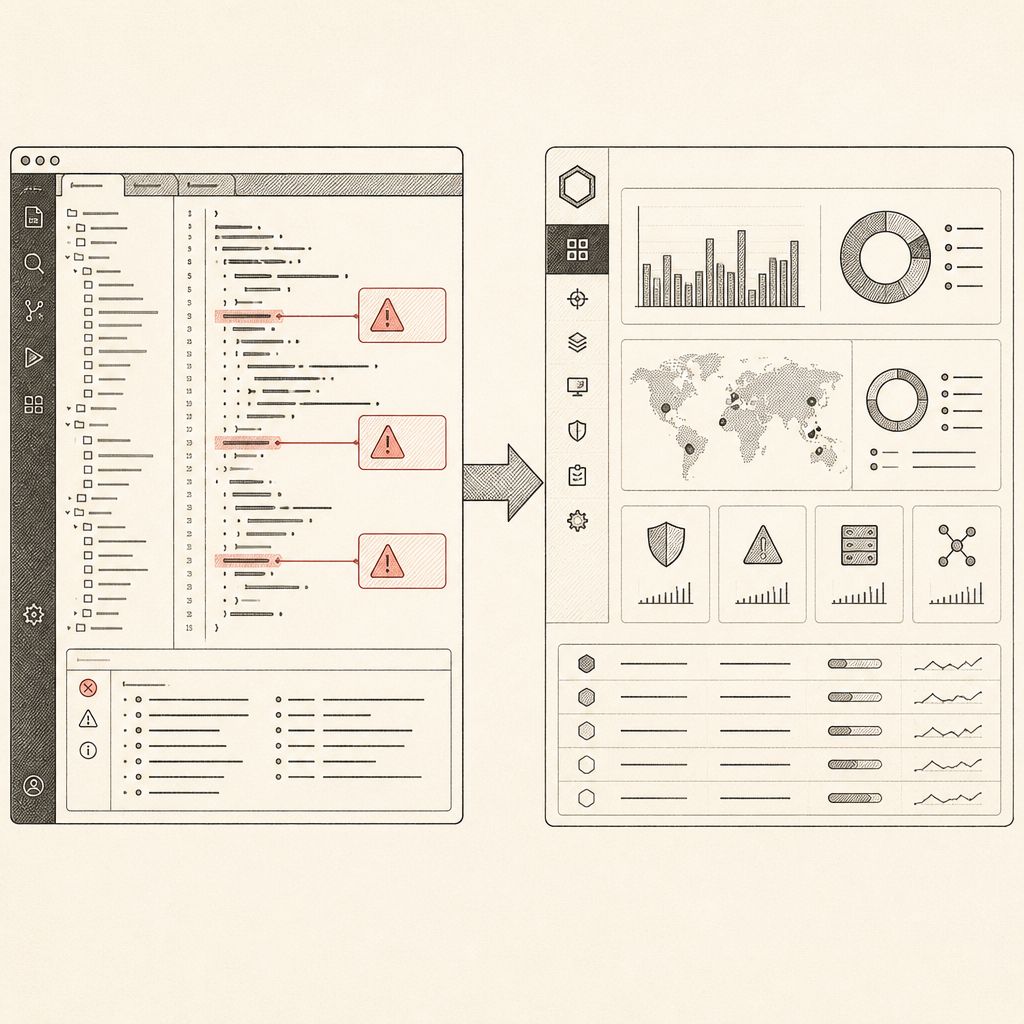
Tenable is enhancing its code security offerings by integrating its Tenable One Exposure Management Platform with OpenAI's Daybreak Defense Factory. This new integration, developed by OpenAI, aims to bridge the gap between security teams and developers by bringing vulnerability context directly into the developer's workflow.
Traditionally, code security findings often lose critical context during the handoff process. Security teams typically export findings or create tickets, which developers then have to re-investigate to understand the affected code and the necessary remediation steps. This often leads to delays and inefficiencies, as much of the context already existed with the security team but wasn't effectively transferred.
The integration utilizes a Codex Security CLI, an open-source tool published by OpenAI. This CLI allows developers to import selected Tenable One findings directly into their local development environment. Each imported finding includes its name, severity, state, and crucially, Tenable's detailed description and recommended solution.
To implement this, users select specific code repository findings within Tenable One. These findings can then be exported via the Inventory Export API or from existing CSV files. The Codex Security CLI then imports these findings into the developer's local workbench, associating them with the relevant code checkout. This ensures that developers have the necessary information at their fingertips to begin fixing vulnerabilities without extensive re-investigation.
The Daybreak Defense Factory is designed to assist developers in investigating affected code, prioritizing findings, and proposing fixes. By having Tenable's vulnerability data readily available alongside the code, developers can more efficiently address security issues, leading to a more streamlined and secure development lifecycle.
This collaboration underscores a growing trend in the cybersecurity industry: shifting security left and embedding security practices earlier in the development process. By providing developers with actionable security intelligence directly within their familiar tools and environments, organizations can significantly reduce their attack surface and improve their overall security posture.
Developers can try out this integration today by following OpenAI's setup guide, which provides detailed commands and helper scripts for importing Tenable One findings into their local Codex Security environment. The integration supports maintaining finding IDs and file paths, further aiding in precise remediation efforts.