
Sticky Note on Monitor Provided Keys to the Company's Kingdom
A penetration tester discovered critical company credentials written on a sticky note attached to an employee's monitor, leading to unauthorized access to sensitive data.
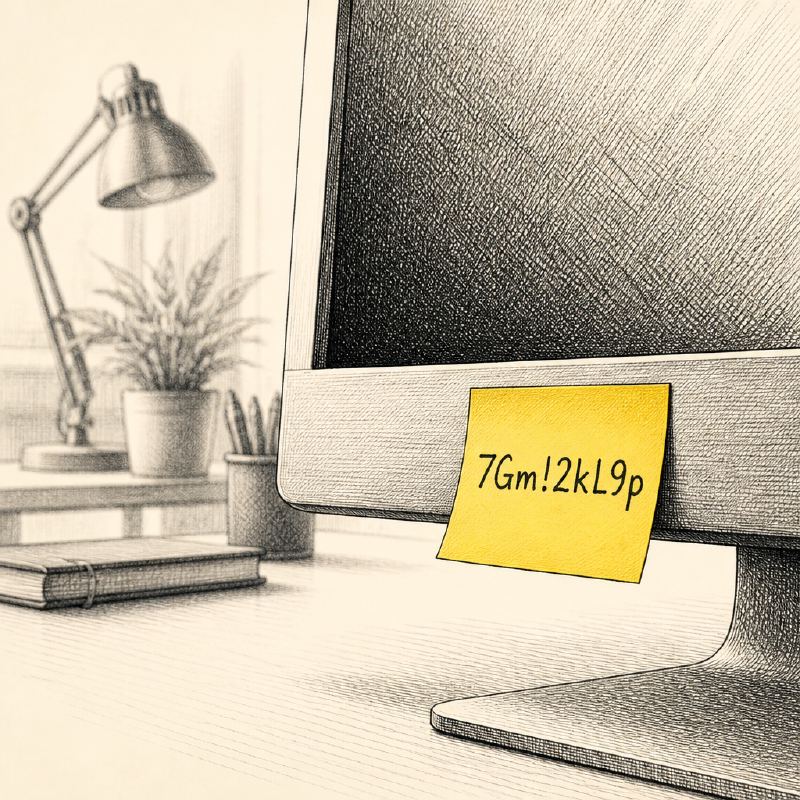
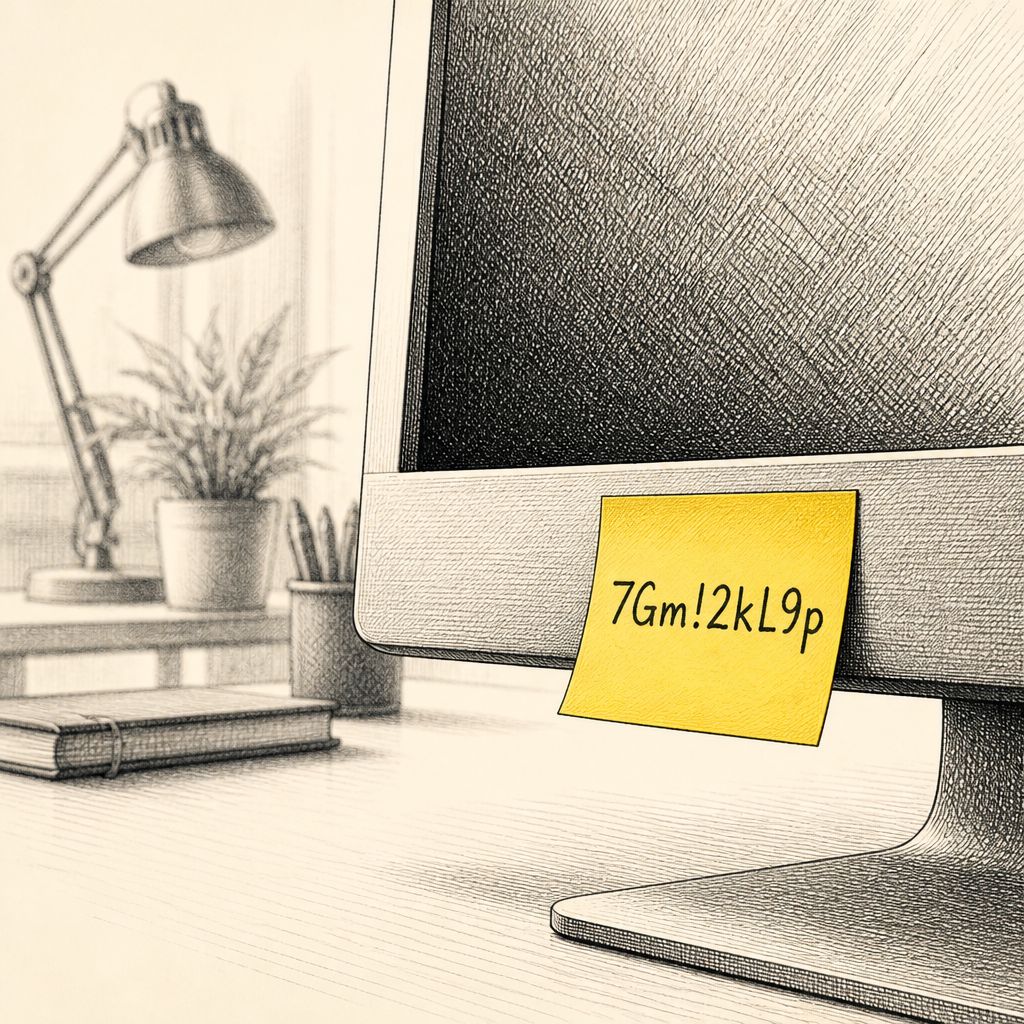
A penetration tester has exposed a critical security lapse where an employee's password, written on a sticky note affixed to their monitor, granted unauthorized access to a company's network. Christian Espinosa, CEO of Blue Goat Cyber, detailed the incident, emphasizing how often physical security vulnerabilities are overlooked in favor of technical defenses.
During a routine client walkthrough, Espinosa observed the password on the monitor. He noted that while physical password storage in a secure notebook might be acceptable, leaving credentials visible on a workstation is a significant risk. "Physical security vulnerabilities are neglected much more often than technical security vulnerabilities and firms invest in firewalls where a sticky note is placed 3 feet from the front door," Espinosa stated.
Espinosa successfully used the discovered password to log into the employee's account. Subsequently, he utilized the same credentials to access the company's VPN, gaining broad access to internal network resources. This initial breach opened the door to further sensitive information.
Once connected to the VPN, Espinosa found an HR folder containing a wealth of personally identifiable information (PII) on employees, including home addresses, driver's license scans, W-4 forms, and salary data. He also located documents detailing internal server names and administrative contacts, as well as instructions for accessing the accounting server.
The accounting server proved to be a particularly rich target, housing vendor banking information, invoices, and payment records. Espinosa highlighted that the credentials from a simple sticky note could have been leveraged for various fraudulent activities, including payroll fraud, identity theft, and vendor-payment fraud.
Following the demonstration of these vulnerabilities, the client took immediate action. The compromised account was disabled, and the company initiated a review of VPN access logs to identify any other potential unauthorized access. A physical sweep of the office was also conducted to find any other exposed credentials.
To mitigate the risks, the organization tightened access permissions on sensitive HR and accounting shares, ensuring that only essential personnel could access the data. The incident served as a stark reminder of the importance of basic security hygiene and robust access control policies.
Espinosa underscored the potential for continued exploitation, noting that an external actor could have easily photographed the sticky note and used the credentials later to access sensitive records remotely. The incident underscores the critical need for comprehensive security awareness training that addresses both digital and physical security risks.