
Sophisticated Phishing Infrastructure Demands Advanced Threat Intelligence
US SOCs and MSSPs must leverage advanced threat intelligence to combat increasingly complex phishing operations that utilize legitimate cloud services and multi-stage redirects.
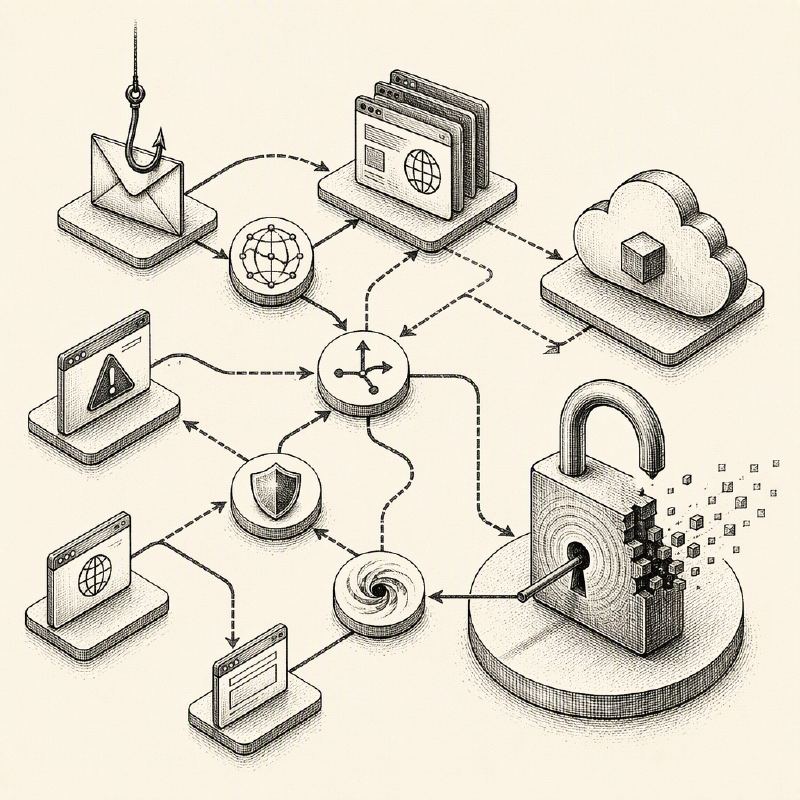
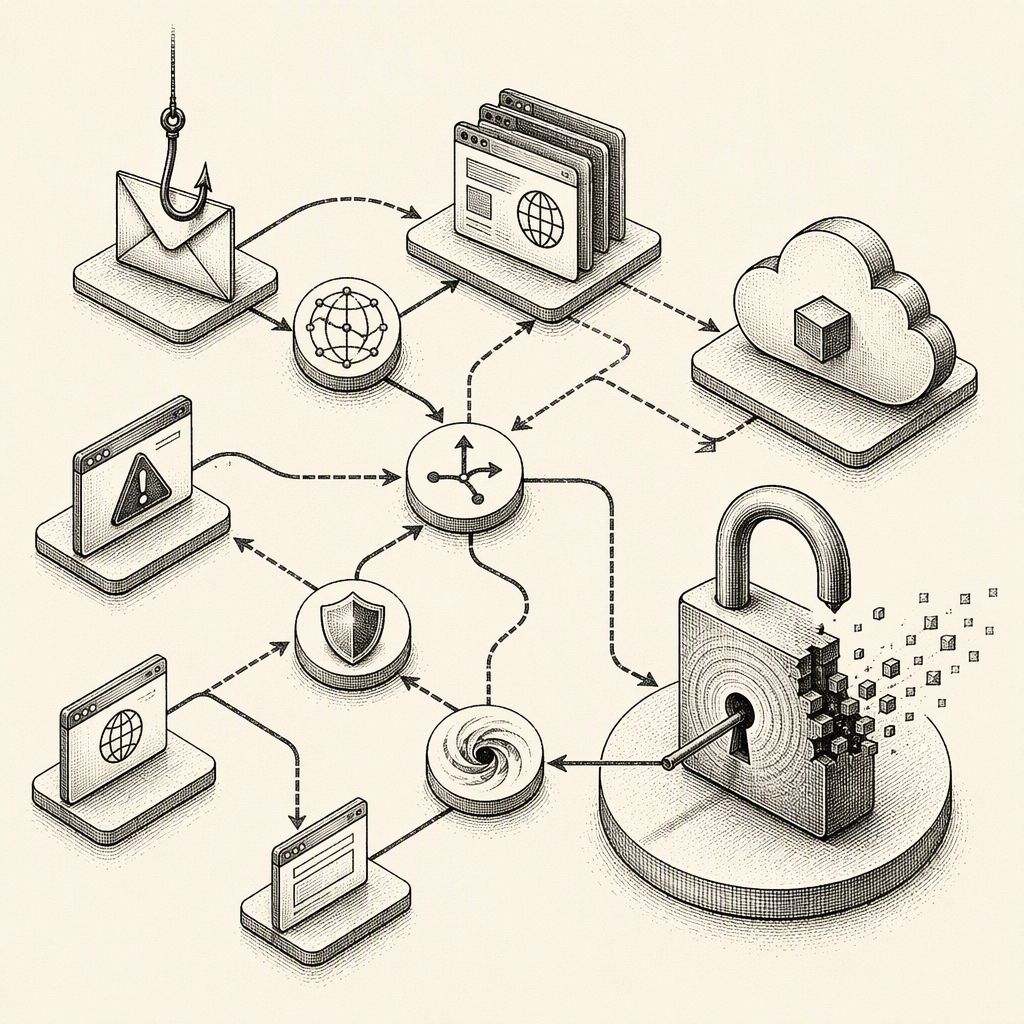
Phishing continues to be a pervasive threat, evolving beyond simple malicious emails to encompass intricate infrastructures. Modern attacks often involve a chain of components, including newly registered domains, compromised websites, redirectors, sophisticated phishing kits, and credential harvesting pages. Attackers are increasingly leveraging legitimate cloud services and authentication mechanisms, making individual elements of an attack appear less suspicious in isolation. This complexity presents a significant visibility challenge for US-based Security Operations Centers (SOCs) and Managed Security Service Providers (MSSPs).
The underlying infrastructure supporting phishing campaigns has become considerably more complex. Attackers can host malicious content on legitimate platforms, compromise existing websites, employ multi-stage redirects, and utilize familiar authentication methods. Some phishing pages are even designed to adapt their behavior based on the visitor, complicating automated analysis and reputation-based detection. The first half of 2026 saw a dramatic surge in OAuth device-code phishing, increasing by 483.7%, according to ANY.RUN's H1 2026 Cyber Risk Report. This report also highlighted a 90.7% increase in the abuse of cloud infrastructure, underscoring the growing trend of attackers utilizing legitimate services.
These evolving tactics mean that attackers no longer require infrastructure that immediately appears malicious. A campaign might use a legitimate service for one stage, a newly registered domain for another, and a compromised website elsewhere in the attack chain. The indicators of compromise can change rapidly, while the core campaign may remain consistent. This dynamic necessitates a focus on the relationships between these indicators, making threat intelligence crucial for identifying connections and potential broader campaigns.
The consequences of a phishing attack can extend far beyond initial credential theft. A stolen password can lead to account takeover, while a compromised session, particularly in platforms like Microsoft 365, can grant attackers access without immediately needing to use stolen credentials. Compromised executive or finance accounts can introduce risks that significantly impact business operations.
The "CSuite" campaign, analyzed by ANY.RUN, exemplifies this trend. This operation employed lures impersonating legitimate services such as Adobe, DocuSign, Zoom, SharePoint, and Microsoft 365. The campaign integrated phishing with Microsoft 365 session theft and the use of legitimate remote management software. Notably, US organizations constituted 60% of the identified victim organizations and 51% of related Interactive Sandbox submissions in the research, indicating a significant focus on American targets.
What makes the CSuite campaign particularly concerning is that the phishing page was not the ultimate objective. It served as a component within a broader attack chain that incorporated identity compromise and remote access techniques. For SOCs and MSSPs, discovering even one domain or URL associated with this chain can provide a critical starting point for a more extensive investigation into the full scope of the compromise.
Threat intelligence plays a pivotal role in enhancing phishing detection by providing essential context around suspicious activities. It helps analysts determine whether a domain, URL, or IP address is linked to known malicious infrastructure or a larger, ongoing campaign. This intelligence can aid in identifying new infrastructure before it reaches end-users and connect disparate indicators to related domains, IPs, and campaigns. Furthermore, threat intelligence reports help security teams understand emerging techniques, enabling them to adapt their defenses proactively. Interactive sandbox environments, like ANY.RUN's, are invaluable for this, allowing real-time analysis of malware and phishing activity by observing redirects and network behavior.
By integrating continuously updated threat intelligence feeds into SIEM, SOAR, email security, DNS, firewall, and endpoint controls, SOCs and MSSPs can better keep pace with the rapidly evolving landscape of phishing campaigns. This allows them to respond more effectively to attackers who can quickly abandon compromised infrastructure and establish new ones, ensuring a more robust and informed defense posture.