
ShinyHunters Exploited Oracle PeopleSoft Zero-Day, Revealed as Chained Flaws
What was initially tracked as a single critical Oracle PeopleSoft zero-day vulnerability, exploited by the ShinyHunters group, has been detailed by researchers as a chain of three distinct vulnerabilities.
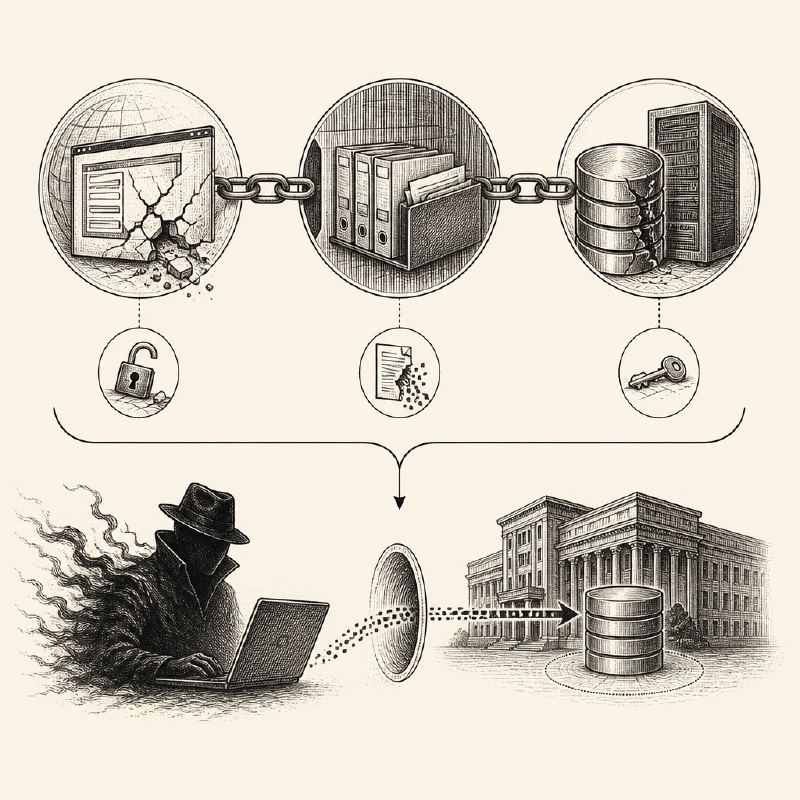
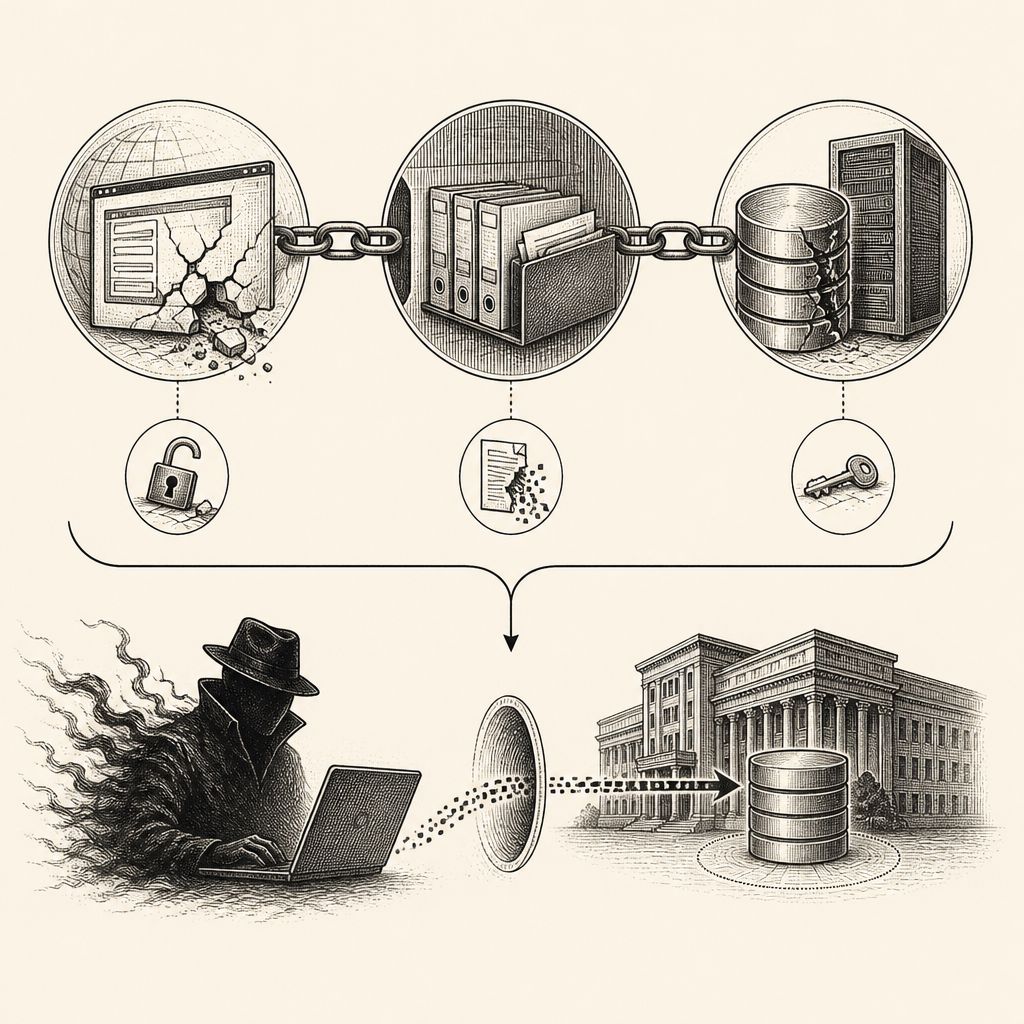
Researchers have revealed that a critical zero-day vulnerability affecting Oracle PeopleSoft, which has been actively exploited by the threat group ShinyHunters since May, is in fact a chain of three separate vulnerabilities. Oracle patched these flaws in June under a single identifier, CVE-2026-35273, but the Zero Day Initiative (ZDI), which reported the issue, is working with Oracle to assign individual CVEs to each of the three distinct flaws.
The exploit chain begins with a server-side request forgery (SSRF) vulnerability within the PeopleSoft Integration Gateway (PSIGW). This flaw allows an unauthenticated attacker to craft a request that PeopleSoft's gateway forwards to an internal management interface. The vulnerability is exacerbated by PeopleSoft's default trust in requests originating from its own loopback address (127.0.0.1), which is pre-configured in the allowedhosts.properties file. This trust mechanism allows an attacker to bypass security controls and access sensitive internal administrative functions.
Once an attacker gains access to the internal management interface, the Environment Management Hub (PSEMHUB), they can leverage two distinct methods to achieve remote code execution. The first method abuses a logging function within PSEMHUB, allowing an attacker to control the content and destination path of log entries. By writing a web shell to the application directory, an attacker can then execute commands on the server with the privileges of the PeopleSoft service account. This method provides a direct path to full system compromise.
The second method for achieving code execution involves crafting a malicious XML file. When PSEMHUB processes this file upon service restart, it uses Java's XMLDecoder. This allows an attacker to embed malicious code within the XML, which is then executed by the decoder without the need to plant a traditional web shell. This technique is particularly stealthy, as it leaves fewer artifacts for standard detection mechanisms to identify, making post-exploitation forensics more challenging.
This vulnerability chain, tracked as CVE-2026-35273, affects PeopleSoft Enterprise PeopleTools versions 8.61 and 8.62 and carries a critical CVSS score of 9.8. It enables unauthenticated attackers to gain complete control over the affected server over the network. Oracle released an out-of-band patch on June 10, and the vulnerability was subsequently added to CISA's Known Exploited Vulnerabilities (KEV) catalog.
Prior to Oracle's patch, threat actors, including the ShinyHunters group (tracked by Mandiant as UNC6240), actively exploited this vulnerability. Initial targets were primarily universities, but a subsequent wave in September expanded to include technology, IT services, healthcare, agriculture, transport, and government sectors, affecting dozens of systems globally. Mandiant noted that attackers were able to bypass Web Application Firewall (WAF) rules by using URL encoding for specific paths, further highlighting the exploit's effectiveness.
To mitigate this threat, organizations are urged to apply Oracle's security patch for CVE-2026-35273 immediately. If patching is not feasible, Oracle's advisory recommends disabling the Environment Management Hub service or removing the PSEMHUB application. For organizations that may have already been compromised, Mandiant advises treating any host with a web shell as fully compromised, preserving evidence, and rotating all credentials accessible from the PeopleSoft tier. It is important to note that patching closes the vulnerability, but it does not automatically remove any unauthorized access or malicious artifacts left by attackers already present within the system.