
ShinyHunters Enters 'Reaping Phase' Amidst Exploitation of Multiple Critical Vulnerabilities
The threat group ShinyHunters is reportedly exploiting critical vulnerabilities in NetScaler, Zimbra, SharePoint, and Atlassian products, marking a shift to an active exploitation phase following the detention of a key member.
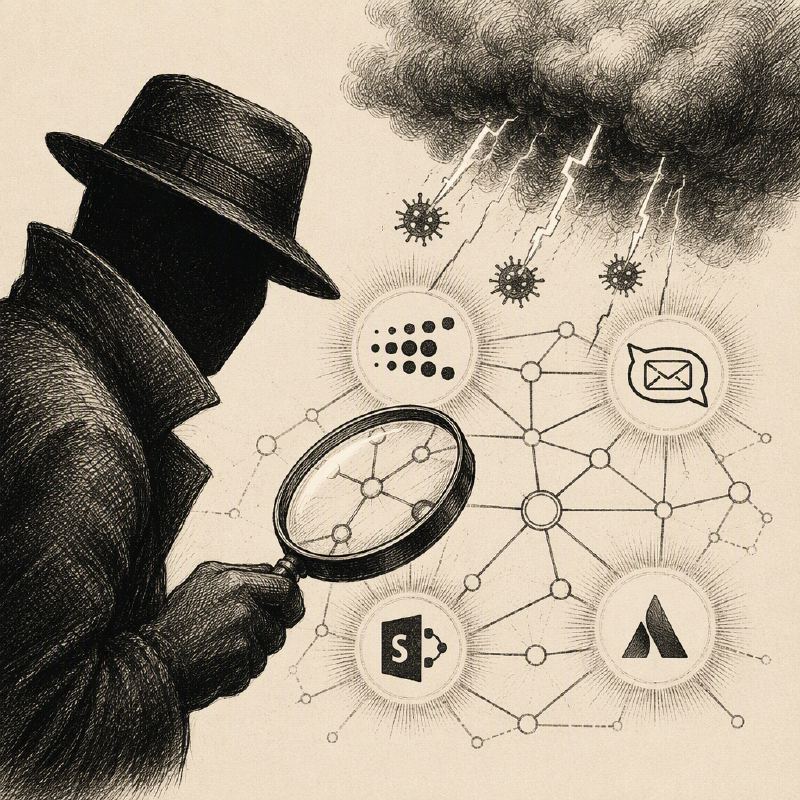
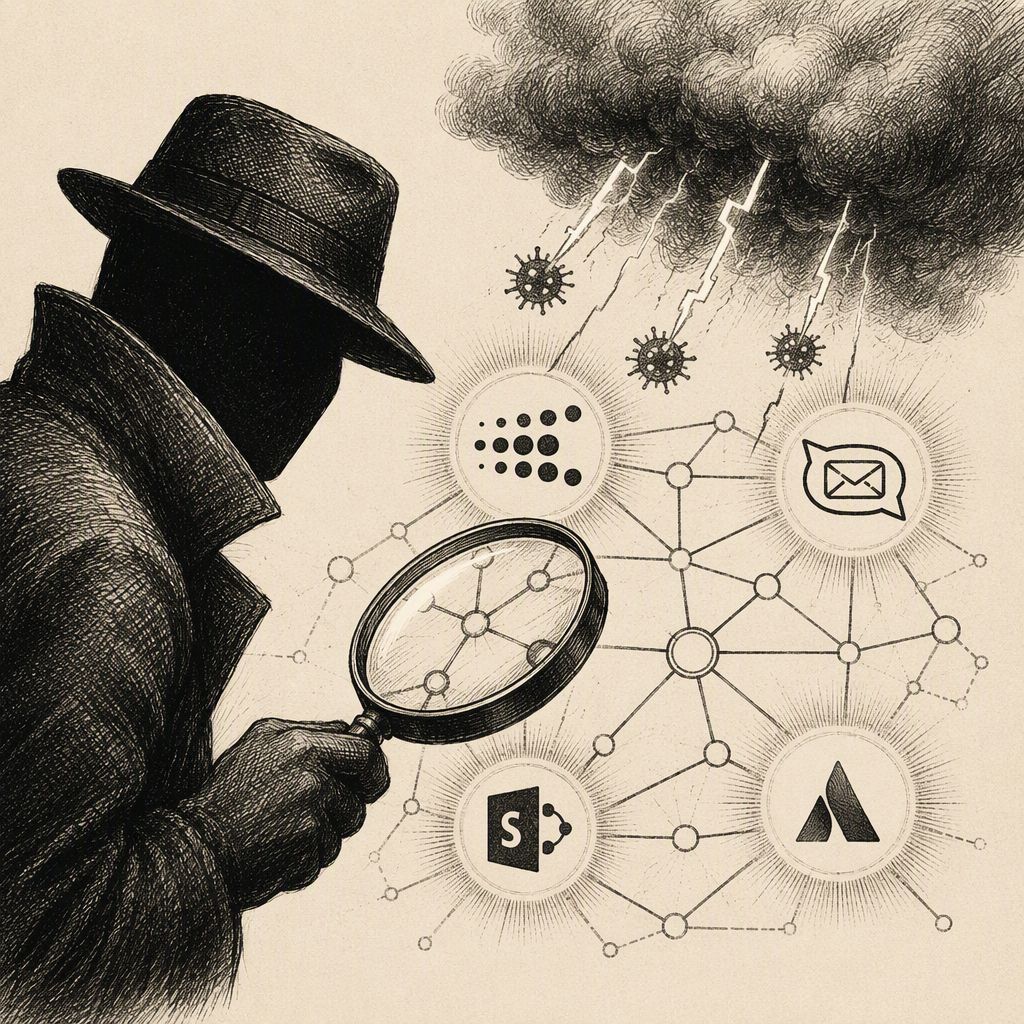
The notorious data theft group ShinyHunters has transitioned from its previous "sowing" activities to a "find out" or "reaping" phase, actively exploiting a range of critical vulnerabilities across popular enterprise software. This shift in tactics comes after the detention of a key ShinyHunters operative who is reportedly cooperating with authorities.
The group is reportedly leveraging zero-day vulnerabilities in NetScaler devices, alongside known flaws in Zimbra, Microsoft SharePoint, and Atlassian products. Specifically, multiple critical flaws, including NetScaler RCE zero-days and a SharePoint vulnerability (CVE-2026-65660), are being actively exploited in the wild. This widespread exploitation suggests a coordinated effort to maximize impact and potentially monetize stolen data or access.
Citrix has issued urgent warnings for users to upgrade their NetScaler instances, confirming that two RCE zero-days are already being actively exploited. Similarly, attackers have been observed exploiting a critical Zimbra flaw to steal emails, and a public proof-of-concept for an Atlassian vulnerability has led to its exploitation.
The involvement of ShinyHunters in these exploits is significant. The group gained notoriety for its large-scale data breaches, often exfiltrating sensitive information from compromised organizations. Their move to actively exploit known and zero-day vulnerabilities indicates a potential escalation in their operational tempo and a desire to capitalize on previously identified weaknesses.
This development also occurs in the context of law enforcement actions against the group. The detention of a key member in Jordan, who is allegedly cooperating with authorities, could be a factor influencing ShinyHunters' current operational strategy. It remains to be seen whether this cooperation will lead to further disruption of the group's activities or provide valuable intelligence to investigators.
Organizations using NetScaler, Zimbra, SharePoint, and Atlassian products are strongly advised to review their security postures and apply necessary patches and mitigations immediately. The active exploitation of these vulnerabilities by a well-known threat actor like ShinyHunters underscores the critical need for prompt patching and robust security monitoring to prevent further compromise.
The situation highlights a recurring pattern in the cybersecurity landscape: threat actors often adapt their tactics in response to law enforcement actions, either by going deeper underground or by accelerating their exploitation efforts to achieve maximum impact before potential disruption. The "find out" phase for ShinyHunters appears to be a direct consequence of these pressures, making it a critical time for defenders to remain vigilant.