
Researchers Leverage TTY Logs to Track Over 3,130 Actors on DShield Sensors
A new script developed by SANS Internet Storm Center researchers parses TTY logs from DShield sensors, revealing over 3,130 unique actors executing similar crontab commands over a 90-day period.
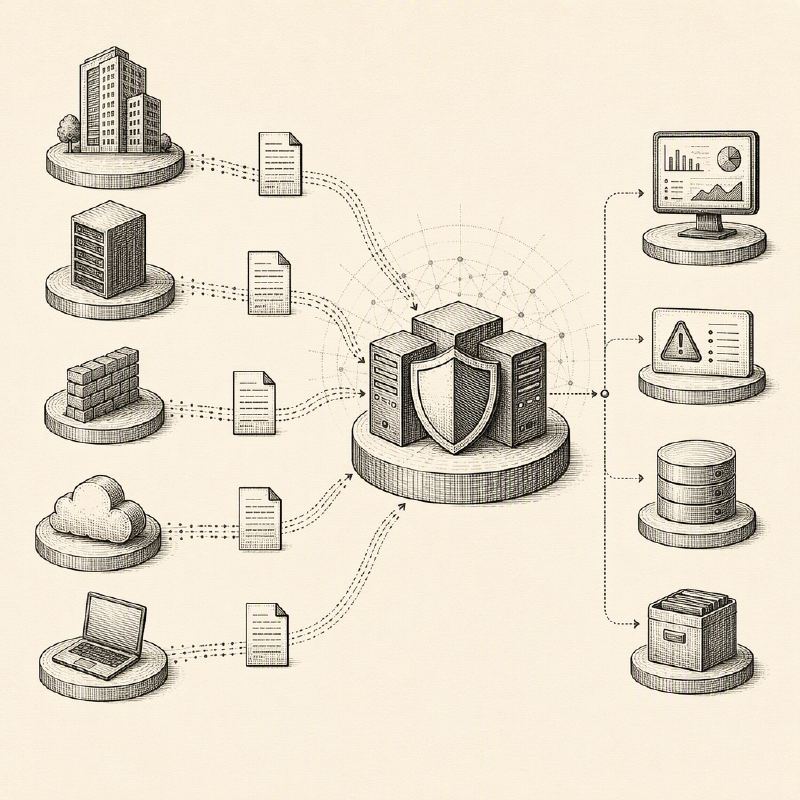
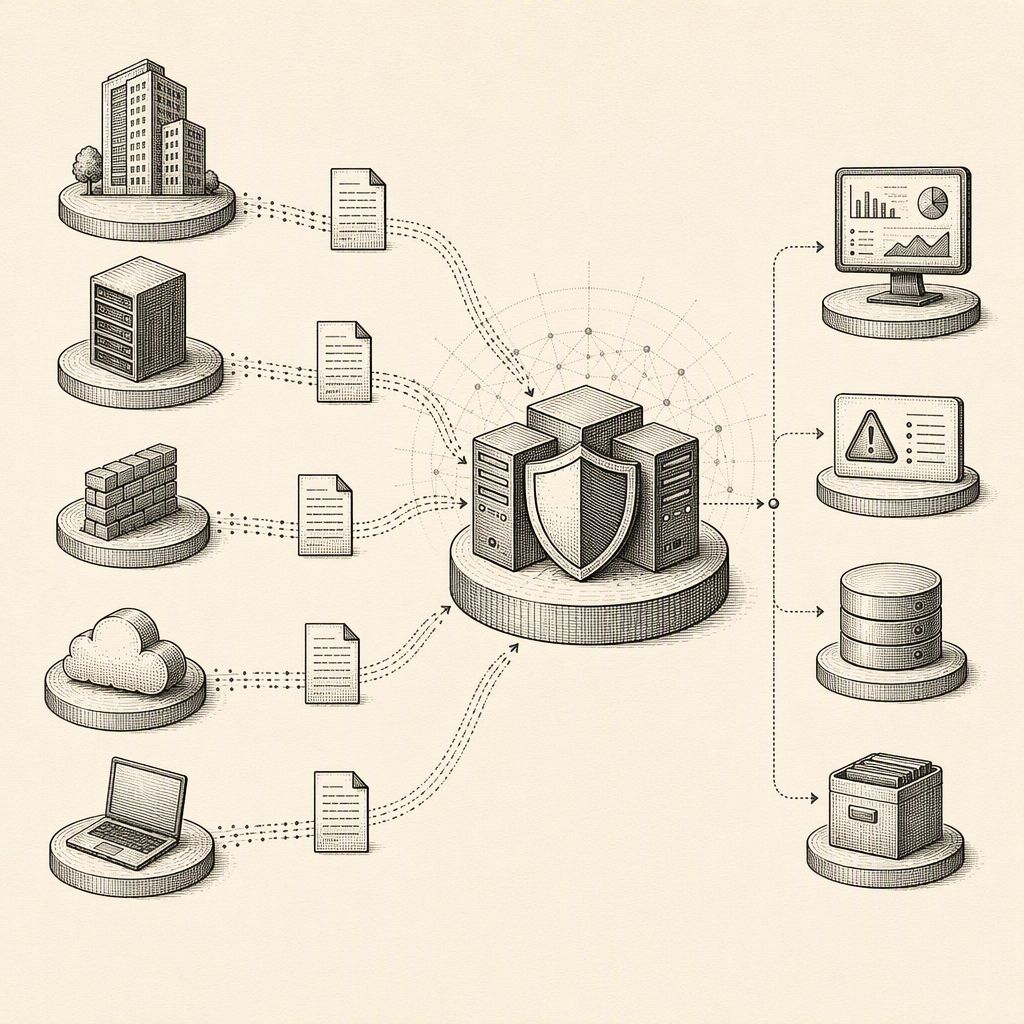
Security researchers have developed a novel script designed to parse and transmit TTY logs generated by activity on DShield sensors. These logs capture the commands executed by actors or bots after gaining access to the sensors. The script automates the daily collection of these logs and forwards them to the DShield SIEM (Security Information and Event Management) system for comprehensive correlation with other security data.
The primary goal of this initiative is to enhance the tracking and analysis of bot and actor activity within the DShield sensor network. By centralizing and analyzing TTY log data, researchers can gain deeper insights into the tactics, techniques, and procedures employed by malicious entities attempting to compromise or utilize these sensors.
Utilizing an ES|QL query, the researchers were able to identify a significant pattern: over 3,130 distinct actors were observed executing similar crontab commands. This identification was made possible by analyzing TTY log hashes over a 90-day period, effectively grouping together disparate activities that shared a common underlying command structure.
The query specifically targeted a transaction ID associated with a set of five similar crontab commands, which were then translated from their hash equivalents. This analysis revealed the sheer scale of the coordinated or opportunistic activity, highlighting the widespread use of these specific commands across a large number of unique actors.
The data presented includes a breakdown of the top 10 IP addresses and their associated Autonomous System Numbers (ASNs) observed engaging in this activity. This information is crucial for understanding the origins and infrastructure used by these actors, potentially aiding in attribution and the development of more effective defensive measures.
The script and associated SIEM integration are part of an ongoing effort to improve the visibility and analysis capabilities for DShield sensor data. The researchers have made the script publicly available on GitHub, encouraging community contribution and further development in log parsing and analysis techniques.
This approach demonstrates the power of log analysis and correlation in uncovering hidden patterns of malicious activity. By focusing on specific log types like TTY logs and employing powerful query languages, security teams can move beyond simple event detection to a more proactive and insightful understanding of the threat landscape.