
Ransomware Recovery: Bridging the CEO-CISO Divide with Tested Plans
Ransomware attacks force a critical divergence in organizational response, pitting executive concerns over payment against CISO priorities for system restoration. Proactive, documented recovery testing in isolated environments, coupled with robust network segmentation, is presented as the key to aligning these objectives and ensuring business continuity.
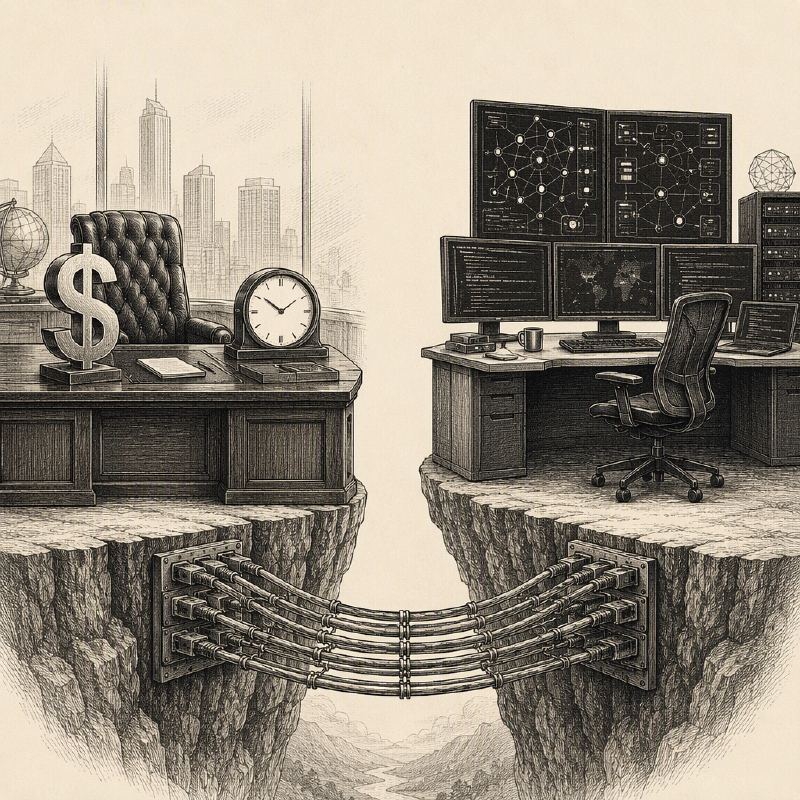
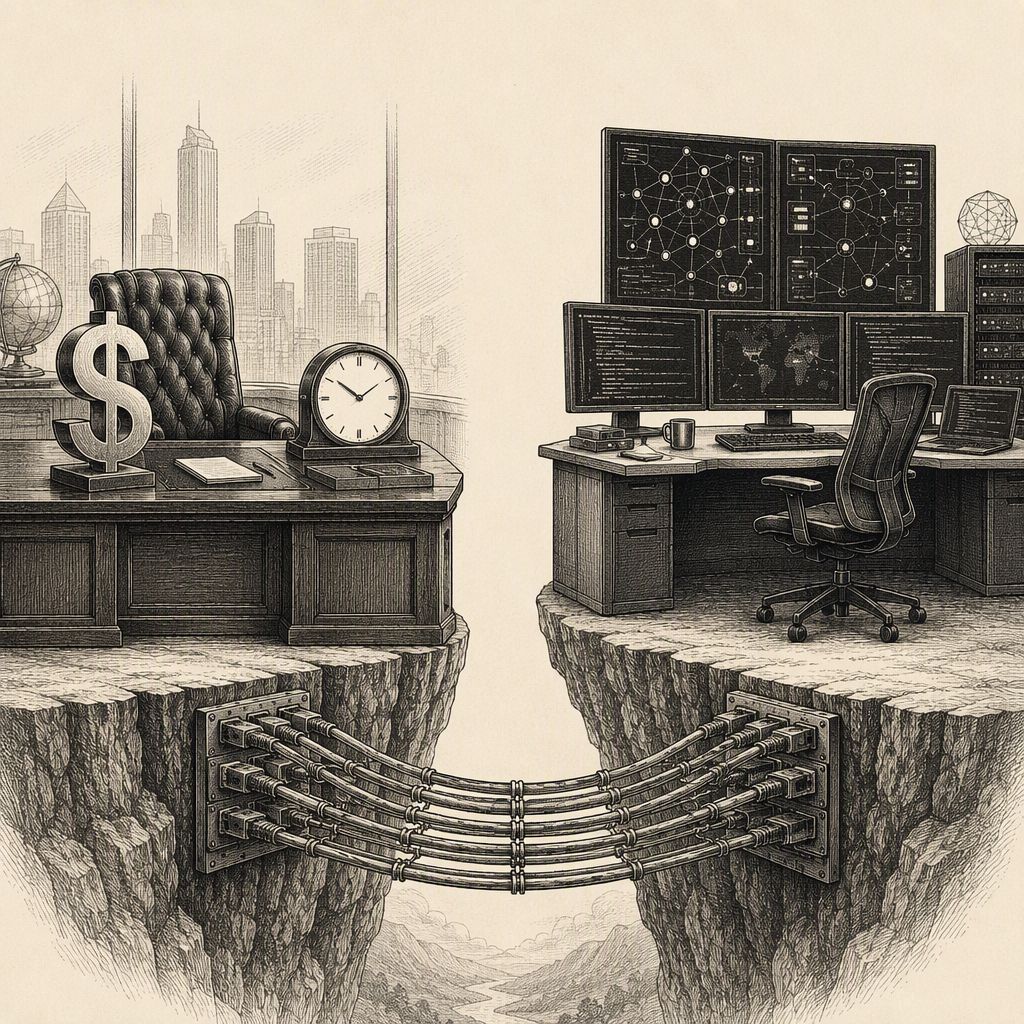
When ransomware strikes, the immediate aftermath often creates a stark dichotomy in organizational response. For Chief Executive Officers, the primary concern frequently revolves around the immediate financial implications and the agonizing question of whether to pay the ransom to regain access to encrypted data. This perspective is driven by the potential for catastrophic business interruption and the perceived speed of recovery that a payment might offer.
Conversely, Chief Information Security Officers and their teams face the complex technical challenge of restoring systems and data. Their focus is on the integrity of backups, the security of the recovery process, and ensuring that a successful restoration does not inadvertently reintroduce the threat. This technical imperative often clashes with the executive pressure to resume operations as quickly as possible, regardless of the underlying risks.
The article posits that this divergence, while understandable, can be effectively bridged through a proactive and disciplined approach to disaster recovery and business continuity planning. The core recommendation is the implementation of regular, documented recovery testing conducted within isolated, production-like environments. This practice moves beyond theoretical planning to tangible validation of an organization's ability to recover.
These tests are not merely about checking if backups are restorable; they are comprehensive exercises designed to simulate a real-world ransomware incident. By replicating the conditions of an attack in a controlled setting, organizations can identify bottlenecks, validate recovery procedures, and quantify the time required for a full restoration. Crucially, the results of these tests must be meticulously documented, providing concrete data that can inform both executive decision-making and CISO strategy.
Network segmentation is highlighted as another critical component of this strategy. By dividing networks into smaller, isolated segments, organizations can limit the lateral movement of ransomware and contain the impact of an attack. This architectural approach is not only a defensive measure but also a facilitator of recovery, allowing specific segments to be restored independently without compromising the entire network.
The combination of rigorous, documented testing and effective network segmentation provides a tangible basis for aligning the CEO's concerns about business impact with the CISO's need for secure and reliable system restoration. When recovery times and success rates are backed by empirical data from tested plans, the conversation shifts from speculative fear to informed confidence.
Ultimately, the article argues that organizations cannot afford to wait for a ransomware attack to discover the efficacy of their recovery capabilities. Proactive, consistent, and documented testing, integrated with sound network architecture, is the most effective way to ensure that when the inevitable ransom note appears, the organization is prepared to respond decisively, securely, and with a unified vision for recovery.