
'Ransom Busters' Poses as Incident Response Service to Divert Payments
A ransomware affiliate, operating under the moniker 'Ransom Busters,' is deceptively offering incident response services to victims, aiming to redirect ransom payments for their own illicit gain.
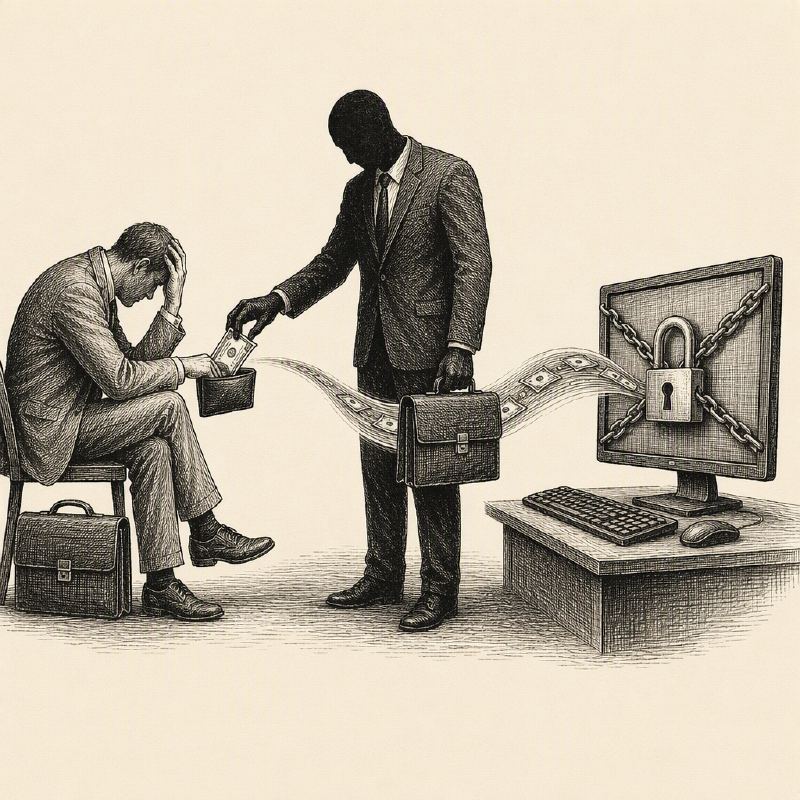
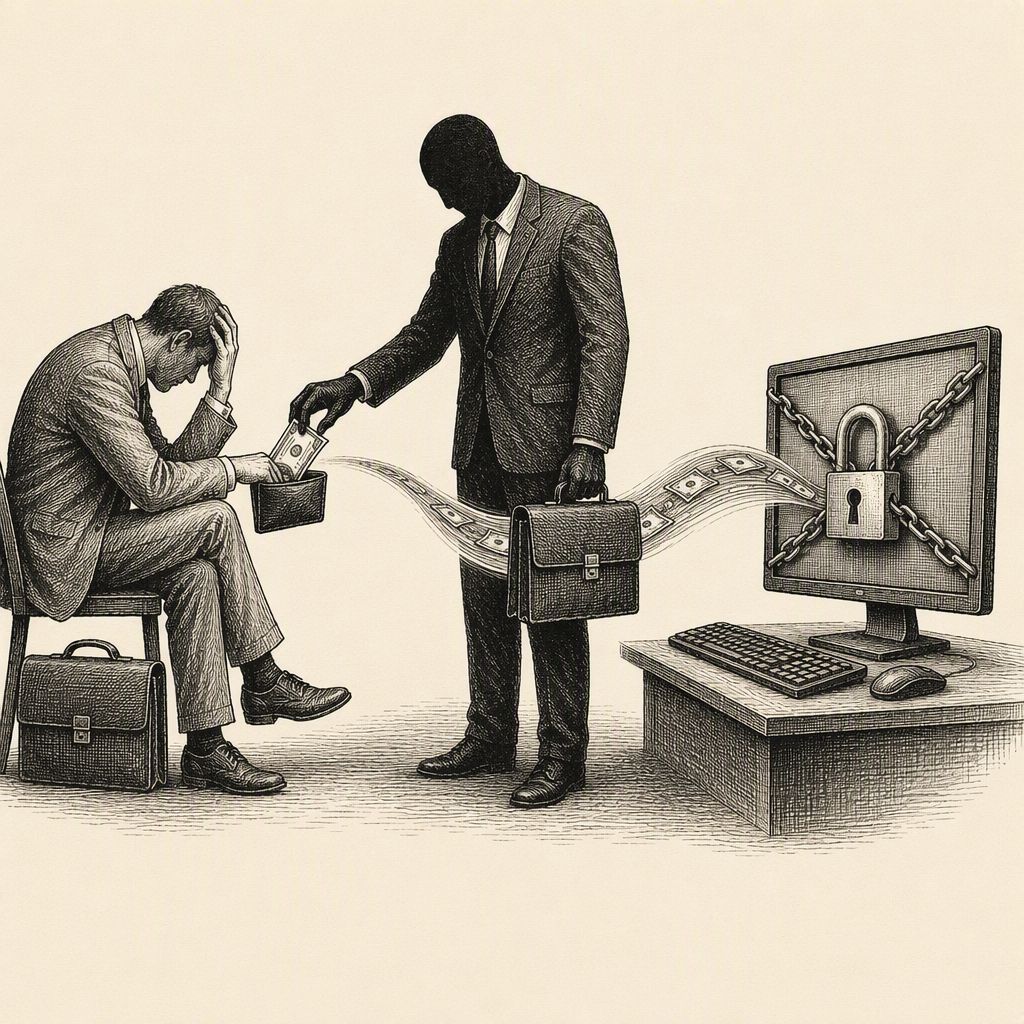
A new tactic has emerged in the ransomware landscape, with an affiliate group dubbed 'Ransom Busters' posing as a legitimate incident-response service. This deceptive operation targets organizations already reeling from a ransomware attack, offering assistance in data recovery while secretly intending to intercept and divert ransom payments.
The group's modus operandi involves reaching out to victims who have recently fallen victim to ransomware. They present themselves as a professional service capable of helping to restore encrypted data, preying on the desperation and urgency that victims experience during such crises. By offering a seemingly helpful solution, 'Ransom Busters' aims to gain the trust of the compromised organization.
However, their true objective is to manipulate the situation to their financial advantage. Instead of facilitating a genuine recovery process, the group intends to reroute any ransom payments made by the victim directly to themselves. This effectively turns the victim's attempt to resolve the crisis into a secondary extortion scheme, where they pay a ransom only to have it pocketed by the very 'rescuers' they hired.
This strategy highlights a disturbing evolution in ransomware operations, where threat actors are not only focused on encrypting data but also on exploiting the aftermath of an attack through social engineering and deception. The 'Ransom Busters' operation underscores the increasing sophistication and multi-faceted nature of modern ransomware campaigns.
While specific technical details about the group's infrastructure or the exact methods used to intercept payments are not yet widely known, the core of their operation relies on exploiting the trust of vulnerable victims. This tactic is particularly insidious as it targets organizations at their weakest point, making them susceptible to false promises of aid.
The emergence of 'Ransom Busters' serves as a critical warning to organizations facing ransomware incidents. It emphasizes the importance of verifying the legitimacy of any third-party services offering assistance during a cyberattack and the potential dangers of engaging with unknown entities, even when they appear to offer a solution.
Security researchers are closely monitoring this development, urging potential victims to exercise extreme caution and to rely on established and reputable cybersecurity firms for incident response. The group's deceptive approach adds another layer of complexity to an already challenging threat environment, where the lines between attacker and 'rescuer' are blurred.
This new report provides further technical details on the 'Ransom Busters' operation, including specific tools used such as SoftPerfect Network Scanner and s5cmd for data exfiltration, and the consistent use of a remote monitoring and management (RMM) tool. Additionally, the analysis highlights commonalities in backdoor account creation and attacker-controlled hostnames across different incidents, suggesting a single operator is behind the persona. The report also notes the group's puzzling justification for charging victims, claiming that acting without compensation would jeopardize their access to ransomware infrastructure.
This new report from Cyber Security News provides further technical details on the 'Ransom Busters' operation, including specific tools used for network discovery (SoftPerfect Network Scanner), data exfiltration to AWS (s5cmd), and remote management (Remotely). It also highlights shared indicators of compromise such as a backdoor password ('Numlock!123') and an attacker-controlled hostname ('DESKTOP-BBETH6KS'), strengthening the link to ransomware affiliates associated with DragonForce, Settra, and Anubis.
This new report from The Register Security provides further technical details on the 'Ransom Busters' operation, identifying specific tools like SoftPerfect Network Scanner and s5cmd used in their attacks. It also highlights the reuse of a common backdoor password ('Numlock!123') and hostname ('DESKTOP-BBETH6K') across multiple ransomware-as-a-service (RaaS) campaigns, strongly suggesting a single affiliate is responsible for this deceptive tactic across various criminal enterprises.