
Qubole Supply Chain Attack Exposes Customer Data via Compromised IAM Credentials
Attackers breached Qubole's cloud environment, stealing sensitive customer data including files, secrets, and credentials by exploiting compromised IAM permissions.
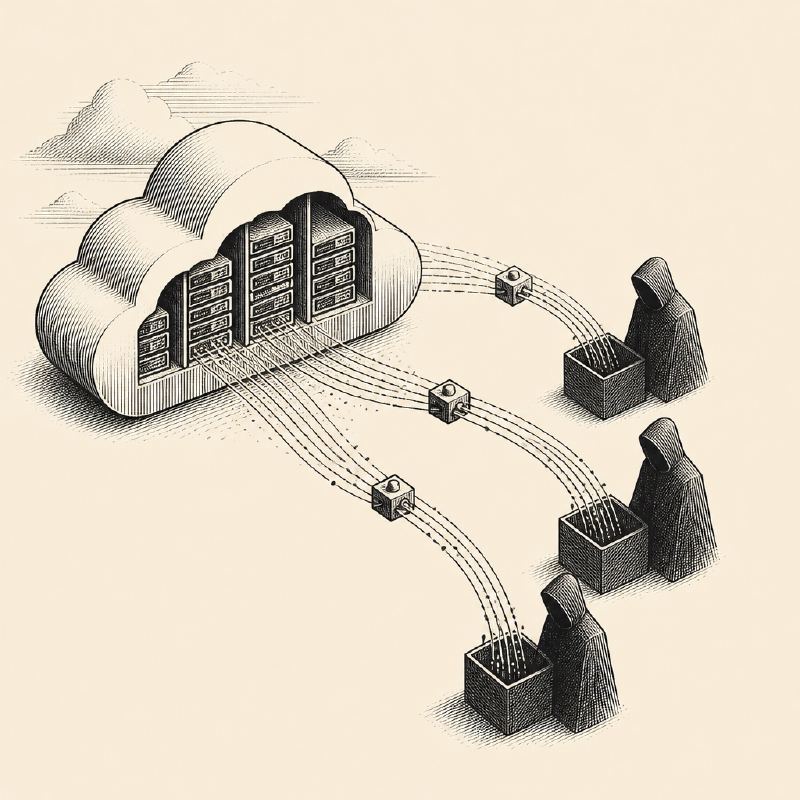
A significant supply chain attack has impacted over a dozen organizations after threat actors compromised the cloud environment of Qubole, a data analytics platform. The attackers successfully gained access to sensitive customer data by exploiting stolen Identity and Access Management (IAM) credentials.
The breach allowed the adversaries to exfiltrate a wide range of critical information. This included customer files, proprietary secrets, cryptographic keys, environment variables, and other sensitive credentials belonging to the affected organizations. The compromised data could potentially be used for further attacks, espionage, or financial fraud.
This incident underscores the inherent risks associated with cloud-based data platforms and the critical importance of securing IAM credentials. Qubole, as a provider of data analytics services, holds access to vast amounts of sensitive information for its clients. A compromise of its environment therefore poses a direct threat to those clients.
The attackers leveraged the compromised IAM credentials to navigate Qubole's cloud infrastructure and access the data repositories of its customers. The exact method of initial compromise for Qubole's environment has not been detailed, but the subsequent data theft was facilitated by the elevated privileges granted through the stolen credentials.
While the full scope of the impact is still being assessed, the exposure of files, secrets, and keys presents a substantial risk to the affected organizations. This could lead to further downstream security incidents, including unauthorized access to other systems, data breaches, and potential financial losses.
Supply chain attacks, where a vulnerability in a trusted third-party vendor is exploited to target its customers, continue to be a prevalent threat vector. This incident serves as a stark reminder for organizations to rigorously vet the security practices of their vendors and to implement robust monitoring and access control measures for any third-party services that handle sensitive data.
Organizations utilizing Qubole or similar data analytics platforms are advised to review their security configurations, rotate any potentially compromised credentials, and enhance their monitoring for suspicious activity. The incident highlights the need for continuous vigilance and proactive security measures in the interconnected digital landscape.