
PropellerAds Details Sophisticated Malware Delivery Tactics
A new analysis from PropellerAds reveals how modern malware campaigns employ multi-stage, visitor-qualifying delivery systems to bypass security researchers and target specific devices.
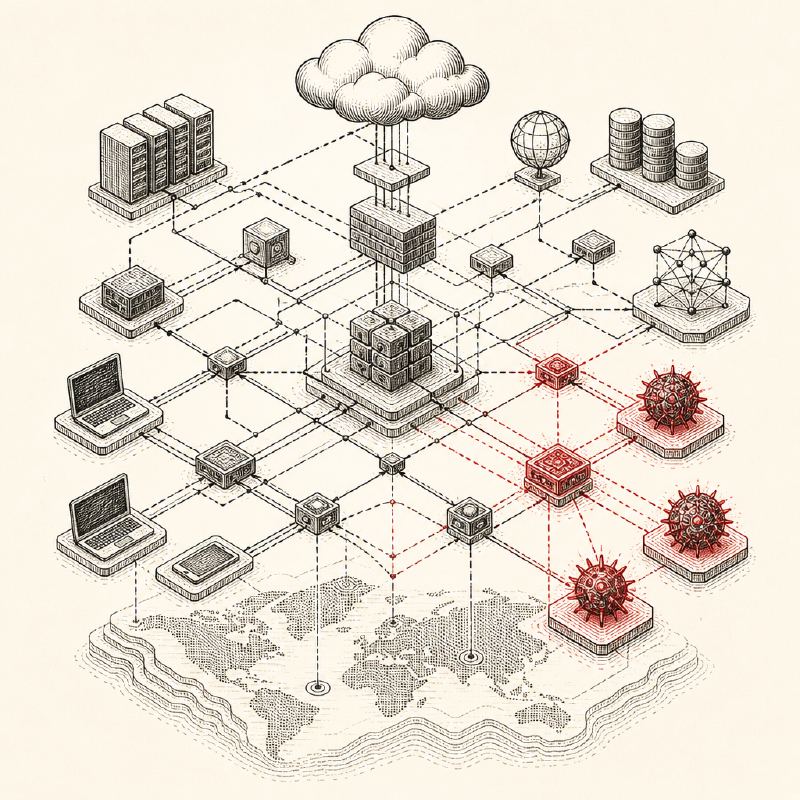
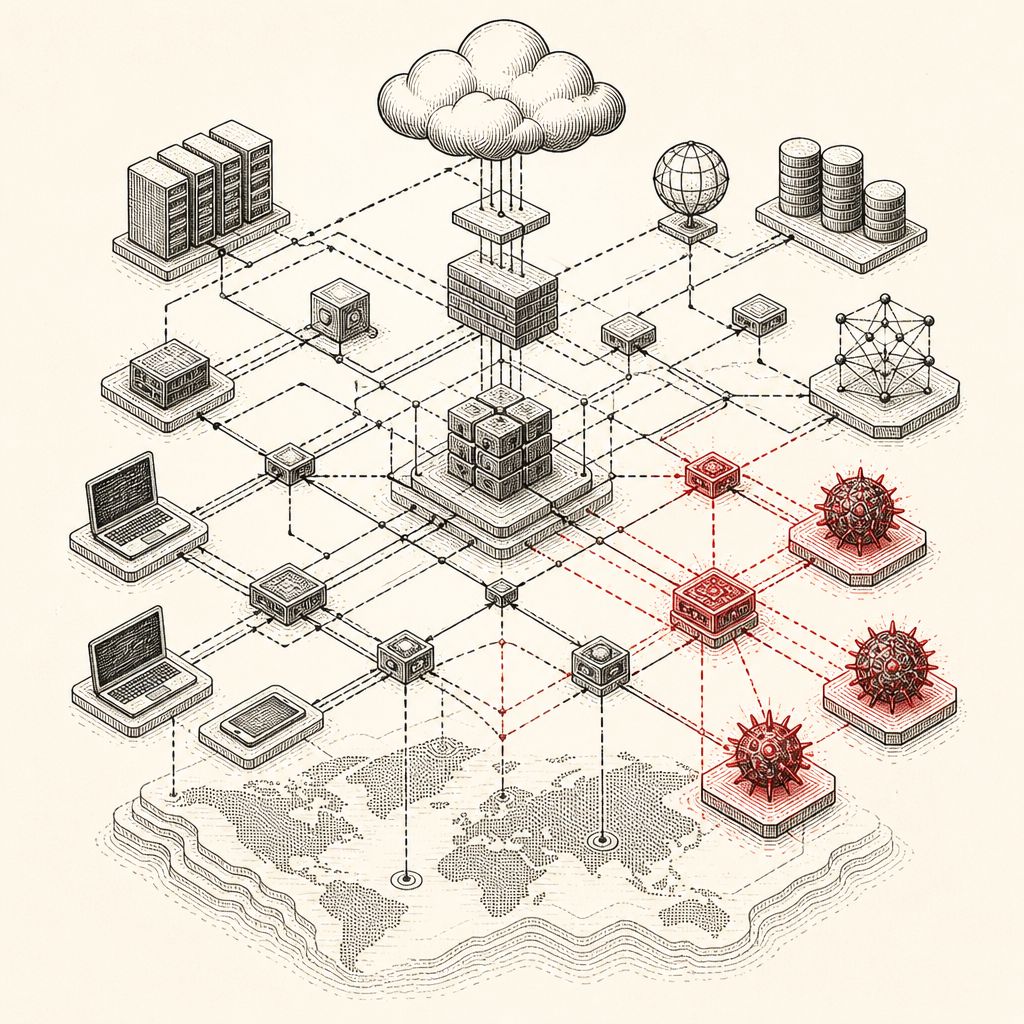
Modern malware delivery has evolved into a complex, multi-stage operation that begins long before the malicious payload is ever deployed. Attackers are increasingly using "qualify-first" approaches, exemplified by the Coruna iOS exploit kit, which meticulously vets visitors before delivering an exploit. This strategy involves JavaScript fingerprinting to identify device models and operating system versions, ensuring that only specific targets receive the exploit while researchers, scanners, and private browsing sessions are actively blocked.
The Coruna exploit kit, disclosed by Google Threat Intelligence Group, showcased this selectivity by targeting specific iOS versions, demonstrating a significant shift from earlier, less discerning malware distribution methods. For defenders, the focus often lies on the payload itself, but for attackers, the payload represents the culmination of an intricate assembly line. This process includes acquiring traffic through various means, routing it through redirectors and traffic distribution systems (TDS), leveraging trusted infrastructure like CDNs to blend in, and finally, qualifying the visitor before persuasion tactics are employed.
PropellerAds, through its traffic-quality and anti-fraud system ADEX, gains visibility into this upstream layer of malware delivery. Their analysis highlights that a malware campaign should be viewed as a sophisticated delivery system comprising five key components: acquisition, routing, trusted infrastructure, visitor qualification, and persuasion. This layered approach allows attackers to operate with a high degree of stealth and precision.
Long redirect chains have been a known tactic for years, but the current trend emphasizes selectivity. The Coruna kit's ability to crash browsers or deliver patched exploits to researchers underscores the importance of this refined targeting. By ensuring that only specific versions of exploits are delivered to compatible devices, attackers minimize the risk of detection and patching by security researchers.
Ad platforms like PropellerAds possess unique insights into these operations. They can observe signals at submission, such as account history and domain reuse; during moderation, by analyzing the full redirect path and landing page scripts; and after launch, by monitoring real traffic and abuse reports. This visibility allows them to identify suspicious patterns, such as pages that load hidden iframes to check OS versions, even before an exploit is delivered.
ADEX's investigation uncovered approximately 50 advertiser accounts linked to campaigns employing similar "qualify-first" delivery mechanisms, even though their landing pages varied widely in theme and vertical. These campaigns shared an identical underlying delivery chain: a hidden iframe checked the OS version, an orchestrator filtered bots, and a version-specific script was served. This consistent delivery behavior, despite disparate appearances, pointed to a single operator.
Data from ADEX's Trust & Safety review for January to September 2026 indicates a significant shift in malware delivery tactics. Cloaking remains a primary reason for campaign suspensions, but device-specific scripts and messenger phishing have emerged as major concerns. The analysis shows that the infrastructure for these sophisticated delivery systems can take weeks to build, while landing pages can be refreshed daily, allowing operators to maintain a consistent delivery method across various deceptive fronts.
This evolution in malware delivery underscores the need for advanced detection and mitigation strategies. By analyzing traffic quality, redirect paths, and visitor qualification techniques, security professionals and ad platforms can gain crucial insights into emerging threats and proactively disrupt malicious campaigns before they reach their intended targets.