
Phishing Detection's Visibility Gap Highlighted by Evolving Attack Chains
Attackers are increasingly using multi-stage redirects and dynamic content to obscure phishing attacks, creating a visibility gap that traditional URL analysis struggles to bridge.
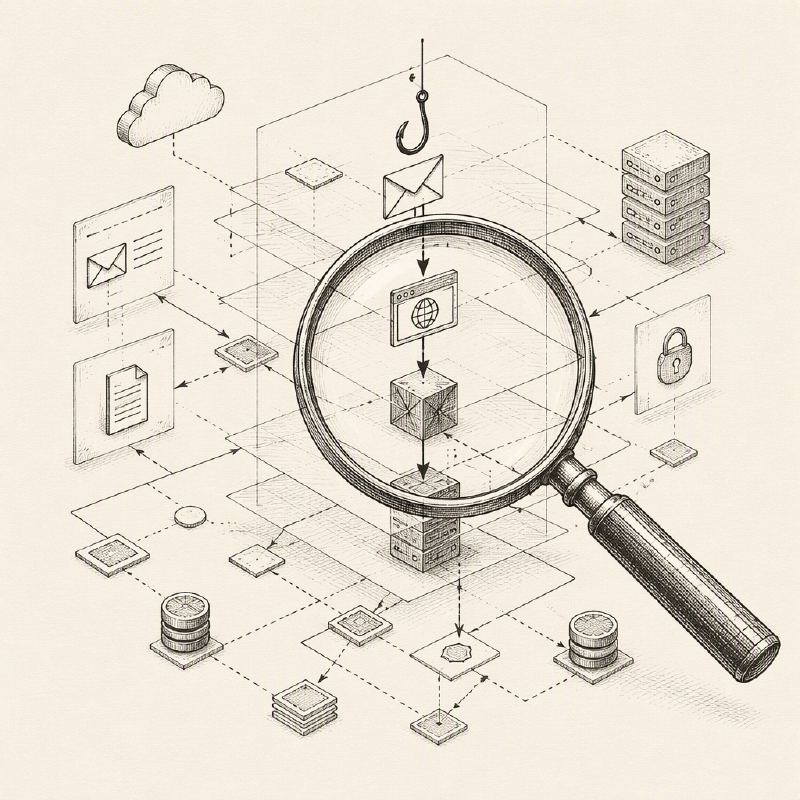
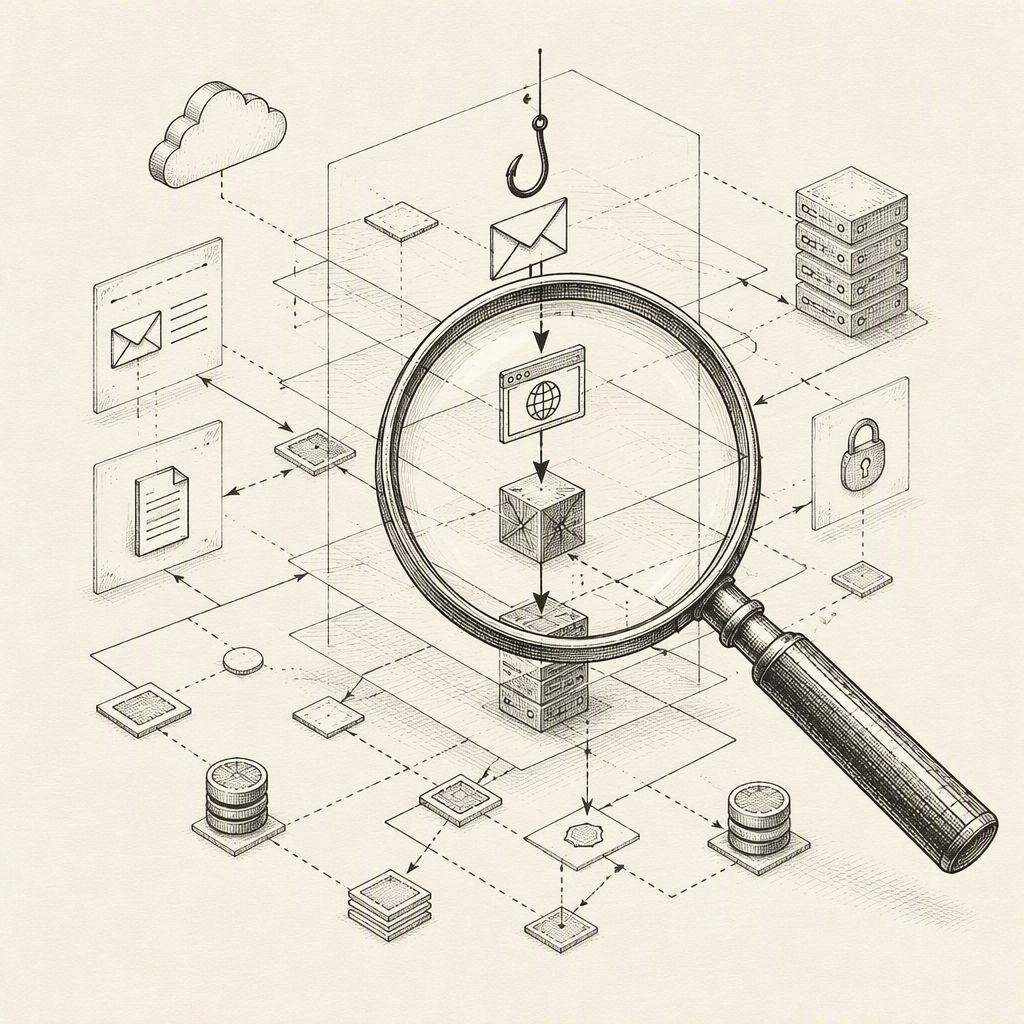
The initial stages of phishing detection often leave security analysts with a critical question: is a suspicious URL truly benign, or does it hide a more insidious threat? Modern phishing campaigns are evolving beyond simple, static links, employing sophisticated techniques that reveal their malicious intent only after a user clicks. This dynamic behavior creates a significant 'visibility gap' for security operations centers (SOCs) and managed security service providers (MSSPs), as their tools may only analyze the initial URL without uncovering the full attack chain.
Traditional static analysis, which examines artifacts like URLs, domains, or files without executing them, can provide initial indicators. However, this method often falls short when an attack relies on post-click actions. For instance, a seemingly harmless link might lead to a page that executes JavaScript, contacts a secondary server, follows a series of redirects, and finally generates a convincing login form designed to harvest credentials. If a security solution only inspects the initial landing page, the ultimate phishing destination remains hidden, leaving analysts with incomplete information.
Sandboxing technology offers a crucial solution to this visibility problem. By providing an isolated, safe environment, sandboxes allow suspicious content to be executed and meticulously monitored. This enables security professionals to observe the complete sequence of actions triggered by a link or file, thereby building a comprehensive understanding of the attack. Interactive sandboxes, in particular, can accelerate threat investigations by quickly detonating samples and allowing analysts to explore the observed behavior in detail.
Attackers employ various strategies to obfuscate their phishing operations. These include chaining multiple domains, using JavaScript to dynamically generate content, and checking browser characteristics or other environmental factors to tailor the phishing page. Some campaigns even incorporate CAPTCHAs or require specific user interactions, further complicating automated analysis. These techniques serve to create a buffer between the malicious infrastructure and the potential victim, making it harder for defenders to connect the dots.
Reputation services, while useful, are not always sufficient. A domain might have a clean reputation, but this doesn't guarantee its current activity. Attackers often leverage legitimate services and infrastructure, making simple reputation-based decisions unreliable. Consequently, a suspicious link may necessitate behavioral investigation even if its individual components appear innocuous.
The evolving nature of phishing is underscored by recent industry reports. For example, ANY.RUN's H1 2026 Cyber Risk Report highlights trends such as the rise of custom fake CAPTCHAs, browser fingerprinting, and the abuse of calendar invites. The report also notes a significant increase in attacks utilizing trusted infrastructure, like Adobe services, and remote management tools, further blurring the lines between legitimate and malicious activity.
For SOC and MSSP teams, staying abreast of these evolving techniques is paramount. Understanding the latest threats, risks, and recommended defenses helps in evaluating current detection coverage and refining investigation workflows. The practical takeaway is that robust threat intelligence, combined with tools that offer deep visibility into dynamic behaviors, is essential for effectively combating modern phishing campaigns.
In conclusion, the 'visibility gap' in phishing detection is a direct consequence of attackers' increasing reliance on multi-stage, dynamic attack chains. Solutions that incorporate advanced sandboxing and behavioral analysis are critical for SOCs and MSSPs to gain the necessary insight to identify and investigate these sophisticated threats effectively.