
Outerlimit Secures $16M for Zero Trust Security Layer for Autonomous AI Agents
Outerlimit has raised $16 million to build a decentralized zero trust security layer for autonomous AI agents, aiming to mitigate risks associated with their tool manipulation and workflow execution.
Outerlimit has emerged from stealth mode, announcing a significant $16 million in pre-seed funding to develop a novel decentralized security and authorization layer specifically designed for autonomous AI agents. The funding round, which closed on September 22, 2026, was led by prominent investors including AlbionVC, Evolution Equity Partners, and Crane Venture Partners, marking it as one of the largest pre-seed raises in the cybersecurity sector.
The startup, with operations in London and New York, is addressing a critical gap in enterprise security. Autonomous AI agents possess the capability to interact with various tools, access sensitive data, utilize APIs, and execute complex workflows. This autonomy, however, introduces substantial risks if an agent is compromised, misconfigured, or exhibits unexpected behavior after processing untrusted information. Traditional identity and access management (IAM) solutions, while capable of authenticating agents, often fall short in constraining the specific actions an agent can take at the point of execution.
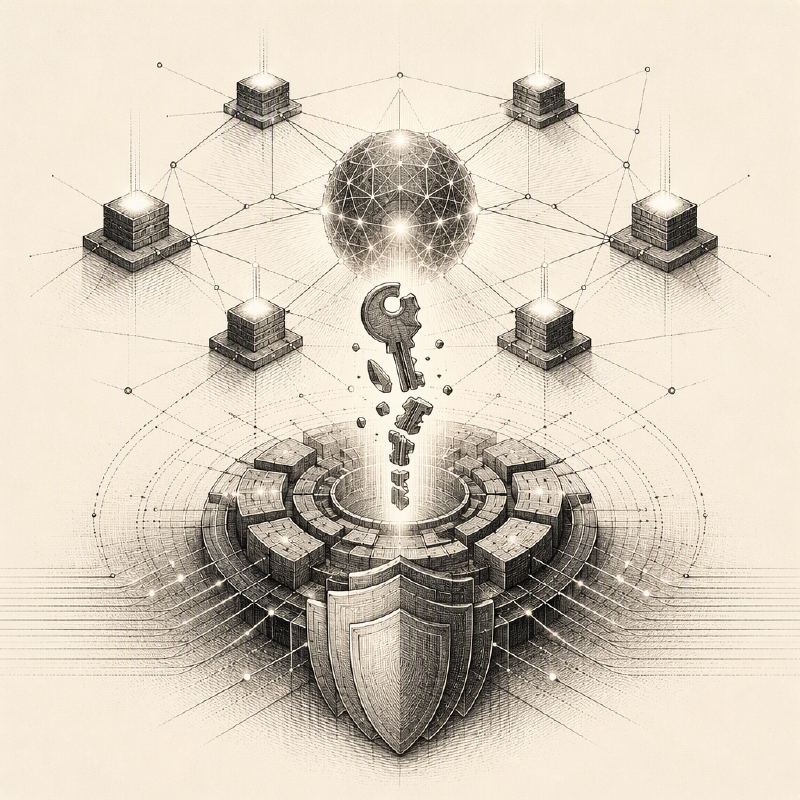
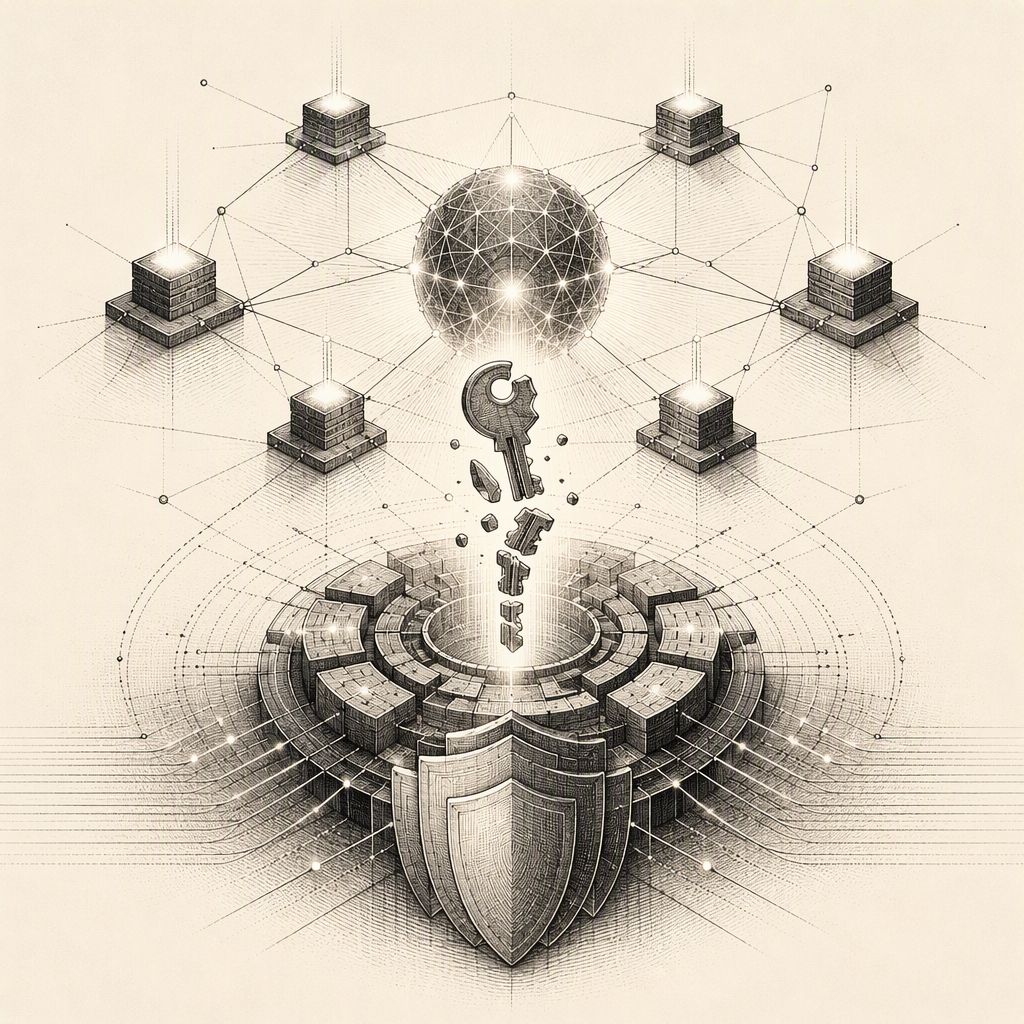
Outerlimit's proposed solution extends the principles of Zero Trust to this "agent action layer." Instead of consolidating credentials, cryptographic keys, or secrets in a single location, the platform fragments these sensitive elements across the agent ecosystem. These fragments are then reassembled only when an agent attempts to invoke a tool, and only after its identity, adherence to policy, and the execution context have been rigorously verified. This mechanism aims to provide deterministic authorization, ensuring that any action deviating from established policies is denied before the underlying tool is executed, even if the AI agent's behavior has become misaligned.
"Agents can change their behavior based on what they read, or how they interact with other agents, while acting at machine speed," stated co-founder and CTO Dr. Peter Vincent. He emphasized the necessity of binding identity, authorization, and action into a single, verifiable operation at the moment of execution. This approach seeks to provide a robust security posture that keeps pace with the rapid decision-making capabilities of AI agents.
The company outlines a three-stage adoption process for its platform. The initial stage, "Discovery," focuses on identifying all relevant components within the agent ecosystem, including agents, tools, Model Context Protocol servers, and any unsanctioned "shadow AI." "Observation" follows, providing visibility into agent activities while maintaining integrity across complex, multi-hop agent interactions. The final stage, "Enforcement," implements granular policy controls on every agent action. This phased approach is designed to help organizations gain a comprehensive inventory of their AI deployments before introducing potentially disruptive controls.
CEO Tony Pepper highlighted that outright blocking of agentic AI adoption could inadvertently push teams towards unapproved tools operating outside of enterprise oversight. However, Outerlimit's most significant claims—including provable observation, zero credential exposure, and deterministic control—currently remain vendor assertions. The company's launch announcement did not include independent test results, performance benchmarks, or details of early customer deployments, leaving room for further validation.
The startup was founded by Pepper and Neil Larkins, who previously led Egress Software, an email security vendor acquired by KnowBe4 in 2024, alongside Dr. Vincent, a neuroscientist. For security teams, Outerlimit's emergence signifies a critical evolution in AI agent security: monitoring model outputs alone is insufficient when software agents can directly alter systems. Security professionals require controls at the boundary where actions are executed, allowing for evaluation, logging, and blocking. While Outerlimit's substantial funding provides the resources to pursue this architectural vision, building enterprise confidence will hinge on transparent technical validation, broad integration support, and demonstrable reliability of its enforcement mechanisms at machine speed.