
Optimizely Platform Compromise Leads to Widespread Malware Distribution
A vulnerability in Optimizely's web experimentation platform was exploited to inject malicious JavaScript, impacting 178 organizations including BBC, CNN, and Zoom.
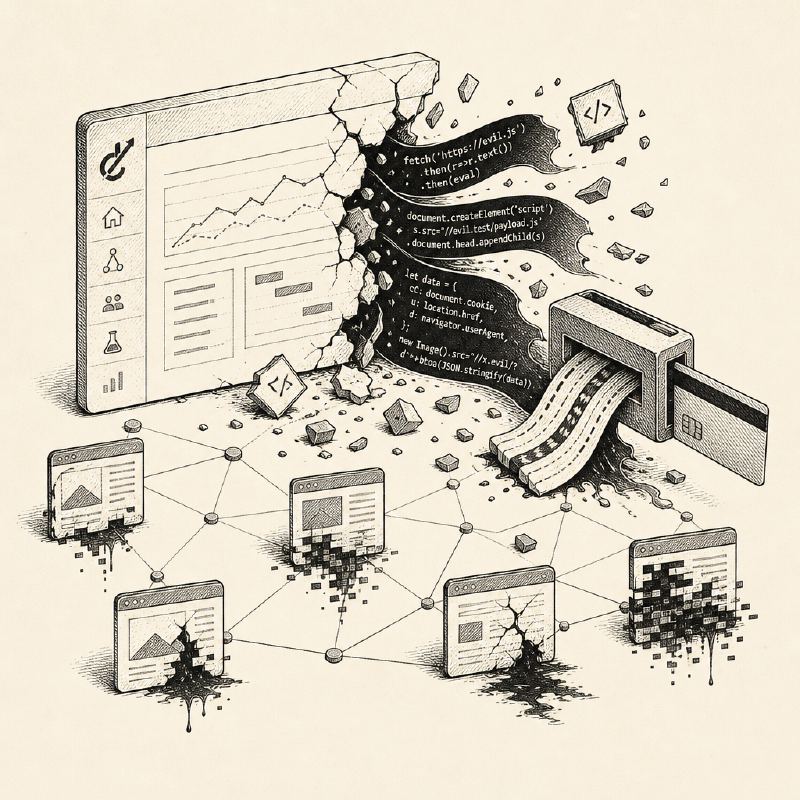
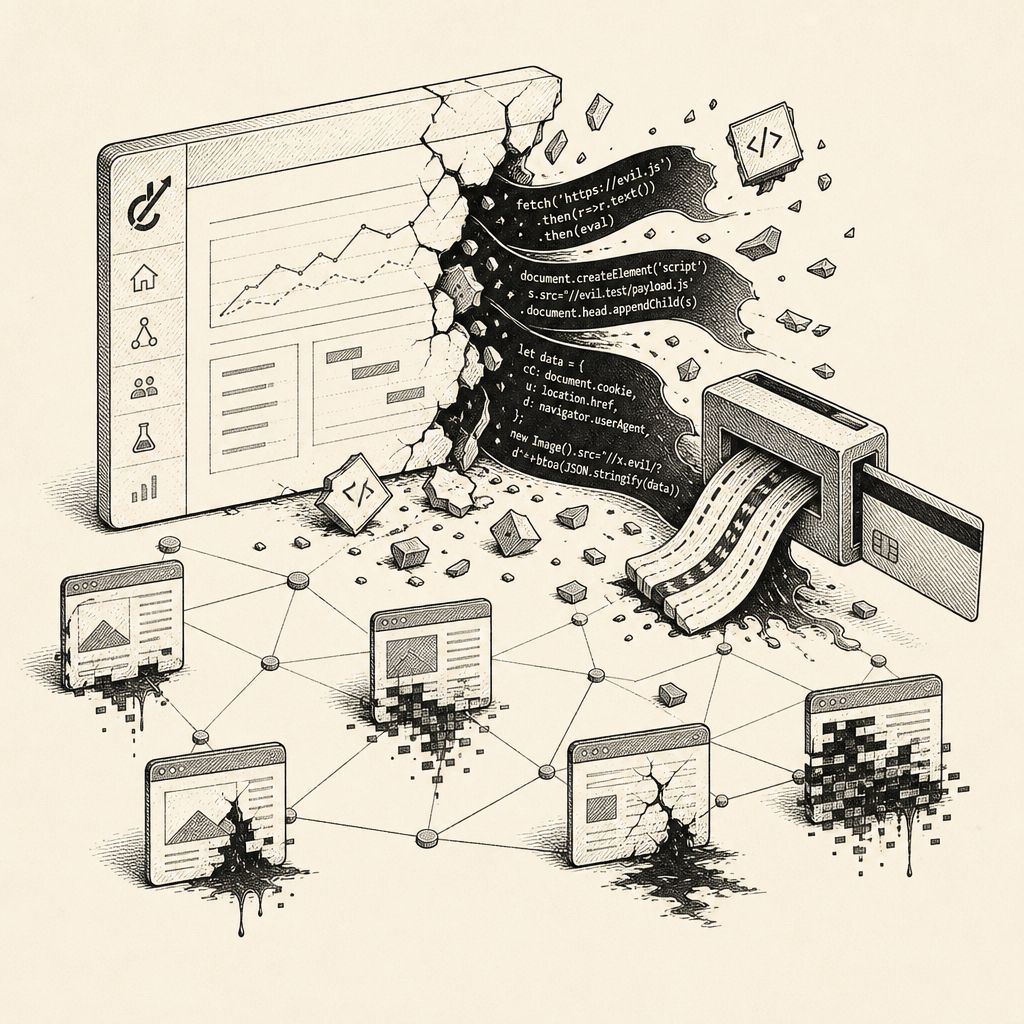
A significant security incident has impacted at least 178 organizations after attackers exploited a vulnerability within Optimizely's web experimentation platform. The attackers leveraged this flaw to inject malicious JavaScript code onto the websites of Optimizely's customers, leading to the distribution of harmful content to a wide audience.
Among the high-profile organizations confirmed to be affected are major media outlets like the BBC and CNN, as well as technology giant Zoom. The compromise highlights the risks associated with supply chain attacks, where a vulnerability in a trusted third-party service can have far-reaching consequences for its clients.
The injected JavaScript was reportedly used to serve various malicious payloads. Initial reports indicate that the attackers deployed card skimmers, designed to steal payment card information from unsuspecting visitors. Additionally, exploit kits targeting iOS devices were also distributed, potentially compromising the security of Apple users.
Optimizely, a platform used for A/B testing and website personalization, acknowledged the incident and confirmed that an attacker exploited a vulnerability in its system. The company stated it has taken steps to address the issue and is working with affected customers to mitigate the impact. The full extent of the data compromised and the specific methods used to exploit the vulnerability are still under investigation.
This incident underscores the critical importance of robust security measures for third-party platforms that integrate with numerous client websites. The widespread nature of the attack, affecting a large number of diverse organizations, emphasizes the interconnectedness of the digital ecosystem and the potential for a single point of failure to cause cascading security breaches.
Security researchers are analyzing the injected code to understand the full scope of the attack and identify any additional malicious activities. The incident serves as a stark reminder for businesses to rigorously vet the security practices of their vendors and to implement comprehensive monitoring and incident response plans to detect and address such supply chain compromises swiftly.
While Optimizely has stated that the vulnerability has been remediated, the fallout from this attack is likely to continue as affected organizations assess the damage and implement enhanced security protocols. The incident also raises questions about the security of web experimentation and personalization tools, which often handle sensitive user data and interact directly with customer-facing websites.