
New Unicode Characters Enable Sophisticated Phishing Domains
Researchers have identified new Unicode characters that allow attackers to craft highly convincing lookalike domains, bypassing browser defenses and tricking users into visiting malicious sites.
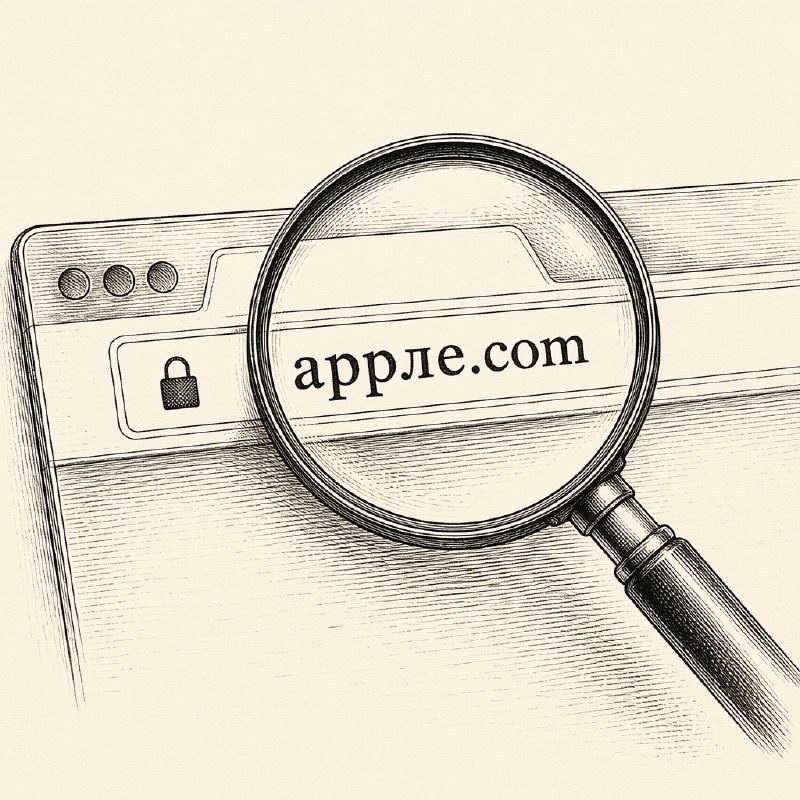
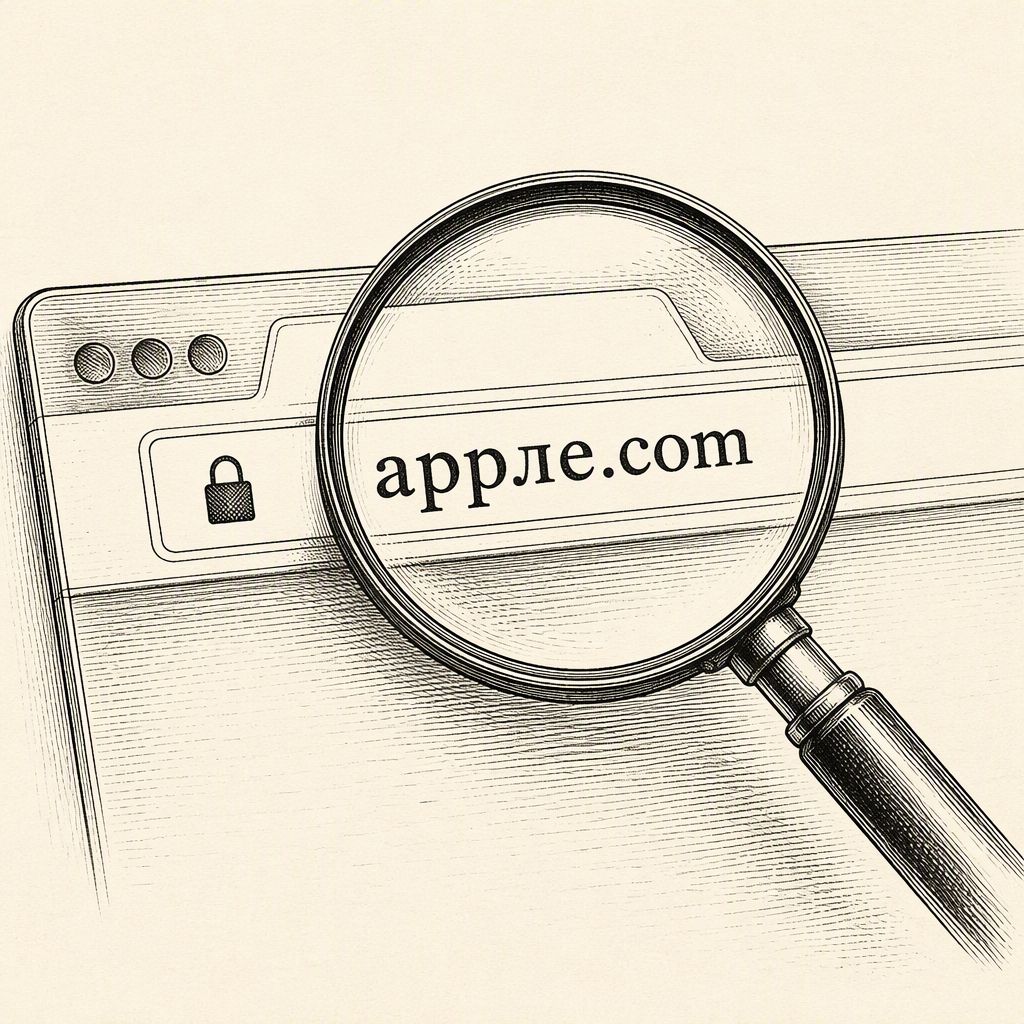
Security researchers have discovered a novel method for creating deceptive domain names that closely mimic legitimate brands, while still appearing as readable Unicode text within Chromium-based browsers. This technique poses a significant phishing risk, as it can fool users into believing they are on a trusted website without triggering typical browser warnings.
The research, conducted by Ian Muscat and Leanne Briffa of Have I Been Squatted, tested internationalized domain names (IDNs) against Chromium's domain display rules. Their proof-of-concept included a domain, аррӏө[.]com, which is a Cyrillic rendition of apple[.]com. In testing, Chrome version 154 displayed this domain in its Unicode form rather than its Punycode equivalent, xn--80a6aa68c8d[.]com, making it appear legitimate to the end-user. These domains were registered for controlled testing purposes and not for active phishing campaigns.
The Domain Name System (DNS) initially supported only ASCII characters. The introduction of IDNs later allowed for characters from various languages, which are then converted into ASCII-compatible Punycode for DNS resolution, typically prefixed with "xn--." While this enables global internet access, it also introduces security risks due to the visual similarity between characters from different scripts, a technique known as a homograph or homoglyph attack. Cyber Security News has previously reported on similar homoglyph attacks and other phishing tactics exploiting character similarities.
Chromium employs several defenses to thwart these attacks, including displaying suspicious IDNs in Punycode. Its detection mechanisms scrutinize mixed scripts, unsafe symbols, entire script confusions, and skeleton matching, drawing upon principles from Unicode Technical Standard 39. A notable defense is the whole-script confusable check, implemented after a well-known 2017 аррӏе[.]com test case that used only Cyrillic characters to mimic "apple." Chromium now detects such attempts and displays the Punycode version.
However, the recent research identified a loophole in this defense. The whole-script confusable check is only effective if *every* character in a Cyrillic label is present on Chromium's lookalike list. The Cyrillic letter 'ө', used in languages like Kazakh and Mongolian, is permitted but not on this list. By replacing a character on the list with 'ө', the entire check can be bypassed, even though the resulting domain can still visually resemble the intended target, such as 'apple.com'.
A secondary vulnerability was found in Chromium's skeleton matching process. This feature typically removes accents and diacritics before comparing domain names. However, marks from characters with hooks or strokes can persist. Consequently, 'oƙta[.]com' does not reduce to the same skeleton as 'okta[.]com' because the bar from 'ө' prevents 'аррӏө[.]com' from matching 'apple[.]com' correctly.
The researchers registered 20 proof-of-concept domains mimicking brands like Apple, OpenAI, Skype, and others. Their tests revealed that Chromium's navigation warning system failed to flag 'аррӏө[.]com' because its skeleton was deemed too dissimilar to 'apple[.]com' for the warning to trigger. The risk extends to email, where tests showed Gmail Web displaying these lookalike domains in Unicode, while Outlook Web showed them as encoded A-labels, potentially misleading recipients.
Organizations are advised to monitor newly registered "xn--" domains that resemble their brands, review certificate transparency logs, and implement impersonation protection in their mail gateways. Users should exercise caution with links in unexpected messages, favor bookmarks or direct typing for access, and leverage password managers or passkeys, which are designed to match exact domain names and resist spoofing attempts. While browser updates are crucial, this research underscores that relying solely on the address bar for verification is no longer sufficient.