
New Abe Office Malware Bypasses Chrome Encryption to Steal Browser Data
A new remote-access trojan, dubbed Abe Office, is exploiting Chrome's App-Bound Encryption to steal user passwords and cookies by injecting code into browser processes.
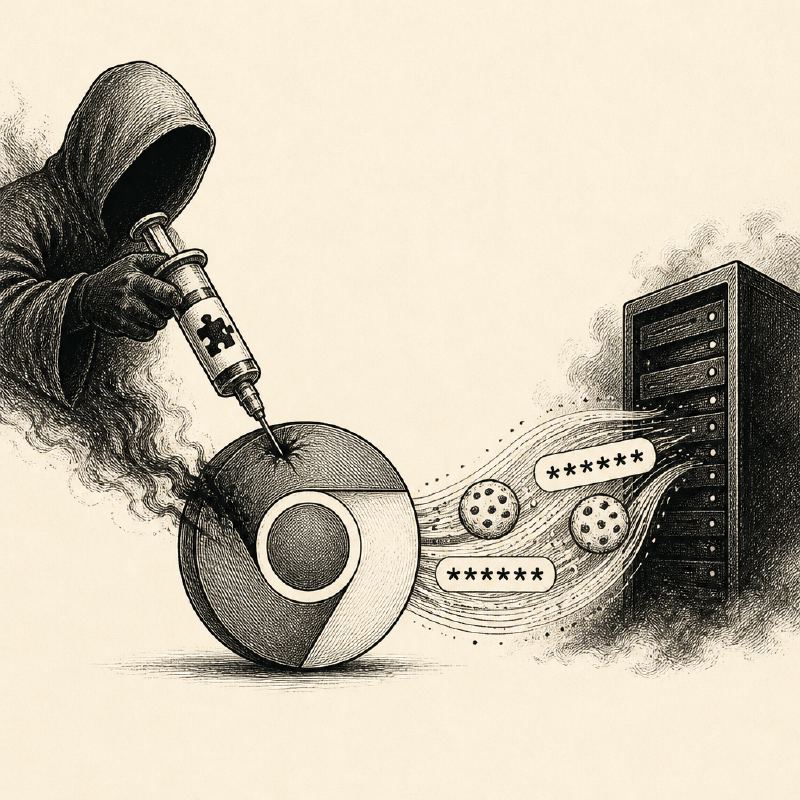
A novel remote-access trojan (RAT) named Abe Office has emerged, specifically targeting Google Chrome's App-Bound Encryption feature to exfiltrate sensitive user data, including saved passwords and session cookies. Researchers at Rogue Authority discovered the malware, which masquerades as a legitimate "Abe Office workstation helper" tool. Despite its deceptive appearance and the use of a valid code-signing certificate issued by SSL.com under the name Kimberley Hankinson, the malware's security protections are notably weak, including a default password "AbeOffice-ChangeMe" used for decrypting its components and network traffic.
The malware's initial execution involves copying itself to the user's profile directory, removing Windows' Mark of the Web tag to evade detection, and establishing persistence through a registry Run key and a scheduled task. It also attempts to create a firewall rule to allow its network communications. Abe Office then drops three encrypted add-ons: the main RAT component, a hidden desktop module, and a browser helper DLL. Crucially, the malware retrieves its decryption keys from a command-and-control (C2) server, but researchers found these keys could be easily derived offline using the default password.
Once decrypted, the hidden desktop module creates an invisible Windows desktop and launches instances of Chrome and Edge within it. It achieves this by copying the victim's existing browser profiles, allowing the attacker to access already logged-in sessions on banking, email, and shopping websites without needing credentials. This technique is increasingly seen in modern infostealers, aiming to bypass multi-factor authentication and "new device" security checks by operating from a seemingly legitimate, pre-authenticated environment.
The core of Abe Office's novel attack lies in its method for bypassing Chrome's App-Bound Encryption, a security feature introduced in July 2024 designed to protect sensitive data by requiring specific applications to have system-level privileges or employ code injection to access decryption keys. Abe Office opts for the latter, injecting its helper DLL into an off-screen browser instance. This injected code then tricks the browser's own elevation service into decrypting the requested data, as the request originates from a legitimate browser process.
While the malware's C2 communication is protected by an AES key derived from the same weak password, allowing for potential decryption of captured traffic, the delivery method for Abe Office remains unknown. However, the presence of a valid code-signing certificate suggests this may be a more recent and sophisticated iteration of the malware family, as previous samples lacked such assurances. The certificate has been reported to the Certificate Authority and flagged.
Security researchers warn that any user who may have executed this malware should consider their browser sessions compromised. Immediate actions recommended include signing out of all online accounts, changing passwords for critical services starting with email, enabling two-factor authentication, and performing a full system clean or reinstallation of the affected PC. Defenders are advised to monitor for the presence of Abe Office-specific directories, registry keys, and network traffic to known C2 servers at 2.26.230.54 and 87.199.195.141 on port 9090.
Further defensive measures include flagging browsers launched with specific off-screen window positions or those utilizing local remote debugging. Additionally, non-browser processes attempting to access sensitive browser data files like Login Data, Cookies, and Local State should be treated with suspicion. The report also highlights that logins originating from the victim's own machine should not be automatically trusted if unusual activity is detected, underscoring the evolving tactics of information-stealing malware.