
MFA Alone Cannot Stop OAuth Consent Abuse, Experts Warn
Multi-factor authentication is insufficient to prevent OAuth consent abuse, necessitating robust governance, monitoring, and rapid revocation processes.
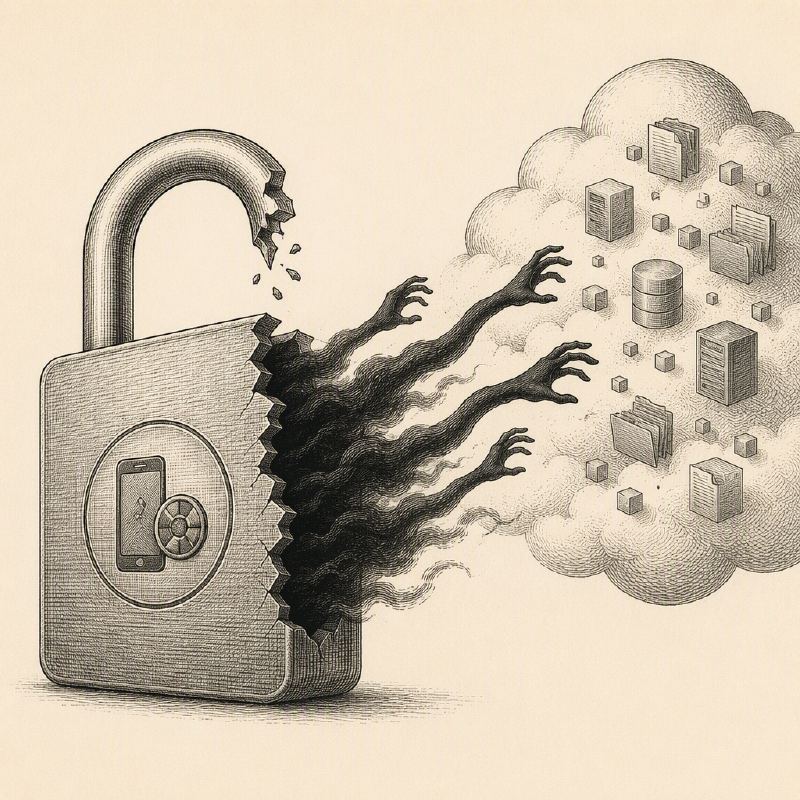
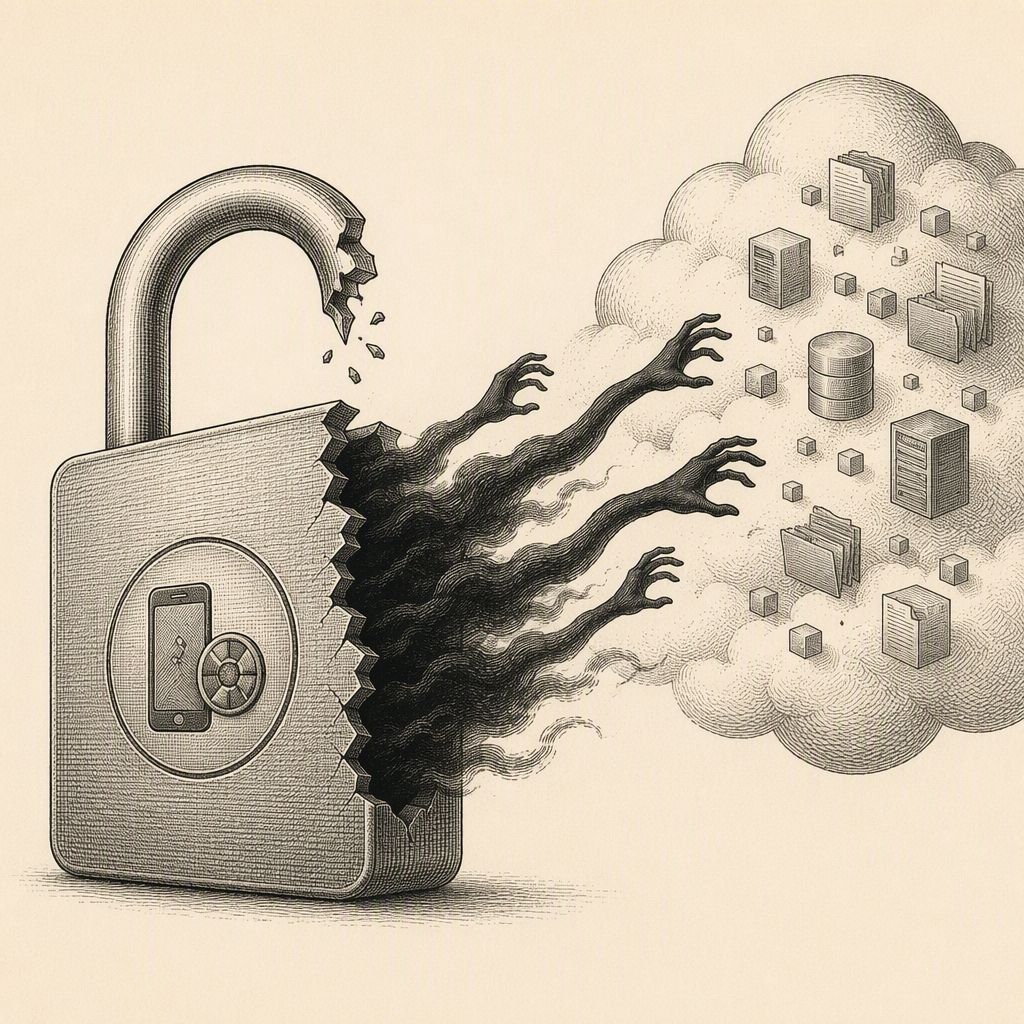
While multi-factor authentication (MFA) remains a cornerstone of modern cybersecurity, experts are warning that it is not a silver bullet against the evolving threat of OAuth consent abuse. Attackers are increasingly leveraging compromised accounts or malicious applications to trick users into granting excessive permissions through OAuth consent flows, bypassing traditional security measures like MFA.
The core issue lies in how OAuth consent works. Users are presented with a request to authorize an application to access specific resources or perform actions on their behalf. Even if MFA is used to log into the primary service, a subsequent malicious OAuth request can still be approved, effectively granting the attacker a foothold. This bypasses the intended security benefits of MFA, which primarily focuses on authenticating the user's identity, not the legitimacy of third-party application requests.
To combat this growing threat, organizations must move beyond relying solely on MFA and implement a comprehensive strategy for OAuth governance. This includes establishing clear policies for application integration, defining acceptable scopes of access, and ensuring that users are educated about the risks associated with granting consent to unknown or untrusted applications.
A critical component of this strategy is the enforcement of least-privilege principles. Applications should only be granted the minimum permissions necessary to perform their intended functions. This significantly reduces the potential impact if an application is compromised or if a malicious actor gains control of a legitimate application's credentials.
Furthermore, continuous monitoring of user consent grants is paramount. Organizations need visibility into which applications have access to their data and what permissions they hold. Proactive auditing and regular reviews can help identify suspicious or overly broad consent grants before they can be exploited.
Finally, establishing rapid revocation processes is essential. When a compromise is detected or an application is no longer needed, its access must be revoked immediately. This minimizes the window of opportunity for attackers to abuse granted permissions and helps maintain a strong security posture.
By adopting these layered security measures—robust governance, least-privilege scopes, active monitoring, and swift revocation—organizations can build a more resilient defense against OAuth consent abuse, ensuring that MFA is complemented by a holistic approach to application security and identity management.