
London Hotel's Admin Credentials Found on Whiteboard Behind Front Desk
A London hotel's administrative login details for its booking website were discovered written on a whiteboard behind the front desk, exposing guest data and reservation details.
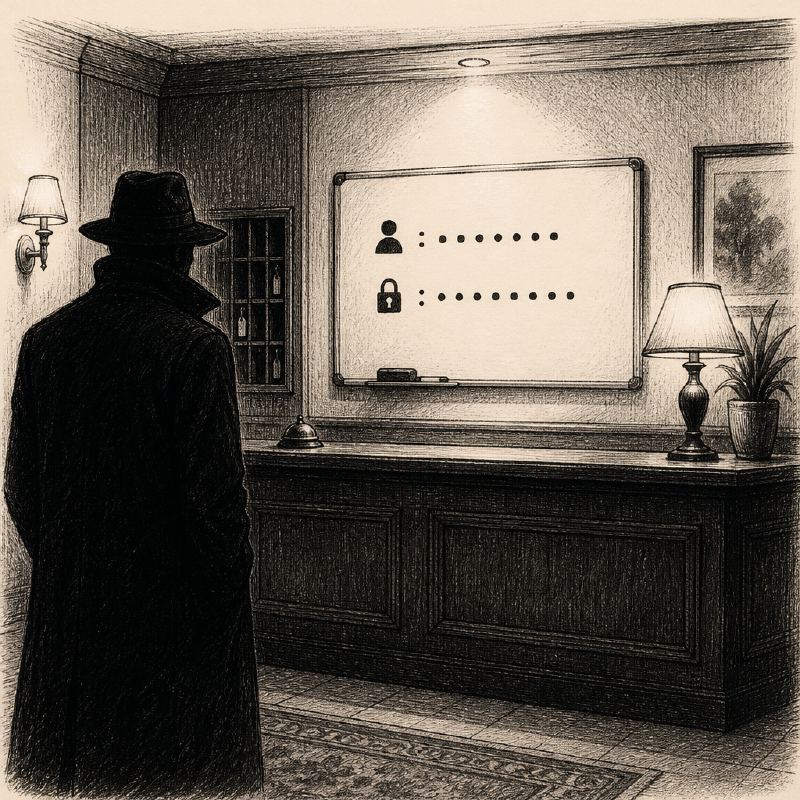
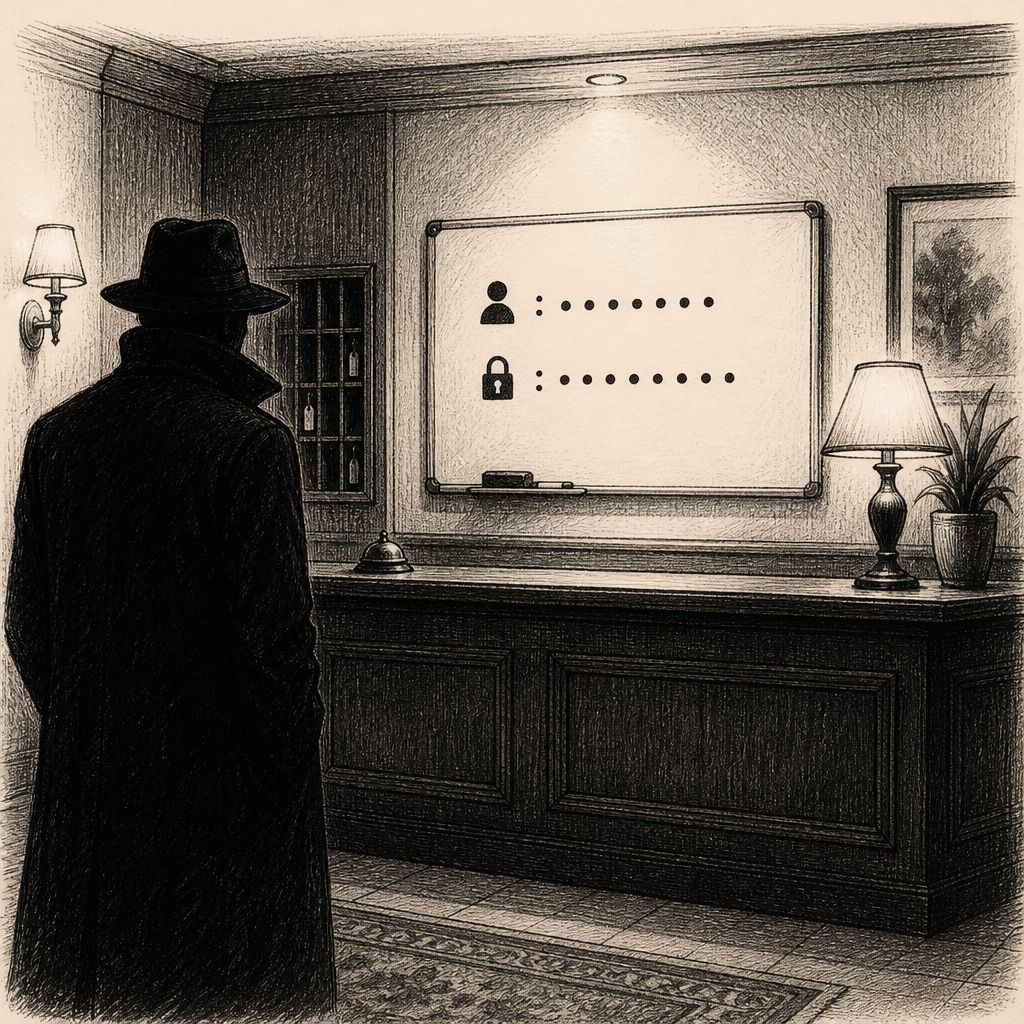
A startling lapse in basic cybersecurity hygiene at a London hotel has exposed sensitive guest information and the potential for reservation manipulation. The hotel's administrative username and password for its Booking.com portal were found written on a whiteboard in a back room, visible to anyone near the front desk.
The discovery was made by Neycho Tepavicharov, co-founder of web hosting company Flashcloud, who was a guest at the hotel. He observed that the door behind the front desk was ajar, revealing a whiteboard within. Scrawled on this board in plain sight were the credentials for the hotel's critical booking system.
Tepavicharov highlighted the significant risks associated with such an oversight. "With that login, someone could change or cancel reservations, see guests’ names and contact details, or message guests pretending to be the hotel," he explained. He further noted that "Fake 'please confirm your payment' messages sent from compromised hotel accounts are a well-known scam," indicating a direct pathway for attackers to target guests with convincing phishing attempts.
The potential impact extends beyond guest data. Attackers could have disrupted hotel operations, manipulated bookings, or used the access to conduct targeted scams against individuals. The actual extent of the risk would have depended on the specific security configurations of the Booking.com account, such as whether multi-factor authentication was enabled.
Recognizing the severity of the situation, Tepavicharov informed the hotel manager, who was reportedly mortified and expressed gratitude for the warning. The staff had apparently not considered the exposed credentials a significant risk, viewing the whiteboard as a convenient way for the team to share a single login.
Following the incident, the hotel promptly changed its credentials and implemented better security practices. Tepavicharov also mentioned that the hotel subsequently moved its website hosting to his company, Flashcloud.
This incident serves as a stark reminder of fundamental security principles. Tepavicharov emphasized the importance of assigning dedicated credentials to each staff member and enforcing multi-factor authentication. "The lesson is an old one, but it keeps happening," he stated. "Shared logins end up written somewhere convenient. Give each staff member their own login, turn on two-factor authentication, and keep passwords in a password manager, not on the wall."
The case underscores the persistent challenge of human error and negligence in cybersecurity, even in seemingly straightforward scenarios. It highlights that robust technical defenses can be rendered ineffective by basic security oversights, particularly in the hospitality sector where ease of access for staff is often prioritized over security.