
Linux Kernel Net Scheduler Vulnerability Allows Local Privilege Escalation
A local privilege escalation vulnerability in the Linux Kernel's Net Scheduler Qdisc component, tracked as CVE-2026-98797, allows low-privileged users to gain elevated privileges.
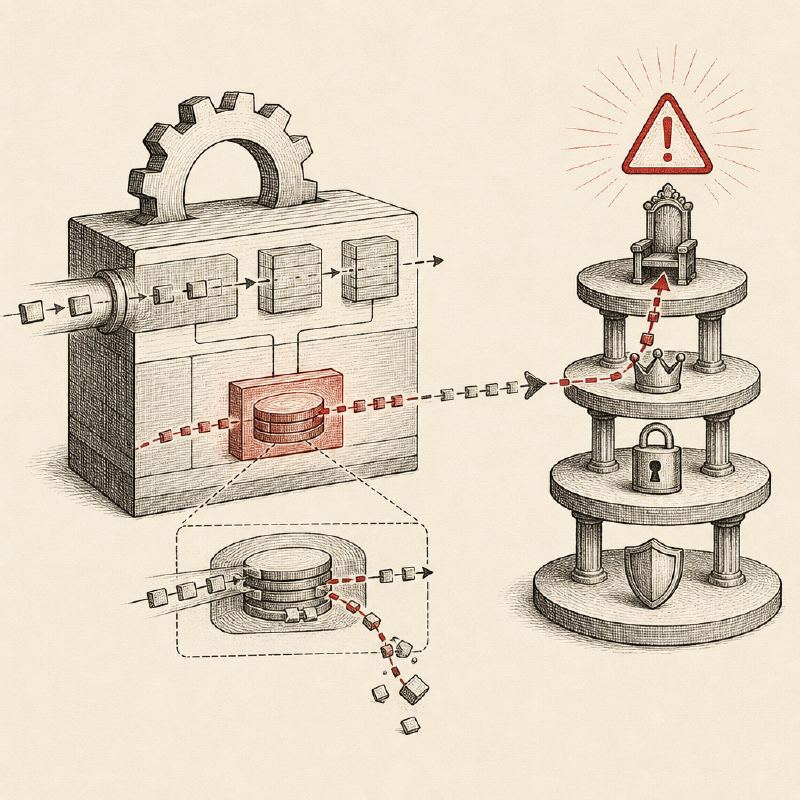
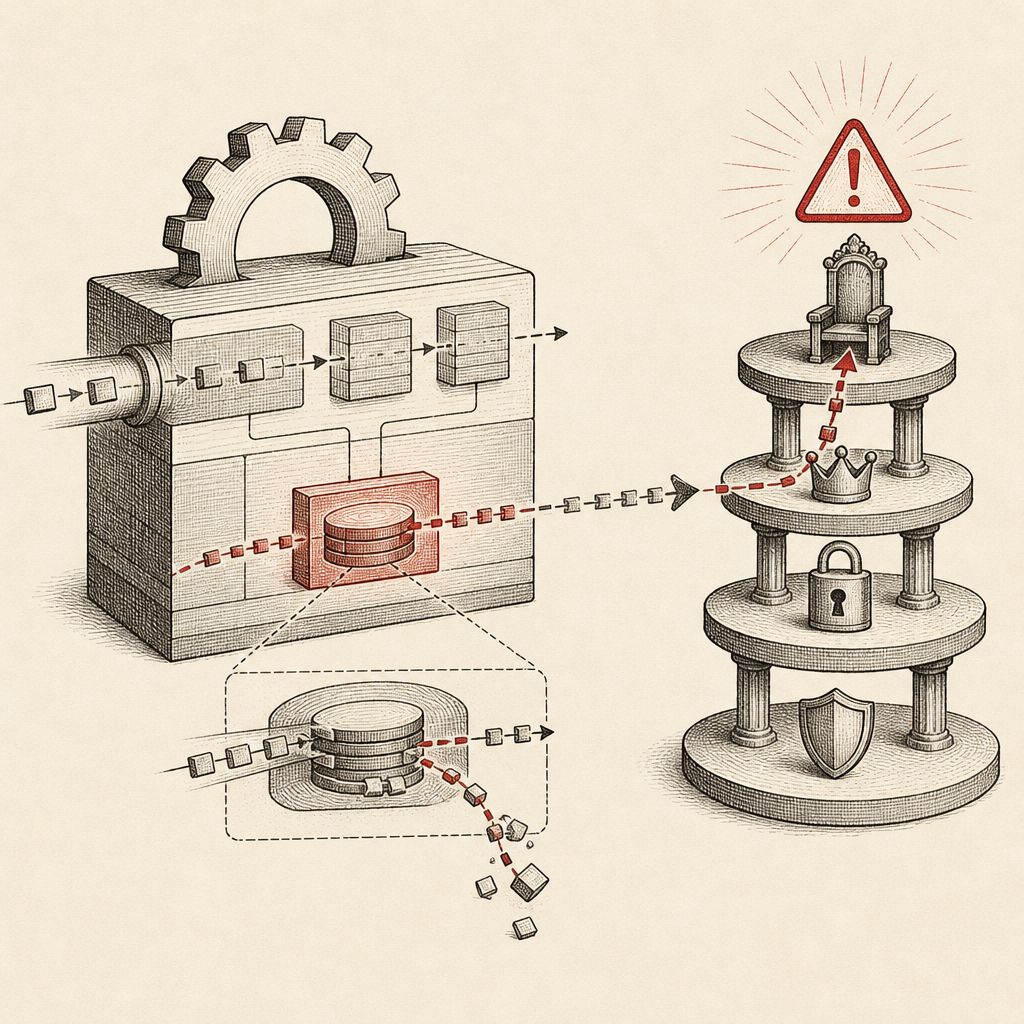
A critical local privilege escalation vulnerability has been identified within the Linux Kernel's Net Scheduler Qdisc component, assigned the identifier CVE-2026-98797 by the Zero Day Initiative (ZDI). This flaw, which carries a CVSS score of 8.8, enables attackers who have already achieved low-privileged code execution on a target system to escalate their privileges to that of the kernel.
The vulnerability specifically resides within the taprio_enqueue function. The root cause is the improper validation of user-supplied data, which leads to an out-of-bounds write operation. This means the function attempts to write data beyond the boundaries of an allocated array, corrupting memory and potentially allowing an attacker to gain control of the kernel's execution context.
Successful exploitation of this vulnerability would grant an attacker the ability to execute arbitrary code with kernel-level privileges. This level of access is the highest possible on a system and would allow an attacker to bypass all security restrictions, install persistent backdoors, exfiltrate sensitive data, or completely compromise the affected machine.
Linux has released a patch to address this vulnerability. The fix can be found in the official Linux kernel repository, with a specific commit detailing the resolution available on GitHub. The disclosure timeline indicates that the vulnerability was reported to the vendor on September 10, 2026, and the coordinated public release of the advisory occurred on November 13, 2026.
This vulnerability was discovered and reported by ELDEN, who is credited in the advisory. The ZDI's proactive disclosure process ensures that users are informed of such critical flaws once a patch is available, allowing them to secure their systems promptly.
While the vulnerability requires local code execution as a prerequisite, the ability to escalate privileges to the kernel level makes it a significant threat. Administrators of Linux systems should prioritize applying the available patch to mitigate the risk of exploitation. The nature of the vulnerability, involving array index validation, is a common class of bugs that can lead to severe security consequences if not properly handled.
This discovery highlights the ongoing need for rigorous security auditing of core operating system components. The Linux kernel, being a foundational element of many systems, is a frequent target for vulnerability research and exploitation. The ZDI's role in identifying and coordinating the disclosure of such flaws is crucial for maintaining the security posture of the broader technology ecosystem.