
Kaspersky Enhances OT Network Security with Machine Learning Event Processor
Kaspersky Industrial CyberSecurity for Networks 5.0 introduces a Machine Learning Event Processor (MLEP) to improve the detection of subtle anomalies in Operational Technology (OT) device network behavior.
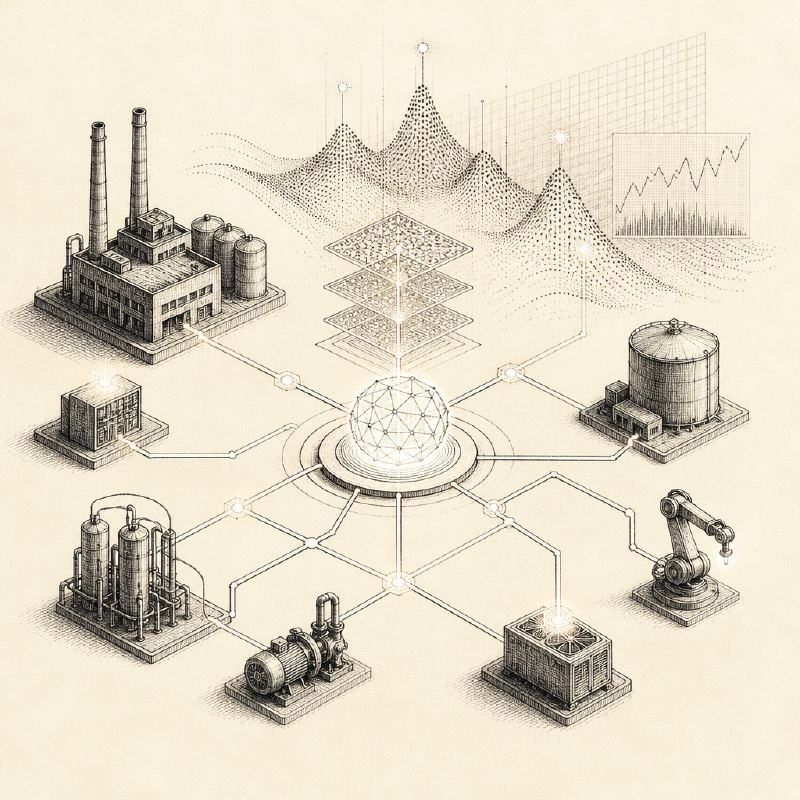
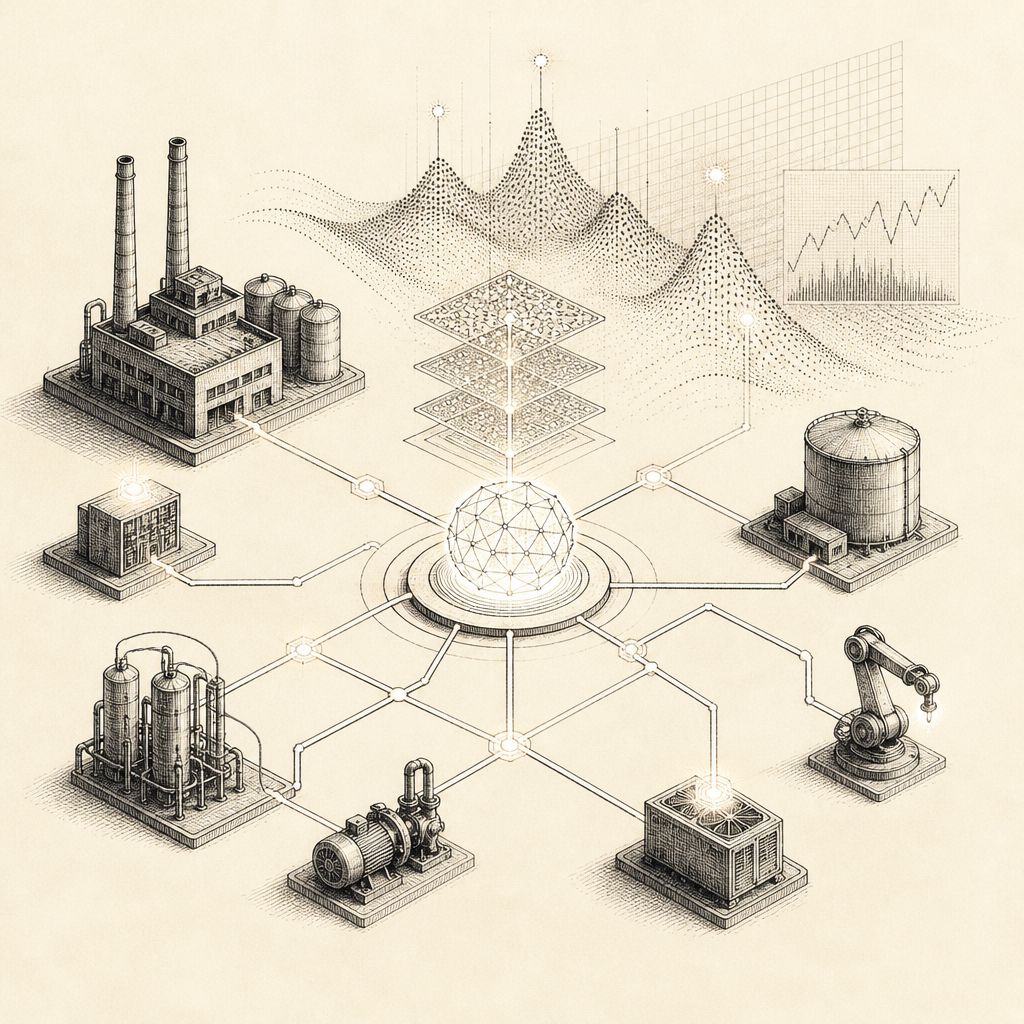
Kaspersky has released version 5.0 of its Industrial CyberSecurity for Networks (KICS) platform, featuring a new Machine Learning Event Processor (MLEP) designed to enhance the security of Operational Technology (OT) environments. The MLEP aims to address the challenge of distinguishing malicious activity from normal network traffic in industrial settings, where attackers often leverage legitimate tools and techniques.
Traditional security methods struggle with subtle anomalies, such as atypical data sources, access times, or volumes, especially when devices use proprietary protocols or encryption. Incomplete asset inventories further complicate the detection of unauthorized connections. The MLEP tackles this by analyzing patterns in network interactions to refine device categorization and identify deviations from normal behavior, even when the activity appears to use standard protocols.
KICS for Networks builds upon its existing Asset Discovery technology, which uses passive network traffic analysis to identify devices and their interactions. Recognition rules help determine device categories and extract information like vendor and model. Active polling modules (APMs) can also gather more detailed configuration and firmware data when permitted, though this is not always feasible or sufficient.
The MLEP processes network sessions by aggregating data into short, 15-second fragments. Each fragment captures key information such as endpoints (IP, MAC, port), data exchange direction, protocol, and packet counts and sizes, forming an 'event' with a timestamp. This sequence of events creates a behavioral history for each device, detailing its communication patterns over time.
This approach allows MLEP to detect anomalies by comparing a device's current network activity against its established behavioral history. The system uses a spiking neural semantic network (NSN) architecture, which structures information as a multilayer ordered graph. This allows the network to learn and operate on event streams concurrently, creating new neurons for novel events and refining its understanding of normal and abnormal behavior.
By analyzing these aggregated events, MLEP can identify subtle shifts in communication intensity or patterns that might indicate compromise, even if the individual events themselves do not trigger traditional alerts. This is particularly valuable in OT environments where downtime is costly and precise identification of threats is critical.
The introduction of MLEP aligns with industry trends and recommendations, such as those from CISA, emphasizing the importance of robust OT asset management and visibility. As organizations increasingly invest in these capabilities, tools like KICS 5.0 with MLEP offer a more sophisticated approach to safeguarding critical industrial infrastructure.
The system's ability to refine device categories and detect anomalies based on learned behavior patterns provides a crucial layer of defense against advanced threats that evade signature-based detection and exploit the complexities of industrial network communications.