
Johnson Controls EasyIO Controllers Vulnerable to Sensitive Information Exposure
CISA has issued an advisory for Johnson Controls EasyIO Neo Series EC and CW Controllers, detailing a vulnerability that could allow attackers to access sensitive information.
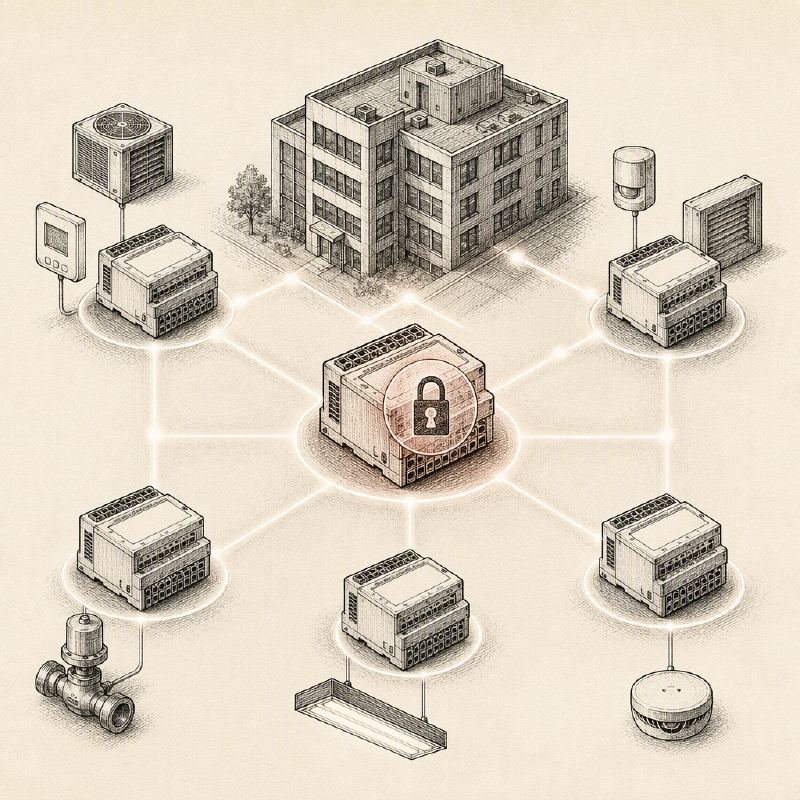
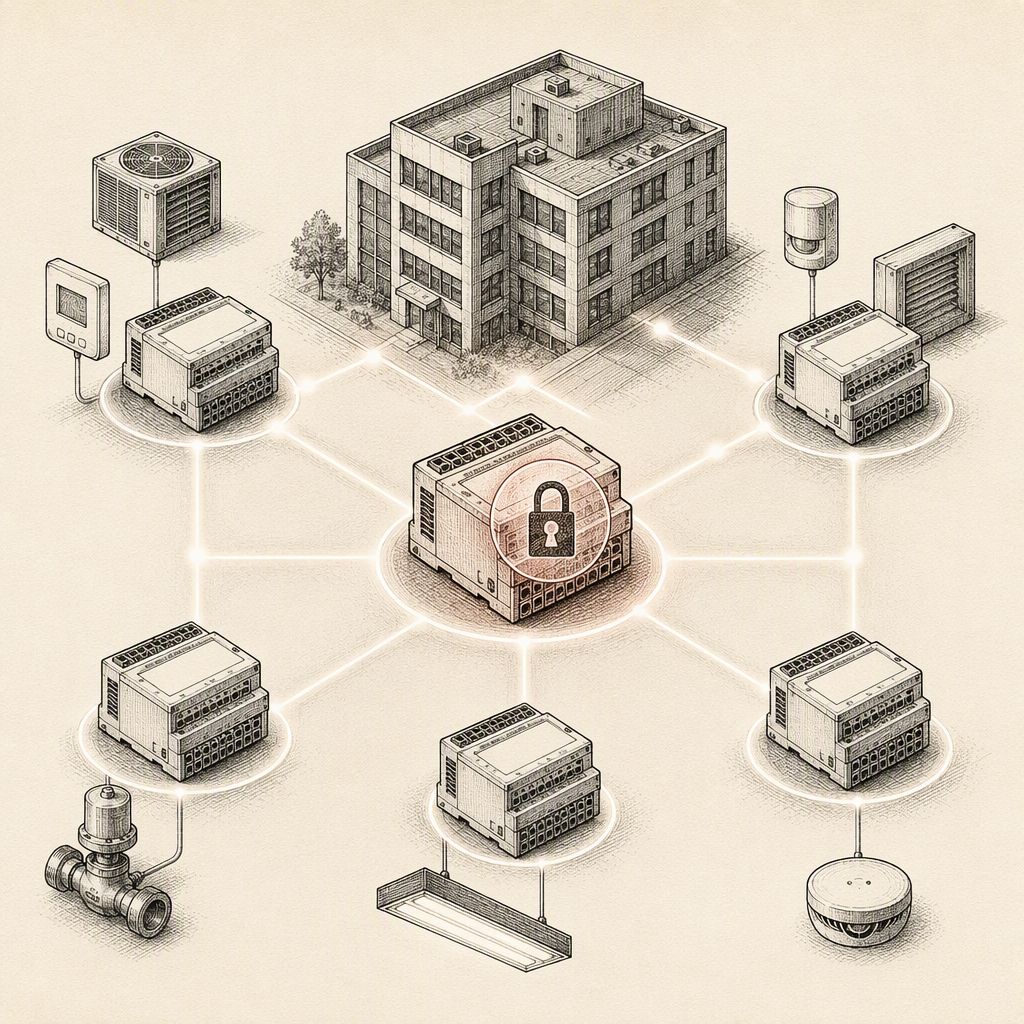
CISA has released an advisory detailing a critical vulnerability affecting Johnson Controls EasyIO Neo Series EC and CW Controllers. The vulnerability, identified as CVE-2026-64892, could permit an unauthorized attacker to gain access to sensitive information. This exposure could then be leveraged to facilitate further attacks against the affected systems.
The affected products include specific firmware versions of the EasyIO Neo Series EC Controllers (V3.3b63 and V3.3b62) and CW Controllers (V3.3b25 and V3.3b24). These controllers are integral components in building automation and control systems, managing functions such as HVAC, lighting, and energy management. They support standard protocols like BACnet and Modbus, making them widely deployable across various critical infrastructure sectors, including critical manufacturing, commercial facilities, government services, transportation systems, and energy.
The vulnerability, classified under CWE-200 (Exposure of Sensitive Information to an Unauthorized Actor), carries a CVSS v3.1 base score of 3.5 (LOW) and a CVSS v4.0 score of 4.8 (MEDIUM). The CVSS v4.0 vector string indicates a network attack vector, low complexity, no attack complexity reduction, high privileges required, user interaction required, and low impact on confidentiality, integrity, and availability.
Johnson Controls has acknowledged the vulnerability and has released updated firmware versions to address the issue. Users are strongly advised to upgrade to EC firmware V3.3b64 or CW firmware V3.3b26, or later versions, as soon as operationally feasible. For organizations unable to immediately apply updates, Johnson Controls recommends several mitigation strategies. These include implementing robust physical access controls, monitoring network traffic for suspicious activity, enforcing the principle of least privilege, disabling debug interfaces where possible, and deploying intrusion detection/prevention systems.
Further mitigation guidance can be found in the Johnson Controls Product Hardening Guide and the JCI Universal Hardening Guide, accessible via the Johnson Controls Trust Center. While these mitigations can reduce risk, they may not fully remediate the vulnerability, and updating to the fixed firmware remains the recommended course of action.
CISA encourages users to implement defensive measures and conduct thorough impact and risk assessments before deploying any security updates or mitigations. Organizations are reminded to follow established procedures for testing and applying updates in ICS/OT environments, including backups and change management protocols.
At the time of the advisory, CISA reported no known public exploitation of this specific vulnerability. However, the potential for sensitive information disclosure in critical infrastructure systems underscores the importance of prompt patching and diligent security practices.
This advisory provides specific details on affected firmware versions for both the EasyIO Neo Series EC and CW Controllers, including EC V3.3b62 and V3.3b63, and CW V3.3b24 and V3.3b25. It also outlines the CVSS v3.1 and v4.0 scores, indicating a MEDIUM severity, and details recommended mitigations such as enforcing HTTPS, disabling HTTP, network segmentation, and using VPNs, alongside specific detection indicators for monitoring.