
IDENTOS PolicyArc Offers Granular Access Control for AI Agents
IDENTOS PolicyArc is a new access policy solution designed to manage permissions for AI agents, enabling task-specific, time-limited access to address growing enterprise security concerns.
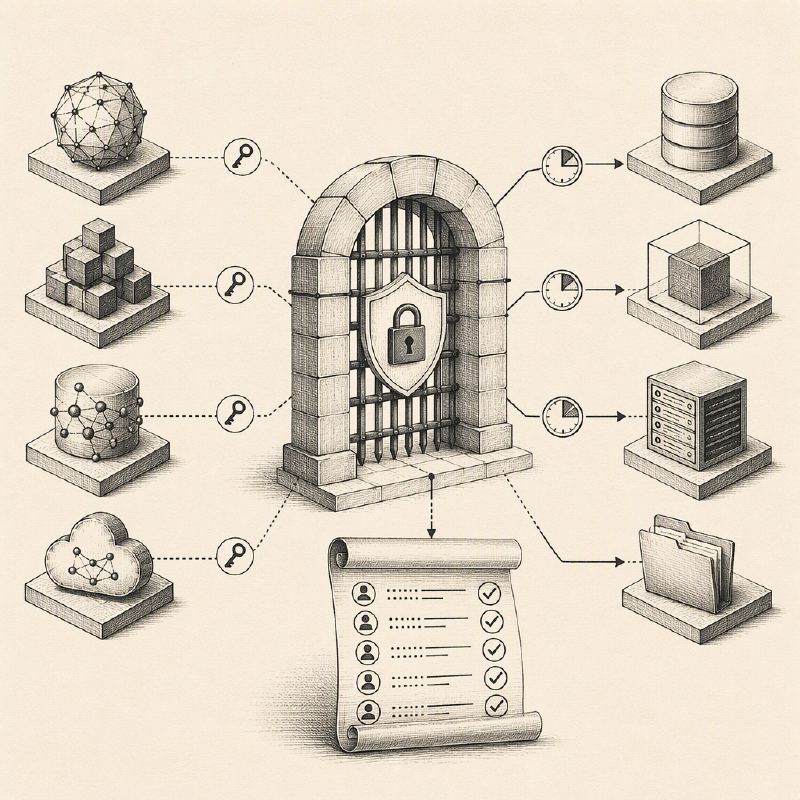
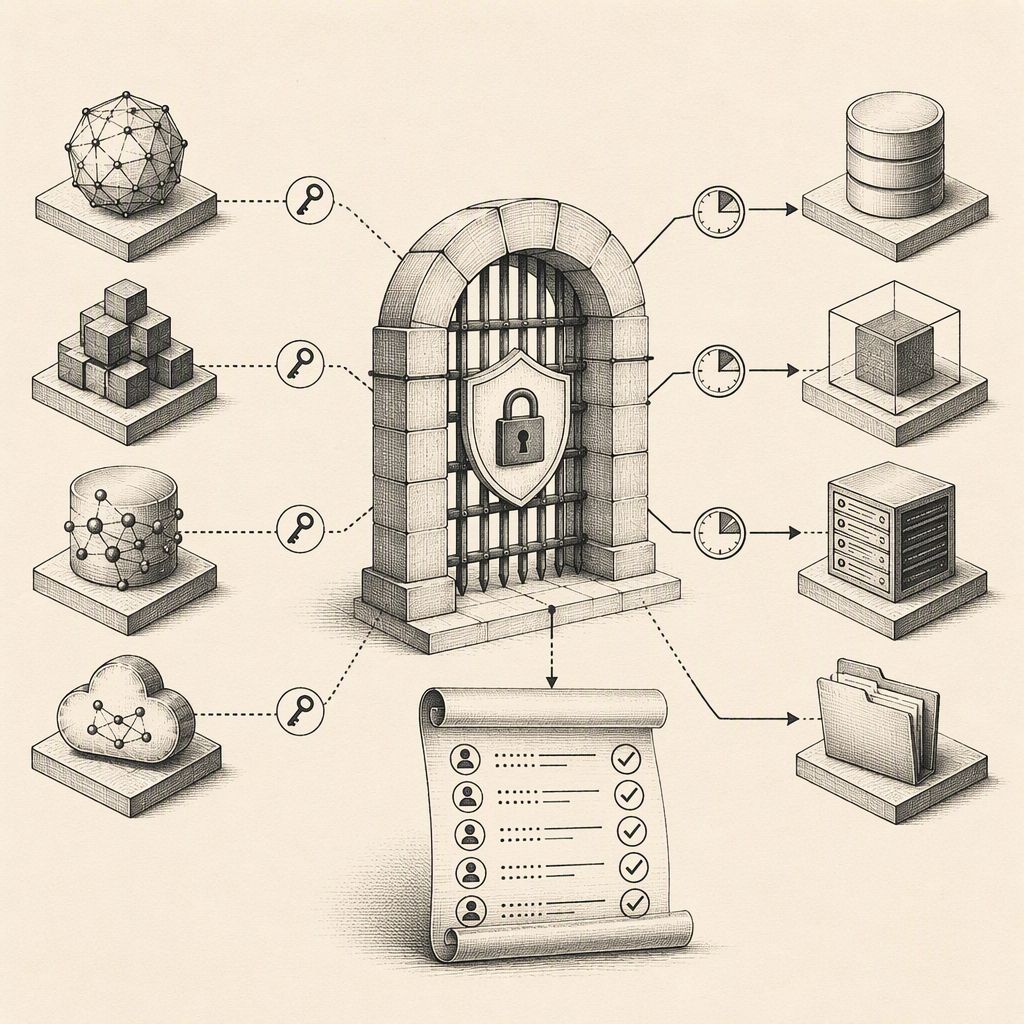
IDENTOS has announced the general availability of PolicyArc, a new solution aimed at providing security, platform, and compliance teams with a centralized platform for defining, enforcing, and auditing access policies across their applications. The core innovation of PolicyArc lies in its ability to safely extend access not only to human users and services but also to the increasingly prevalent AI agents that operate on behalf of users within enterprise systems.
This development builds upon IDENTOS's extensive experience, spanning over 12 years, in managing identity and access within sensitive environments such as Canadian government and healthcare systems. The timing of PolicyArc's release is critical, as organizations are rapidly adopting AI agents capable of accessing data, executing actions, and making decisions within their internal systems. Traditional access control mechanisms, however, were not designed to grant these agents the precise, limited permissions required for specific tasks and durations.
The need for such a solution is underscored by recent industry reports. According to IBM and Ponemon Institute’s 2026 Cost of a Data Breach Report, a staggering 92% of organizations that experienced an AI-related breach lacked adequate AI access controls. PolicyArc is positioned to mitigate this risk, while also addressing the persistent challenge of access policies that are often slow to adapt and difficult to audit.
PolicyArc offers several key functionalities designed to enhance security and compliance. It enables individuals to grant AI agents a scoped, time-limited version of their own access, ensuring the agent has sufficient permissions for its task without overreach. This access is automatically revoked once the task is completed or the designated time window expires. Furthermore, PolicyArc enforces consent on every access request, verifying not just against policy but also against the explicit agreements made by the data owner, rather than solely at login.
The system also facilitates dynamic access decisions by combining static information, such as user roles and identity verification status, with real-time contextual data, including resource sensitivity and workflow stage. This allows for immediate decisions to allow, deny, or request additional verification. A significant advantage is the ability to define a policy for a resource type once, ensuring consistent application across all connected applications. This approach allows for rapid updates to resource types and policies, keeping access rules synchronized with product development.
Moreover, PolicyArc provides an audit trail by default, automatically logging every access decision. This ensures that evidence for audits and compliance checks is readily available from the outset, eliminating the need for post-incident reconstruction. The solution is primarily targeted at teams responsible for access decisions, including platform and security engineering leads managing authorization across diverse product surfaces, compliance and risk leaders needing to demonstrate appropriate access, and development teams building AI-agent features who require a secure delegation mechanism without building custom infrastructure.
Alec Laws, CTO at IDENTOS, emphasized the solution's design philosophy: "Most systems only know how to grant broad, standing access. That’s fine for a person, but reckless for an agent. We built PolicyArc so a team can hand an agent exactly the permission it needs for one task, nothing more. When the task ends, the access disappears, and every decision is on record."