
Hoxhunt Automates Phishing Investigations and Email Removal
Hoxhunt's expanded Respond platform now automates phishing investigations and email removal, aiming to drastically reduce the workload on security operations teams.
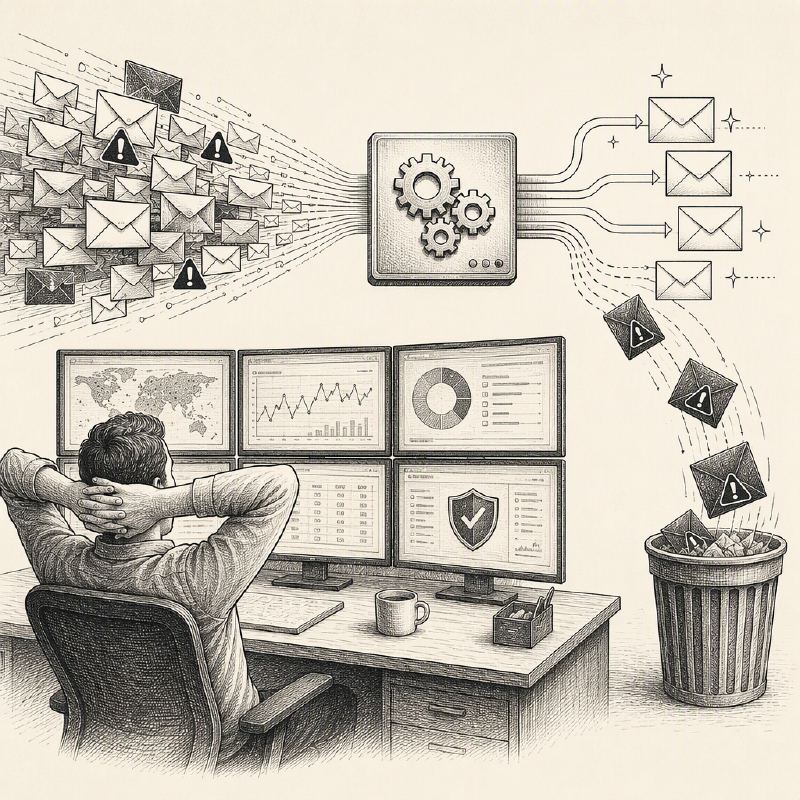
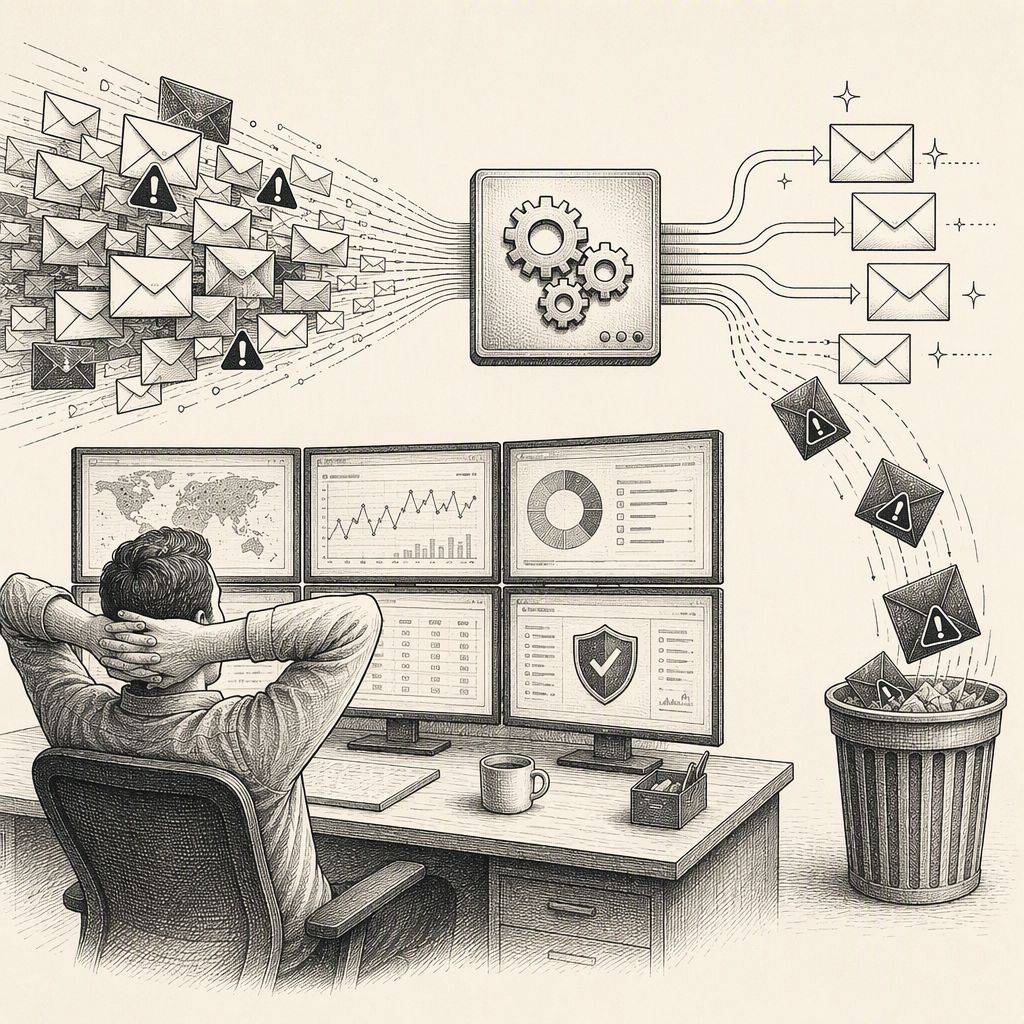
Hoxhunt has announced significant enhancements to its Respond platform, an automated email incident response solution designed for security operations centers (SOCs). The expanded capabilities promise to automate the investigation of reported phishing attempts and the subsequent removal of malicious emails, with the goal of reducing the number of tickets requiring direct analyst attention by up to 99% and remediating confirmed threats in under a minute.
The effectiveness of employee phishing training, while a critical security win, often leads to an overwhelming volume of reported emails for SOC teams. Hoxhunt's data indicates that approximately 80% to 85% of these employee-reported emails are benign. The expanded Respond platform is engineered to tackle this challenge head-on by automatically investigating each reported email, grouping similar reports into a single campaign-level incident, and suppressing safe or duplicate submissions. This allows SOC analysts to focus on genuine threats rather than sifting through numerous false positives.
Once a threat is confirmed, Hoxhunt Respond automatically locates and removes matching malicious messages across all affected inboxes. The platform offers reversible remediation, ensuring that legitimate emails are not permanently lost, and provides immediate feedback to employees who reported the threat. This closed-loop system reinforces positive security behaviors and streamlines the incident response process.
The Hoxhunt Respond platform is built around four core components. 'Instant Feedback' provides employees with real-time responses to their threat reports, reinforcing the behavioral changes learned in simulated training. 'Incident Orchestration' intelligently classifies and correlates reported emails, presenting analysts with a consolidated view of threats rather than a flood of individual alerts. 'Search & Destroy' is the automated remediation engine, capable of finding and removing malicious emails swiftly. Finally, 'Feedback Rules' identifies known safe communications, offering immediate, customizable feedback to employees and reducing unnecessary alerts while maintaining the valuable reporting habit.
"Getting employees to habitually report suspicious emails is one of the biggest wins we can achieve in cybersecurity, and a surge of threat intelligence should help, not hinder, the SOC," stated Mika Aalto, CEO of Hoxhunt. "Hoxhunt transforms the workforce into a distributed network of threat sensors, and Respond finds the signal so the SOC can quickly respond, without generating more manual work. One employee can spot the attack, and automation can remove it for everyone else."
The platform leverages a decade of real-world employee-reported phishing data and intelligence from over five million "human sensors" to train its models. This extensive dataset allows Hoxhunt Respond to classify malicious emails with 96% accuracy and safe emails with over 99% accuracy, ensuring reliable threat detection and automated response.
Enterprise companies using Hoxhunt Respond have reported significant time savings, with documented instances of over 900 hours of SOC analysis time saved per month. This efficiency gain is crucial as organizations face increasingly sophisticated and voluminous phishing attacks, allowing security teams to reallocate resources to more strategic initiatives.