
Hackers Compromise ccTLD Registries to Issue Fake Google HTTPS Certificates
Attackers gained control of the .gh, .sl, and .as country-code top-level domains, enabling them to issue fraudulent HTTPS certificates for Google domains and other major organizations.
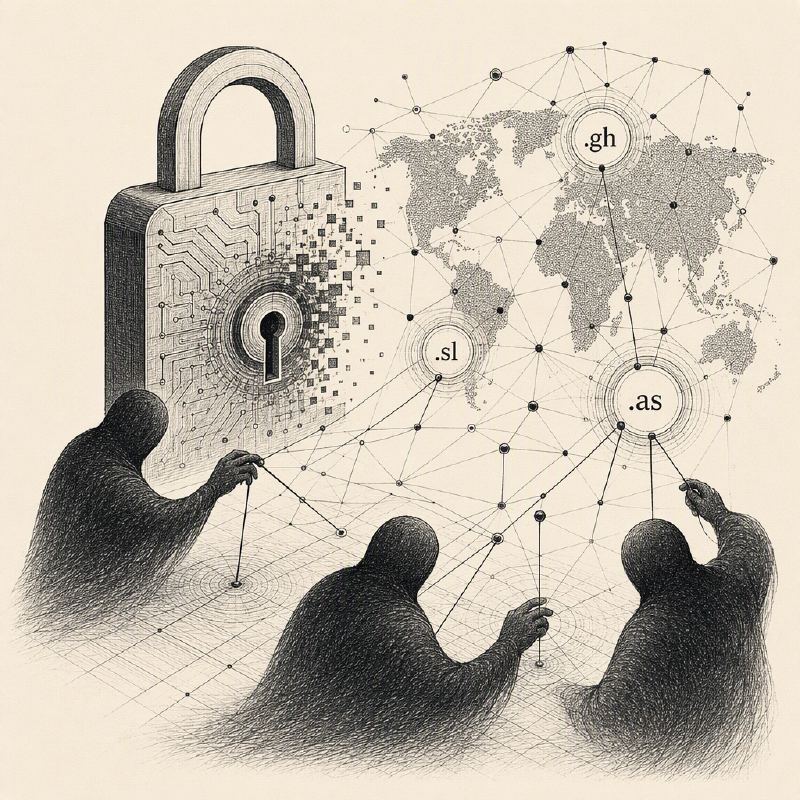
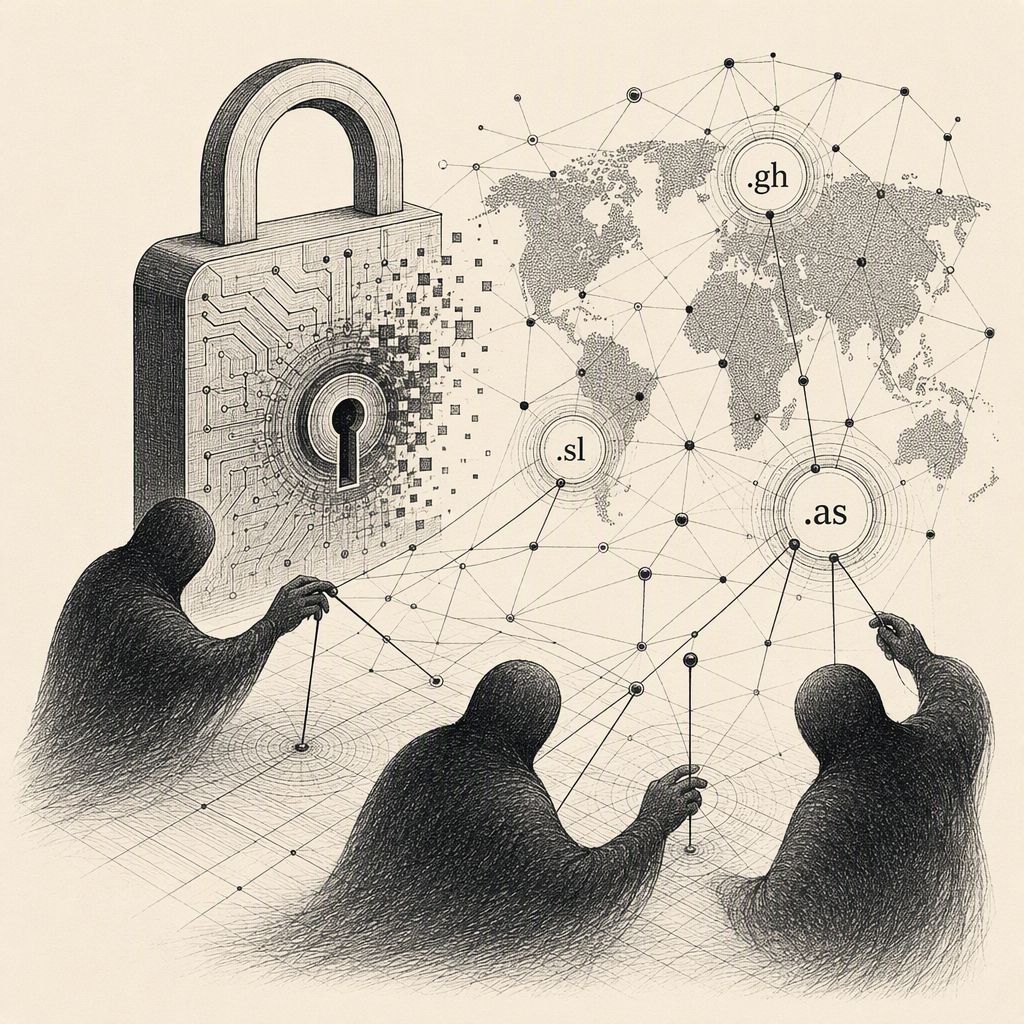
In a sophisticated attack targeting the integrity of internet trust, threat actors have successfully compromised the operators of three country-code top-level domains (ccTLDs): .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa). This breach granted them the ability to alter DNS records and, critically, to obtain unauthorized HTTPS certificates for domains belonging to Google and other large organizations.
Google disclosed the incident, emphasizing that its own systems were not compromised. The attackers exploited their control over the ccTLD registries to manipulate the Domain Name System (DNS) infrastructure. By controlling the authoritative DNS records for domains under these TLDs, they could then trick certificate authorities into issuing fraudulent SSL/TLS certificates.
These certificates, when issued, would appear legitimate to browsers and other clients, potentially allowing attackers to conduct man-in-the-middle attacks, intercept sensitive traffic, or impersonate legitimate services. The compromise of ccTLD registries represents a significant threat, as these domains are fundamental to the global internet's naming and security infrastructure.
The implications of such an attack are far-reaching. While Google stated its systems were unaffected, the ability to obtain fraudulent certificates for its domains could have enabled sophisticated phishing campaigns, espionage, or disruption of services if exploited further. The attackers' motives remain under investigation, but the technical capability demonstrated points to a well-resourced and knowledgeable adversary.
This incident highlights a critical vulnerability in the hierarchical trust model of the internet. Certificate Authorities (CAs) rely on the accuracy of DNS information to validate domain ownership before issuing certificates. When the authoritative source for that DNS information—in this case, the ccTLD registry—is compromised, the entire validation process can be subverted.
While Google's infrastructure and security measures appear to have mitigated the direct impact on its services, the broader implications for other organizations and the internet's trust ecosystem are significant. The incident serves as a stark reminder of the need for robust security practices not only for end-users and software vendors but also for the foundational infrastructure providers that underpin global connectivity.
Further investigation is ongoing to determine the full extent of the compromise and to implement necessary remediation steps to prevent similar incidents. The security community is closely monitoring developments, as the compromise of ccTLD registries could have cascading effects on internet security and user trust.