
Hacked Thai College Website Abused for Illegal Online Casino Redirects
Attackers exploited a compromised Thai educational website to redirect Google searchers to an illegal online casino, bypassing ad screening through legitimate infrastructure.
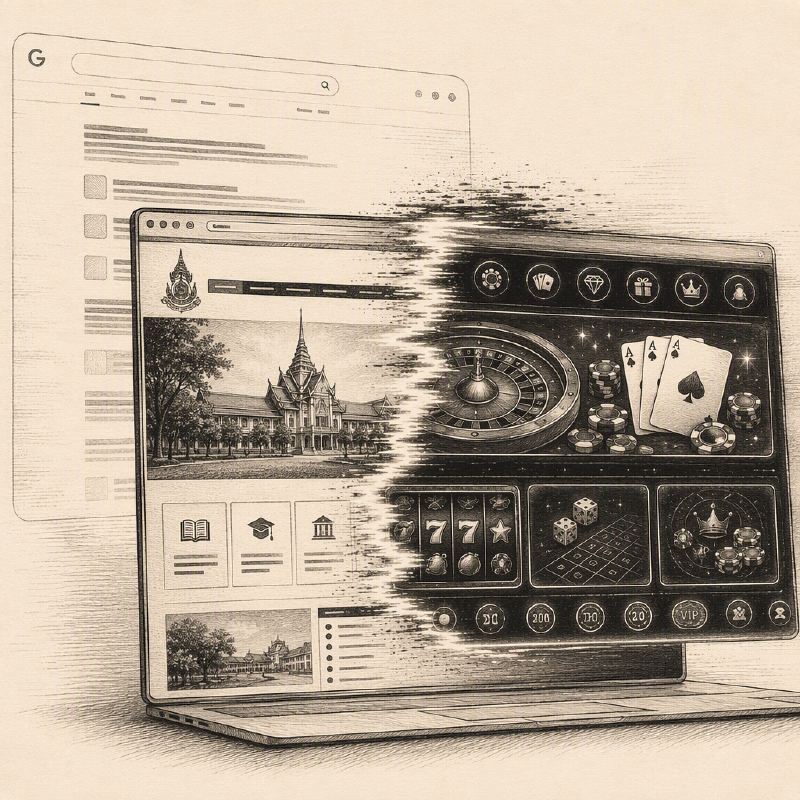
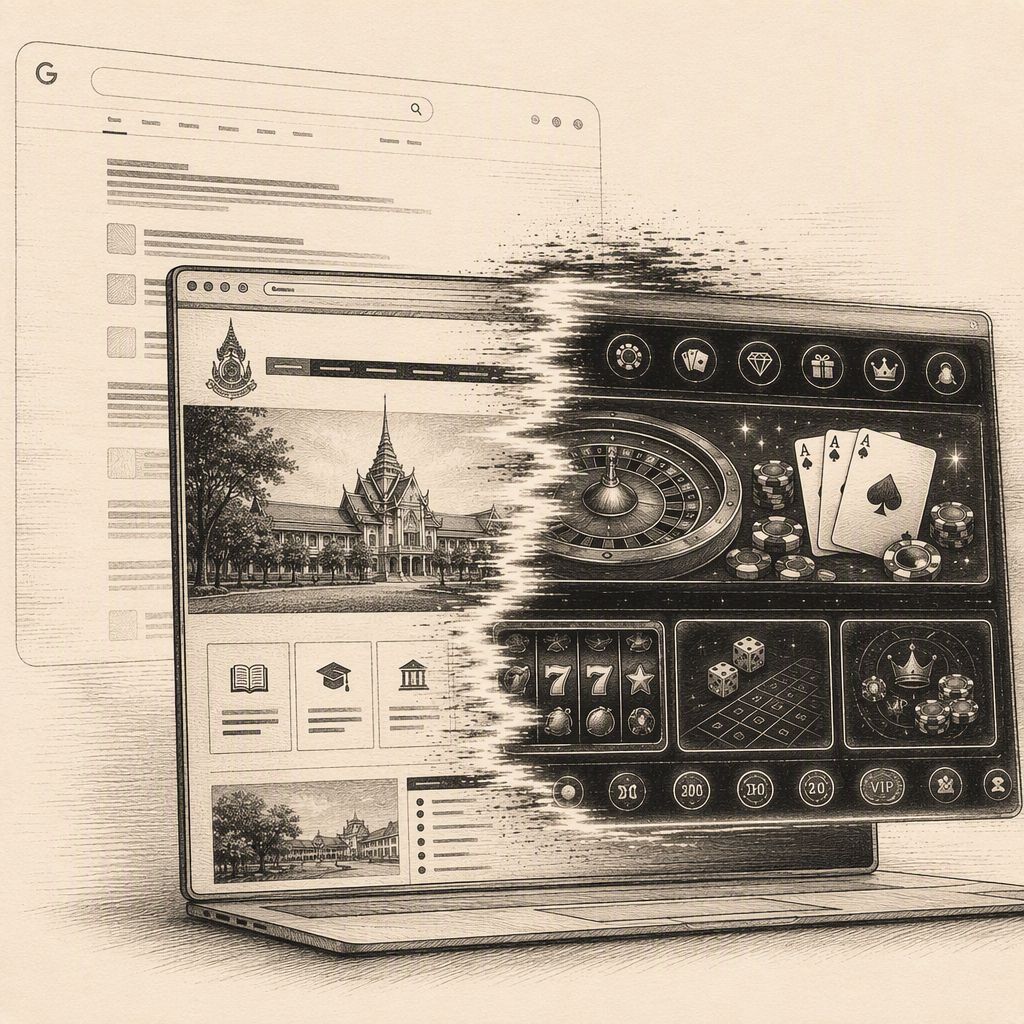
A compromised Thai college website has been weaponized by attackers to redirect unsuspecting Google searchers towards an illegal online casino. The scheme, identified by the anti-fraud platform ADEX, leveraged the legitimate domain km.chpc.ac.th, belonging to Thailand's educational institution zone (.ac.th), to bypass advertising screening and ad cloaking mechanisms without deploying any malicious code.
This tactic represents a significant evolution in how threat actors abuse trusted online infrastructure. Unlike traditional cloaking methods that rely on the attacker's own servers to differentiate between human visitors and crawlers, this campaign utilized entirely legitimate components. The attackers planted a casino-themed page on the hacked college website, which was subsequently indexed by Google and ranked highly for specific search queries. Users clicking on what appeared to be a standard Google search result were then redirected to an offshore gambling site, a service illegal to advertise within Thailand.
The attack chain began with an advertiser whose traffic was routed through a seemingly innocuous Google search results page. This allowed the malicious destination to remain hidden from ad moderators and automated crawlers. The critical redirection step occurred after the initial click, on a third-party website entirely separate from the advertiser's infrastructure. ADEX highlighted that each step in the chain—the Google search, the college website, and the redirect—functioned as intended, with the malicious outcome arising solely from their combination.
This incident is indicative of a broader trend where attackers are increasingly borrowing trusted domains, particularly those within government (.gov) and educational (.edu) zones, to host illicit content. ADEX reports similar tactics are being observed globally. For instance, Thailand's Ministry of Digital Economy and Society has identified millions of gambling-related URLs across numerous public-sector sites. Indonesia's Ministry of Communication and Informatics has blocked hundreds of government and educational sites containing gambling content, with .ac.id domains being particularly hard-hit.
Researchers have also noted the widespread abuse of these trusted domains. A recent academic crawl of Indonesian domains revealed a significant number of compromised sites and pages laden with gambling keywords. Furthermore, an underground marketplace has been observed selling access to over 15,000 compromised .gov, .edu, and country-code domains, with a notable concentration of campaigns targeting Turkey's gambling market. Similar injection campaigns have been identified affecting hundreds of government and university sites worldwide.
Google's efforts to combat this issue, such as its "site reputation abuse" policy introduced in March 2024 and tightened in November 2024, may not fully address this specific type of attack. ADEX points out that the policy is primarily aimed at sites that intentionally rent out their reputation, rather than those where adversaries silently hijack web servers. This leaves institutions whose servers are compromised without their knowledge largely unprotected by current regulations.
ADEX recommends that ad networks and advertisers treat restricted domain zones like .ac., .gov, and .edu with heightened suspicion, rather than as a guarantee of legitimacy, especially when they appear in redirect chains. The platform also advises advertisers to conduct post-approval checks on campaigns, as redirect chains can be reconfigured at any time, and to be wary of valid TLS certificates as a sole indicator of trustworthiness. Website owners are encouraged to maintain an inventory of their subdomains and to periodically scan their own domains from an attacker's perspective to detect hidden injected pages.
ADEX, an AI-driven anti-fraud and traffic-quality platform, emphasizes that traditional security measures focusing solely on the landing page are insufficient. The malicious activity in these cases often resides further down the redirect chain, making it invisible to standard checks. This evolving threat landscape underscores the need for more robust, multi-layered security approaches that account for the sophisticated ways attackers leverage legitimate infrastructure.