
Google Pauses Open-Source Bug Bounty Amidst AI-Generated Submission Flood
Google has temporarily halted its Open Source Software Vulnerability Reward Program (OSS VRP) due to an overwhelming influx of invalid, AI-generated vulnerability reports.
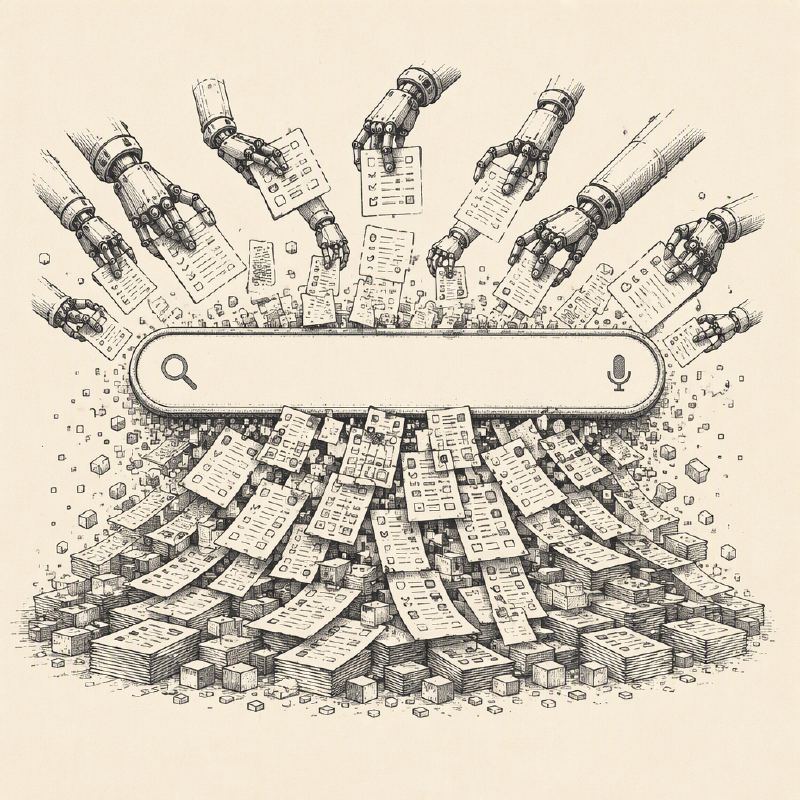
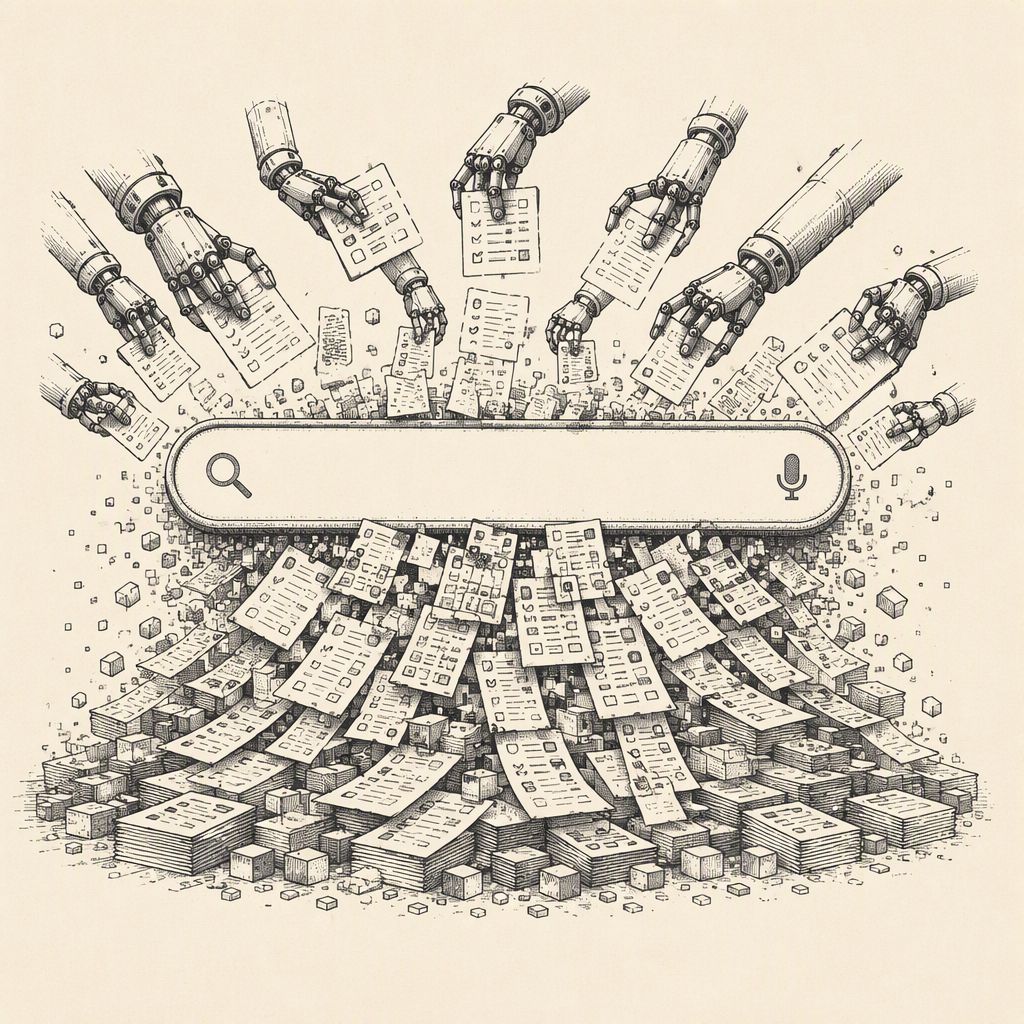
Google has ceased accepting new vulnerability submissions to its Open Source Software Vulnerability Reward Program (OSS VRP), citing a significant surge in automated, invalid reports. The program, which rewards security researchers for discovering and reporting flaws in Google's open-source projects like Go, Angular, and Protocol Buffers, is no longer taking submissions as of October 1, 2026.
This decision stems from the program's struggle to cope with a deluge of low-quality reports, many of which are suspected to be generated by artificial intelligence. These automated submissions have placed an undue burden on the engineers and maintainers responsible for triaging and verifying potential security issues. The program was initially launched in 2022 to incentivize the discovery of vulnerabilities in Google's open-source ecosystem.
While submissions made before the October 1 deadline are unaffected, the pause signifies a broader challenge faced by the cybersecurity community. Google has indicated that it may still accept product vulnerability reports for certain Google Cloud repositories through its separate Cloud VRP, provided they impact Cloud products. However, the OSS VRP itself is undergoing a reevaluation.
Google has committed to addressing the issue and plans to provide an update on the future of the OSS VRP in the first quarter of 2027. In the interim, security researchers are being directed to other Google vulnerability programs, such as the Patch Rewards Program, which focuses on rewarding security improvements to open-source projects rather than specific product vulnerabilities.
The reward structure for the OSS VRP, which previously offered varying amounts based on the severity and tier of the project, now lists no specific monetary rewards for product vulnerabilities across its four project tiers. This change, coupled with the submission pause, suggests a significant shift in how Google is managing its open-source security efforts.
This move by Google follows months of growing complaints from open-source maintainers and other bug bounty programs worldwide. Many have reported a similar increase in AI-assisted or entirely AI-generated vulnerability reports, which often lack the detail, accuracy, or novelty required for effective security analysis. The sheer volume of these submissions consumes valuable time and resources that could otherwise be dedicated to genuine security research.
The OSS VRP's scope traditionally includes any design or implementation issue in Google's open-source software that substantially affects the confidentiality or integrity of user data. The criteria for accepting reports are typically based on the project's tier and the specific vulnerability subcategory. However, the current influx of invalid reports has rendered these criteria difficult to apply effectively.
As the cybersecurity landscape evolves with the rapid advancement of AI, organizations like Google are grappling with how to leverage AI for security while mitigating its potential misuse. The pause in the OSS VRP highlights the urgent need for better mechanisms to distinguish between genuine security research and automated noise, ensuring that valuable security contributions are not lost in the digital din.
The new article provides further detail on the types of invalid reports Google is seeing, specifically citing AI 'hallucinations' and invented exploit paths as significant burdens on security engineers and open-source maintainers. It also clarifies that while product vulnerability submissions are paused, supply-chain vulnerability reports remain active and in scope for the program.
Google has provided an update on the OSS VRP pause, stating that they will continue to reformat and work on the program and commit to giving an update in Q1 2027. While product vulnerability submissions are paused, the company noted that this change does not affect product vulnerabilities submitted before October 1, 2026, and that some reports may still be eligible through the Cloud VRP for Google Cloud repos. Researchers are encouraged to explore Google's other vulnerability reward programs, such as the Patch Rewards Program, for alternative avenues to submit their findings.
The pause in Google's open source bug bounty program, OSS VRP, is attributed to a significant increase in automated submissions, the vast majority of which are invalid. This situation mirrors past instances, such as curl ending its HackerOne program due to low-quality, AI-generated reports overwhelming its security team. The current pause allows Google to implement stricter controls and potentially leverage AI for validation, aiming to streamline the process for legitimate researchers while preventing engineers from wasting time on non-issues.
Google has updated the rules for its Open Source Software Vulnerability Reward Program (OSS VRP) to reflect the pause in rewards for product vulnerabilities, removing specific monetary reward amounts for these types of flaws. The program now commits to an update in the first quarter of 2027, indicating a significant rework is underway to address the surge in invalid, automated reports, which are suspected to be AI-generated. While product vulnerability rewards are suspended, rewards for supply chain compromises and other security issues remain active.
The article elaborates on the "AI slop" issue, detailing how the surge in automated, low-quality submissions has increased manual triage labor for organizations. It highlights research suggesting that attackers could weaponize this "slop" to overwhelm vendors. The piece also provides examples from Daniel Stenberg of curl and Linux kernel maintainers, who have also reported similar challenges with an unmanageable volume of bug reports, some of which are AI-generated.