
Gartner Framework Offers 4 Pillars for Effective Exposure Prioritization
Gartner's new exposure prioritization framework emphasizes threat intelligence, asset context, exploitability modeling, and security control validation to move beyond CVSS scores and reduce breach risk.
Organizations are struggling to effectively manage their vulnerability backlogs, often remediating thousands of exposures with little measurable impact on actual breach risk. A new framework from Gartner highlights a critical shift away from traditional severity-based prioritization, arguing that fewer than 10% of vulnerabilities are actually exploited. The report champions a four-pillar approach to exposure prioritization, designed to align remediation efforts with genuine threats and business impact, moving beyond the limitations of the Common Vulnerability Scoring System (CVSS).
The traditional reliance on CVSS scores, while once a rational approach, is no longer sufficient in today's rapidly evolving threat landscape. Gartner points to several factors contributing to this inadequacy: legacy metrics that reward auditable compliance over actual risk, persistent compliance pressures, and fragmented ownership structures within organizations. This combination often leads to "prioritization paralysis," where significant resources are expended on vulnerabilities that attackers are unlikely to target, while more critical exposures are overlooked. The result is a disconnect between remediation activity and actual risk reduction.
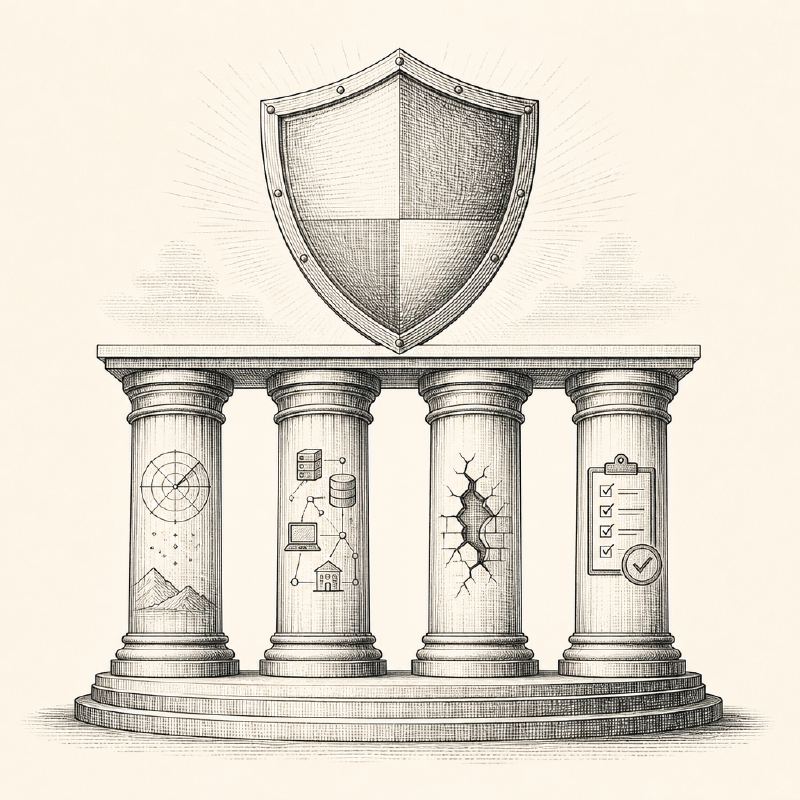
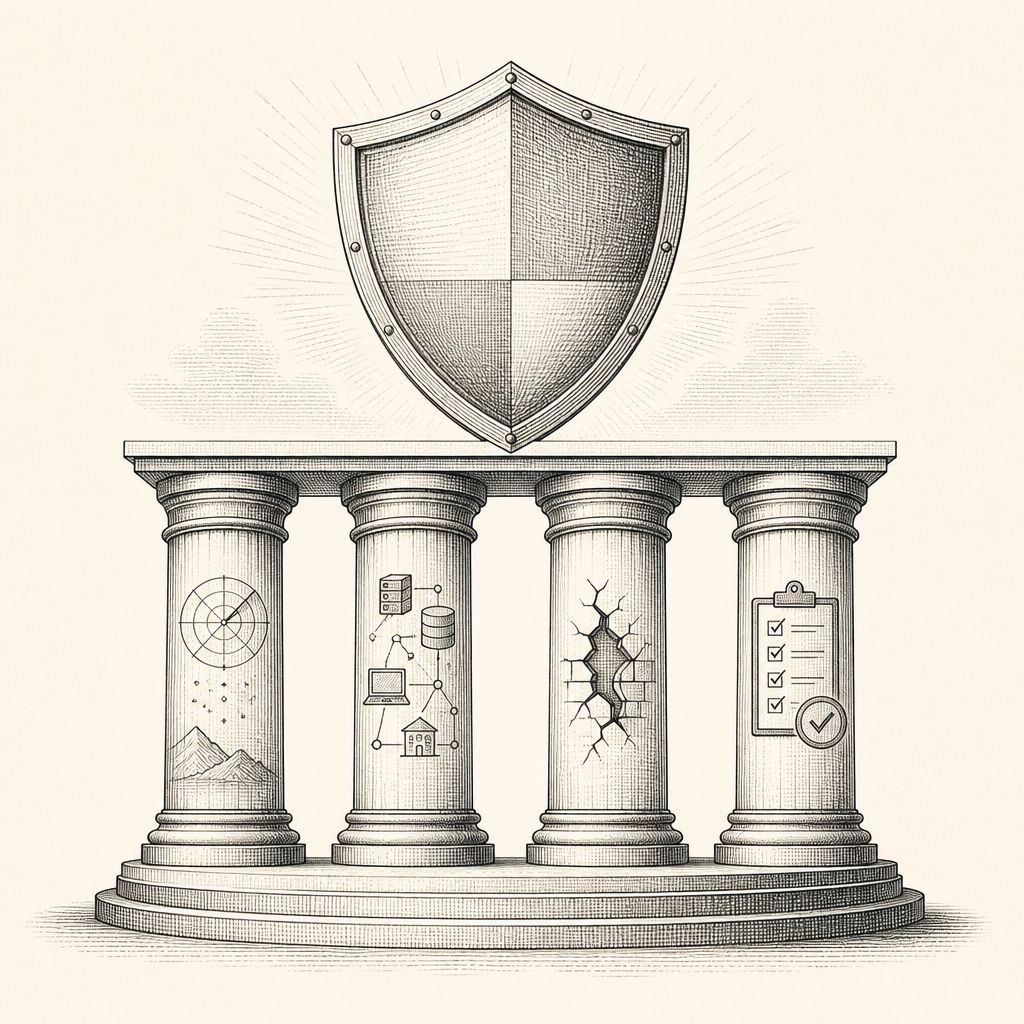
Gartner's proposed framework is built upon four interconnected elements, each answering a crucial question about a given exposure. The core principle is that an exposure warrants urgent remediation only when all four elements converge, indicating a high likelihood of exploitation and significant potential impact. This integrated approach directly supports the principles of Continuous Threat Exposure Management (CTEM) by ensuring that remediation efforts are validated against real-world context before resources are mobilized.
The first pillar, Threat Intelligence, introduces the adversary's perspective. By analyzing which vulnerabilities are actively being exploited in the wild, security teams can identify a subset of high-risk exposures that might otherwise be lost in a large backlog. This intelligence helps focus remediation on vulnerabilities that attackers are demonstrably targeting, often including moderately-rated flaws that are easier to weaponize or affect widely deployed systems. The operational challenge lies in the speed of intelligence dissemination and its timely application to testing and remediation workflows.
Element two, Asset Context and Business Criticality, addresses the impact of a vulnerability. An exploitable flaw becomes a material risk only when it affects an asset crucial to business operations, handles sensitive data, or serves as a pivot point to more valuable systems. Without this context, all assets are treated equally, potentially diverting attention from critical "crown jewel" exposures. Unifying and maintaining current asset inventory data from various sources like CMDBs and cloud security platforms is key to operationalizing this pillar.
Exploitability Modeling, the third element, uses predictive models like the Exploit Prediction Scoring System (EPSS) to estimate the likelihood of a vulnerability being exploited. These models analyze factors such as exploit complexity, component prevalence, and the time between disclosure and observed exploitation. While EPSS can identify latent risks and help teams anticipate threats, Gartner emphasizes that it provides a general statistical likelihood. True validation of exploitability within an organization's specific environment is still necessary.
The final and often missing pillar is Security Control Validation. This element assesses an exposure against the existing defenses, such as network segmentation, endpoint protection, and identity controls. A vulnerability that appears critical on paper might be effectively mitigated by strong security controls, rendering it practically unreachable for attackers. Conversely, a less severe vulnerability on a poorly protected asset could pose a greater risk. Ignoring control context leads to an overestimation of risk and inefficient remediation efforts, Gartner warns.
By integrating these four elements—threat intelligence, asset context, exploitability modeling, and security control validation—organizations can move beyond the limitations of CVSS scores. This comprehensive approach promises to significantly reduce breach likelihood by focusing resources on the exposures that pose the most immediate and substantial threat, thereby optimizing security investments and reducing remediation fatigue.