
Fortinet FortiOS SSLVPN Vulnerable to Man-in-the-Middle Attacks
A critical vulnerability in FortiOS SSLVPN allows unauthenticated remote attackers to conduct Man-in-the-Middle attacks by exploiting improper certificate validation.
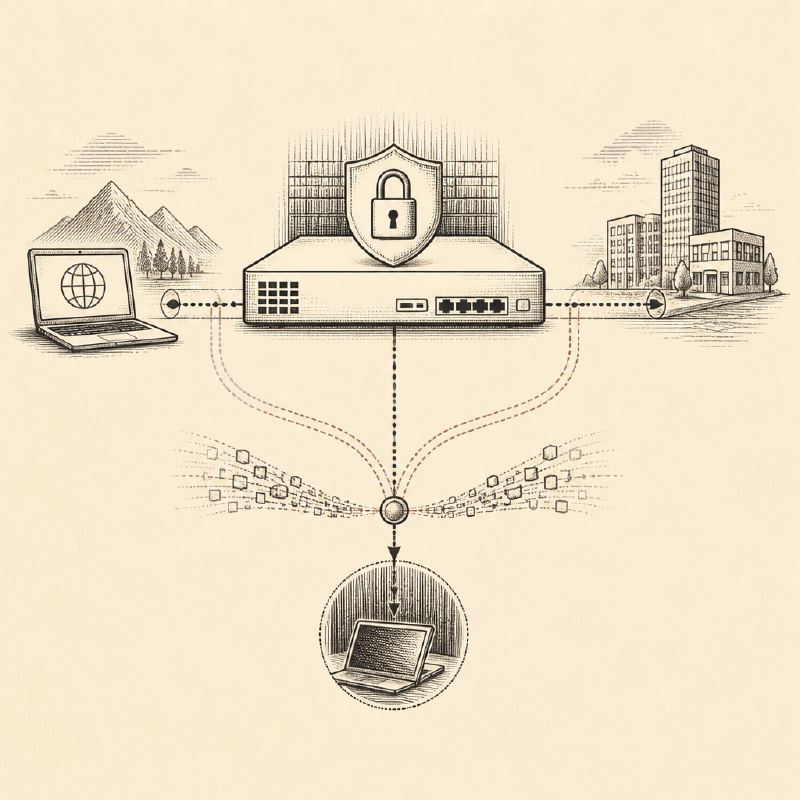
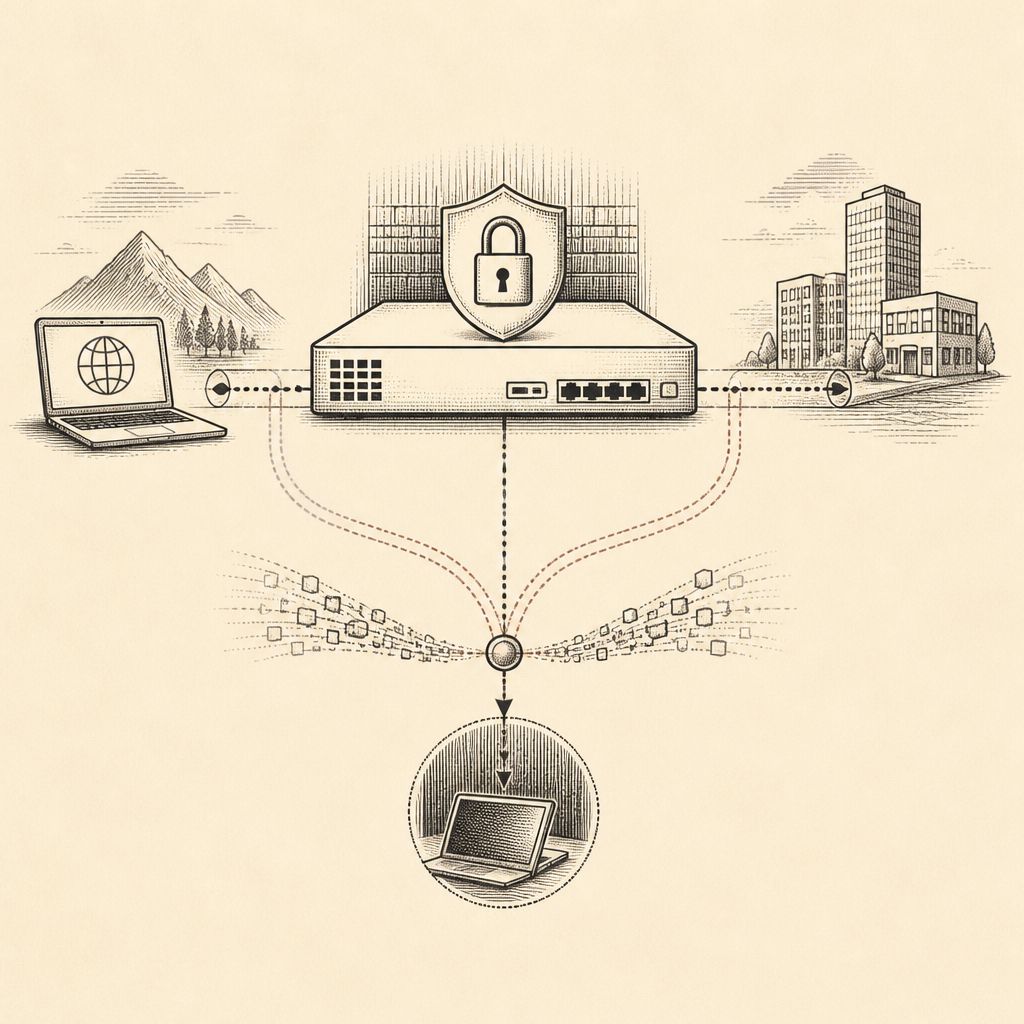
Fortinet has issued a security advisory detailing a critical vulnerability, identified as CWE-295, within its FortiOS SSLVPN feature. This flaw, which carries a CVSSv3 score of 7.7, permits unauthenticated remote attackers to execute Man-in-the-Middle (MitM) attacks. The vulnerability specifically targets the communication channel established between the SSLVPN web portal and the backend destination websites.
The core of the issue lies in the improper validation of certificates. When the SSLVPN attempts to establish a secure connection to a backend service, it fails to adequately verify the authenticity of the server's certificate. This oversight creates an opening for an attacker to intercept and potentially alter the traffic flowing between the VPN client and the intended destination. By presenting a fraudulent certificate, an attacker could trick the SSLVPN into establishing a connection with them instead of the legitimate backend server.
Successful exploitation of this vulnerability could have significant consequences for organizations relying on Fortinet's SSLVPN for secure remote access. An attacker capable of performing a MitM attack could eavesdrop on sensitive communications, steal credentials, inject malicious content into legitimate traffic, or redirect users to phishing sites. The unauthenticated nature of the exploit means that an attacker does not need prior access or credentials to initiate the attack, making it a particularly dangerous threat.
Fortinet has identified a broad range of affected FortiOS versions, spanning from 6.4.0 through 7.6.4, and including various releases in the 7.0, 7.2, and 7.4 branches. This wide impact underscores the importance for organizations to promptly assess their FortiOS deployments and apply the necessary patches. The advisory was initially published on November 10, 2026, with an update on November 12, 2026, providing further details on fix behavior across different software branches.
The vulnerability was discovered and reported internally by John Headley of the Fortinet System Engineering team. While the advisory does not explicitly mention active exploitation in the wild, the severity and nature of the flaw suggest a high potential for exploitation by malicious actors. Organizations are strongly advised to consult the official Fortinet advisory for specific remediation steps and to prioritize patching affected systems.
This incident highlights the ongoing challenges in securing VPN solutions, which often serve as a critical gateway into an organization's internal network. Proper certificate validation is a fundamental security control, and its failure can lead to severe breaches. Fortinet's advisory, FG-IR-26-193, provides the necessary information for customers to protect themselves against this critical flaw.