
Fortinet Advisory Details Authorization Bypass Flaw in FortiManager and FortiAnalyzer
Fortinet has issued a security advisory for an authorization bypass vulnerability in its FortiManager and FortiAnalyzer products, allowing authenticated administrators to access unauthorized VDOMs.
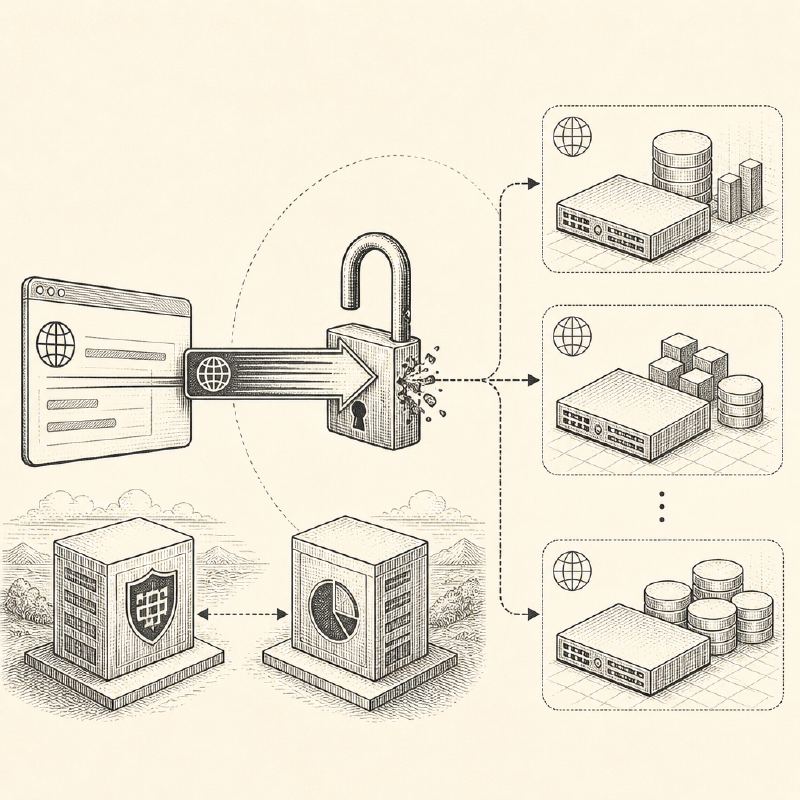
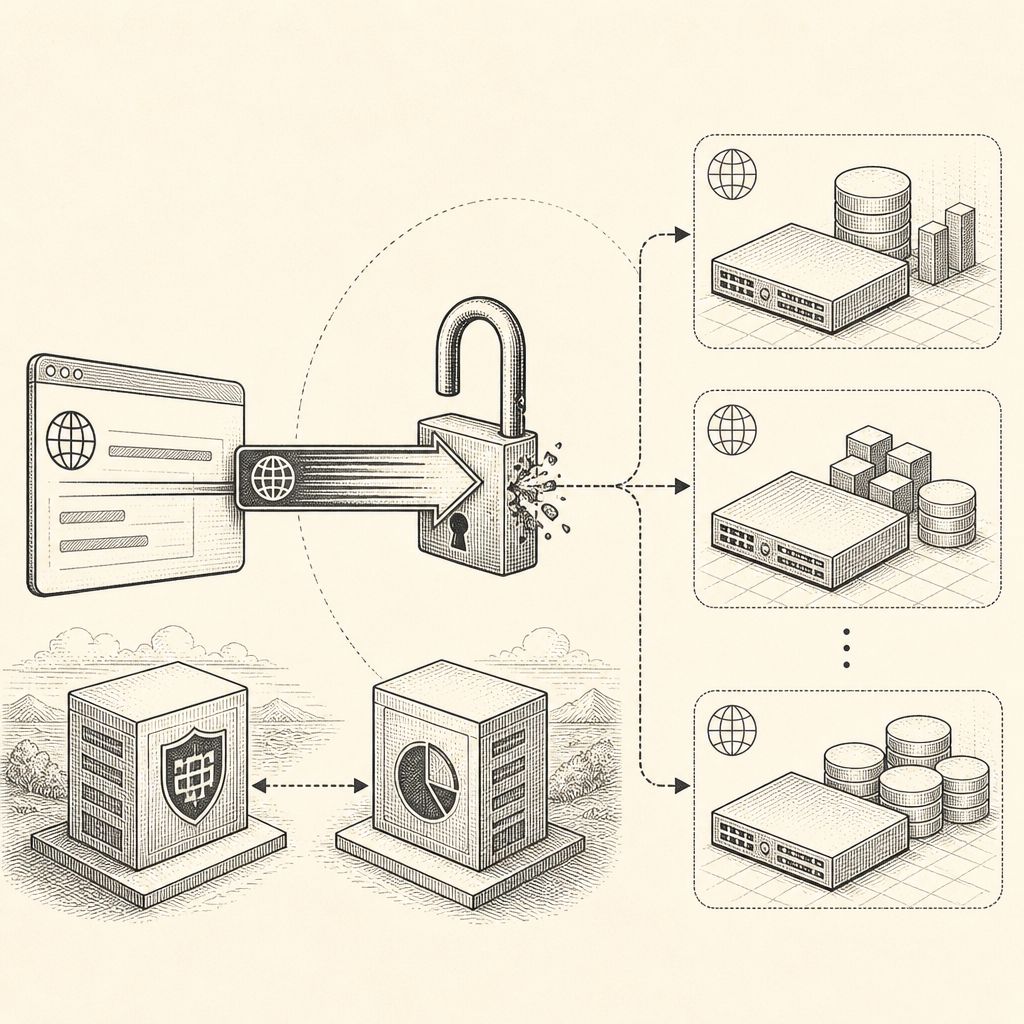
Fortinet has released a security advisory detailing an authorization bypass vulnerability, identified as CWE-639, within its FortiManager and FortiAnalyzer product lines. The flaw, assigned the identifier FG-IR-26-244, carries a CVSSv3 score of 9.1, indicating a critical severity.
The vulnerability stems from an improper access control mechanism within the dmserver component. Specifically, an authenticated administrator could exploit this flaw by sending specially crafted HTTP requests. This allows them to bypass intended access restrictions and gain entry to other Virtual Domains (VDOMs) that they should not have permission to view or manage.
This security issue affects a wide range of versions for both FortiManager and FortiAnalyzer, including their cloud-based counterparts, FortiManager Cloud and FortiAnalyzer Cloud. The advisory lists numerous affected versions, from FortiAnalyzer 7.2.0 up to 8.0.1 and corresponding cloud versions, highlighting the broad potential impact across customer deployments.
The vulnerability was discovered internally by Loic Pantano of the Fortinet Product Security team, who utilized the "Claude Mythos" AI model in their research. This internal discovery suggests a proactive approach by Fortinet to identify and address potential security weaknesses before they are exploited by external threat actors.
While the advisory does not detail specific exploitation scenarios or in-the-wild activity, the critical CVSS score and the nature of the vulnerability (authorization bypass) suggest a significant risk. Unauthorized access to VDOMs could lead to data exposure, configuration manipulation, or further compromise of network security controls managed by these devices.
Fortinet has provided a comprehensive list of affected versions in its advisory, which serves as the primary resource for customers to identify their exposure. Users are strongly encouraged to consult the advisory and apply necessary updates or mitigations to protect their environments. The advisory itself is published under the CVRF (Common Vulnerability Reporting Format) standard, facilitating easier integration into security management tools.
As of the advisory's publication date, no specific workarounds or patches are explicitly mentioned beyond the implication that updating to a non-vulnerable version is the recommended course of action. Organizations utilizing FortiManager or FortiAnalyzer should prioritize reviewing their deployed versions against the advisory's list and plan for timely updates to remediate this critical security risk.
The advisory for FG-IR-26-229, updated on November 10, 2026, details an authentication bypass by spoofing vulnerability affecting multiple FortiAnalyzer and FortiManager products, including cloud and BigData variants. This flaw, rated with a CVSSv3 score of 8.2, could allow an attacker to disrupt the High Availability (HA) state of these devices. The vulnerability was discovered internally by a Fortinet Product Security team member.
This advisory updates the initial publication by detailing the specific products affected, including various versions of FortiManager, FortiManager Cloud, and FortiSASE-Sovereign GUI. The vulnerability, identified as CWE-639, allows authenticated attackers to bypass authorization controls and execute commands outside their intended scope through crafted HTTP requests, carrying a CVSSv3 score of 8.7.